
Three Organizations, One Initiative
Three organizations each have one job, and that separation is why an SCR certification can be trusted.

The SCF Council writes the content. It owns the control set, the body of knowledge and the assessment guides, but it does not accredit assessors or issue certifications.
The Cyber AB is the Accreditation Body for the SCR CAP and the same body that operates in the CMMC ecosystem. It decides who is qualified to assess and support organizations, and it lists them in the SCF Marketplace.

The Cyber EF is an entity of The Cyber AB dedicated to sustained engagement with CMMC and SCF stakeholders through training, education, outreach and market facilitation.
Individual certifications sit with SAICO, the SCR Assessor and Instructor Certification Organization.
Built For The Requirements You Can't See Yet
CMMC, HIPAA, GDPR, the EU AI Act, NIS2, PCI DSS: each arrives with its own language, deadlines and assessors. Standing up a separate program for each one is how compliance becomes fragile. With a Living Control Set (LCS), the next mandate, whether it covers Artificial Intelligence (AI), Zero Trust (ZT), Post-Quantum Cryptography (PQC), Supply Chain Risk Management (SCRM) or Operational Technology (OT), is absorbed into the controls you already operate.
Implement Once
Controls are built against the SCF's common control set, not one regulation at a time.
Absorb What Comes Next
New requirements map onto controls you already run, so a new mandate becomes an update to today's program.
Prove Several At Once
A Common Controls Framework® (CCF)-based LCS can be third-party validated against multiple laws, regulations and frameworks in the same assessment.
The Goal
Build to scale for requirements you cannot see yet, adapt with minimal disruption, and give auditors, regulators and customers assurance that your processes are secure, compliant and resilient.
Certification For Organizations And Professionals
SCR certification works at two levels: organizations earning a third-party validated designation, and professionals proving they can implement and assess the SCF.
Company-Level SCR Certifications
It is possible to become certified using SCF controls. For example, SCR Certified for NIST CSF 2.0, SCR Certified for HIPAA Security Rule and more. This is all part of the SCR Conformity Assessment Program (SCR CAP). The SCR CAP leverages the SCF's metaframework structure and no-cost content to make conformity assessments more cost-effective, efficient, and objective.
Available certifications include: NIST SP 800-171 R3, NIST Cybersecurity Framework 2.0 (NIST CSF 2.0), NY DFS 23 NYCRR Part 500, HIPAA Security Rule (NIST SP 800-66 R2), NIST SP 800-161 R1, SCF CORE Fundamentals and CMMC Level 1.
Individual-Level SCR Certifications
The SCR Assessor and Instructor Certification Organization (SAICO) is a separate entity responsible for individual-level certification and training within the SCR CAP Ecosystem. SAICO provides three certification programs that equip cybersecurity professionals with the expertise to evaluate and implement SCF controls effectively. Each course uses Computer-Based Training (CBT), enabling self-paced learning.
Three Certification Tracks:
- SCR Practitioner, which covers foundation-level understanding of the SCF
- SCR Architect, which covers designing and implementing SCF-based programs
- SCR Assessor, which covers conducting conformity assessments using SCF methodology.
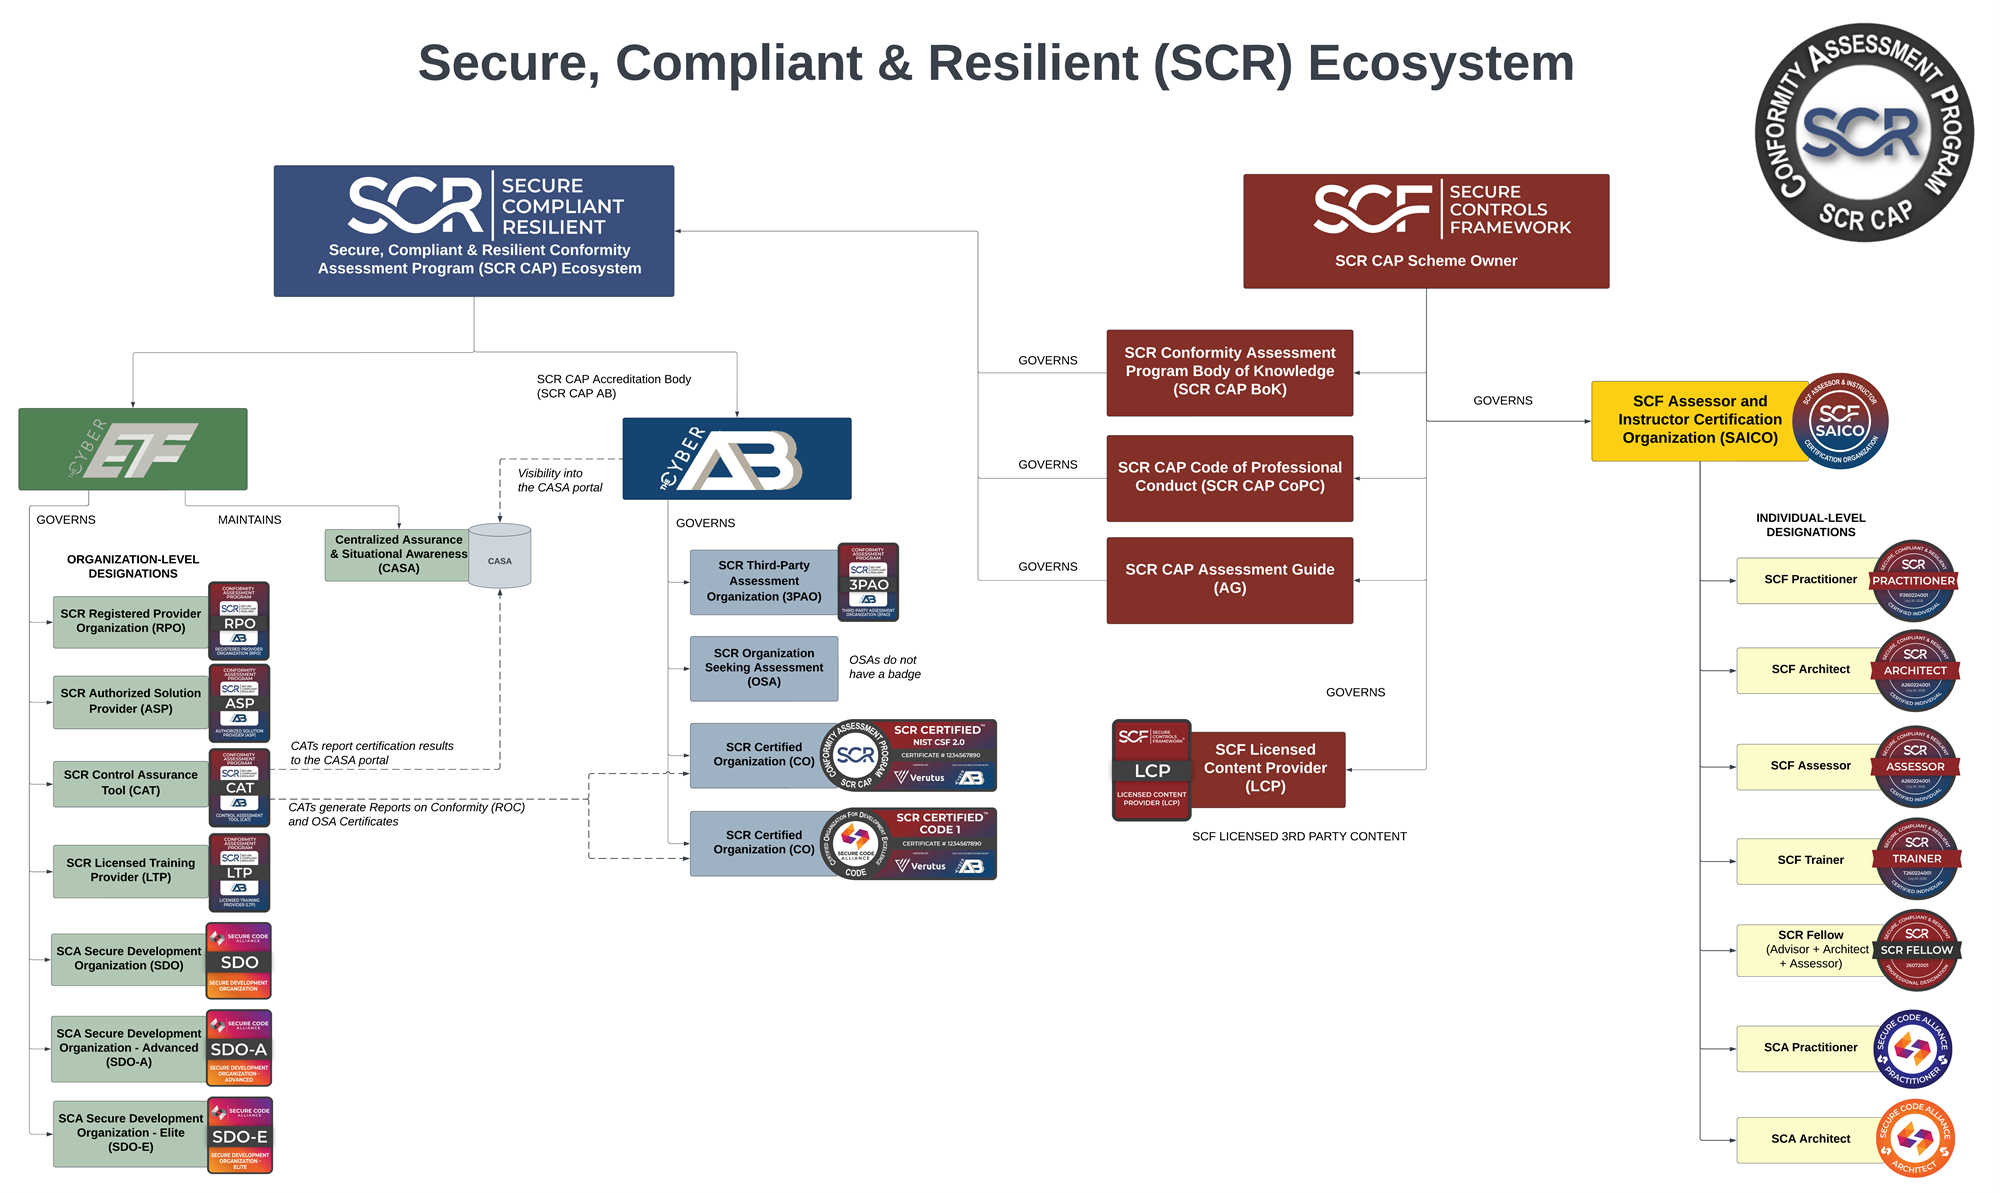
Who Does What In The SCR CAP Ecosystem
Seven roles work under one program, the SCR CAP, which sets the participant roles, assessment standards and certification requirements, with The Cyber AB as its Accreditation Body.
The SCR Ecosystem page is the full reference for who governs what, including The Cyber AB, the Cyber EF, SAICO and the SCF Council.
3PAO
SCR Third-Party Assessment Organizations
Independent assessment organizations accredited to conduct SCR CAP conformity assessments on behalf of organizations seeking certification.
OSA
SCR Organizations Seeking Assessment
The organization pursuing an SCF-based certification, whose security posture and controls implementation is being evaluated but which has not yet completed an SCR CAP conformity assessment.
ASP
SCR Authorized Solutions Providers
Cloud-based platforms and service providers, including CSPs, MSPs and MSSPs, that operate within the defined scope of the SCF and give organizations a structured environment for implementing it.
RPO
SCR Registered Provider Organizations
Consulting and advisory organizations registered to provide SCF implementation, advisory, and assessment preparation services.
CAT
SCR Control Assurance Tools
Governance, Risk and Compliance platforms that specialize in integrating the SCF, so that compliance interpretation and risk management are operationalized inside the tools an organization already runs.
LTP
SCR Licensed Training Providers
Organizations certified by SAICO to deliver approved individual-level certification training programs using SCR Trainers.
LCP
SCF Licensed Content Providers
Organizations authorized by the SCF Council to create derivative SCF content, such as SCF-based policies, standards and procedures.
CAP
SCR Conformity Assessment Program
The program framework that governs all ecosystem participant roles, assessment standards, and certification requirements. Accreditation Body: The Cyber AB.
Three Professional Certification Tracks
A living control set needs people who can build it, run it and assess it.
The SCR Assessor and Instructor Certification Organization (SAICO) provides three Computer-Based Training (CBT) certification programs. Each follows a defined syllabus to meet the specific learning objectives and standards of the certification track.
SCR Practitioner
Foundation Level: The entry-point certification for cybersecurity professionals who work with the SCF. Covers the structure and application of the SCF, its control domains, and how to use the framework as a practitioner implementing or managing a security program. Self-paced CBT with defined syllabus, SAICO-certified.
SCR Architect
Design & Implementation: For cybersecurity professionals who design and implement security programs using the SCF. Covers program architecture, control selection and rationalization, SCF implementation, and the SCRMS operational model. Self-paced CBT with defined syllabus, SAICO-certified.
SCR Assessor
Assessment & Audit: The advanced certification for professionals who conduct conformity assessments using the SCF methodology. Covers assessment planning, examine-interview-test methodology, evidence evaluation, and SCR CAP assessment procedures. Self-paced CBT with defined syllabus, SAICO-certified.
Where To Go From Here
Where you start depends on how far along your program is. Most organizations begin with one of these three steps.
Start With The SCF
The SCF is free to download. It gives you the full control set and its mappings to the laws, regulations and frameworks you already report against.
Plan For Certification
The SCR CAP page walks through both phases of certification, from your self-assessment to the third-party assessment that leads to the SCR Certified™ designation.
Find A Provider
The SCF Marketplace, run by The Cyber AB, lists the assessors, consultants, solution providers and GRC platforms that work in the SCR CAP ecosystem.