
What Is The Cyber EF?
An accreditation body has a narrow job. It sets a standard, evaluates organizations against it, and grants or withholds accreditation. It is deliberately not in the business of promoting the program or teaching people how to work within it, because those activities sit uncomfortably next to the act of judging.
The Cyber EF exists to do that second set of things. It is an entity of The Cyber AB, and its stated mission is dedication to sustained engagement with CMMC and SCF stakeholders, supporting cybersecurity conformity through continuous engagement: training, education, outreach and market facilitation. Its work covers both the CMMC and the SCF rather than only one.
Currently Being Restructured
The Cyber EF is new and its corporate structure is in the middle of changing. Treat any description of its legal form as provisional until The Cyber AB publishes the new arrangement.
What Does The Cyber EF Do?
The Cyber EF has described four areas of work. Each one addresses a gap that accreditation alone does not close.
Enhanced Practitioner Development
Multi-framework, multi-standard training and credentialing for providers. Accreditation says an organization is qualified. Practitioner development is how its people got there.
Market-Making
A trusted marketplace that distinguishes vetted services and products, including AI, so that finding a qualified provider is a usable process rather than a long list.
Implementation Guidance
A living knowledge base defining what secure means across the ecosystem, built and maintained with government, partners and industry experts between formal releases.
Program Engagement
Stakeholder groups shaping new requirements across the whole ecosystem, so the organizations that have to meet a requirement have a hand in writing it.
One Ecosystem, Connected End To End
The Cyber EF describes its remit as assurance that holds every partner to the same standard, across six groups that span both the CMMC and SCF ecosystems.
Defense Industrial Base
Contractors and subcontractors working toward CMMC certification.
Advisory & Implementation
RPOs, MSPs, MSSPs, CSPs and vendors preparing and sustaining conformance.
Public & Private Industries
Extending cyber-hygiene practices to critical infrastructure.
Governments
Aligning policy, oversight and adoption with the DoD and others.
CMMC
Training, knowledge base and marketplace for the ecosystem.
SCF
The same support, extended to the Secure Controls Framework®.
Trust, Extended Upstream
Today, CMMC certifies the organization being assessed. The Cyber EF is extending that same rigor upstream, adding certification requirements for the advisors and implementers guiding organizations, and for the vendor products they rely on, including AI.
Advisory Services
Certification requirements for the advisors guiding organizations toward conformance.
Implementation Services
Certification requirements for the implementers doing the work alongside them.
Vendor Products
Certification requirements for the vendor products organizations rely on, including AI.
In The Cyber EF's Own Words
“We're adding real requirements, for the advisory and implementation providers guiding organizations, and for the vendor products they rely on, including AI. That's how we build trust across the whole ecosystem, not just at the assessment.” Mike Snyder, Executive Director, The Cyber EF.
What Is The Cyber EF's Relationship To The SCF?
The Cyber EF engages the SCF ecosystem alongside the CMMC ecosystem rather than treating the SCF as a side concern. For an organization pursuing an SCF-based certification, that engagement is the practical route in: the training that produces qualified people, and the marketplace that makes accredited providers findable.
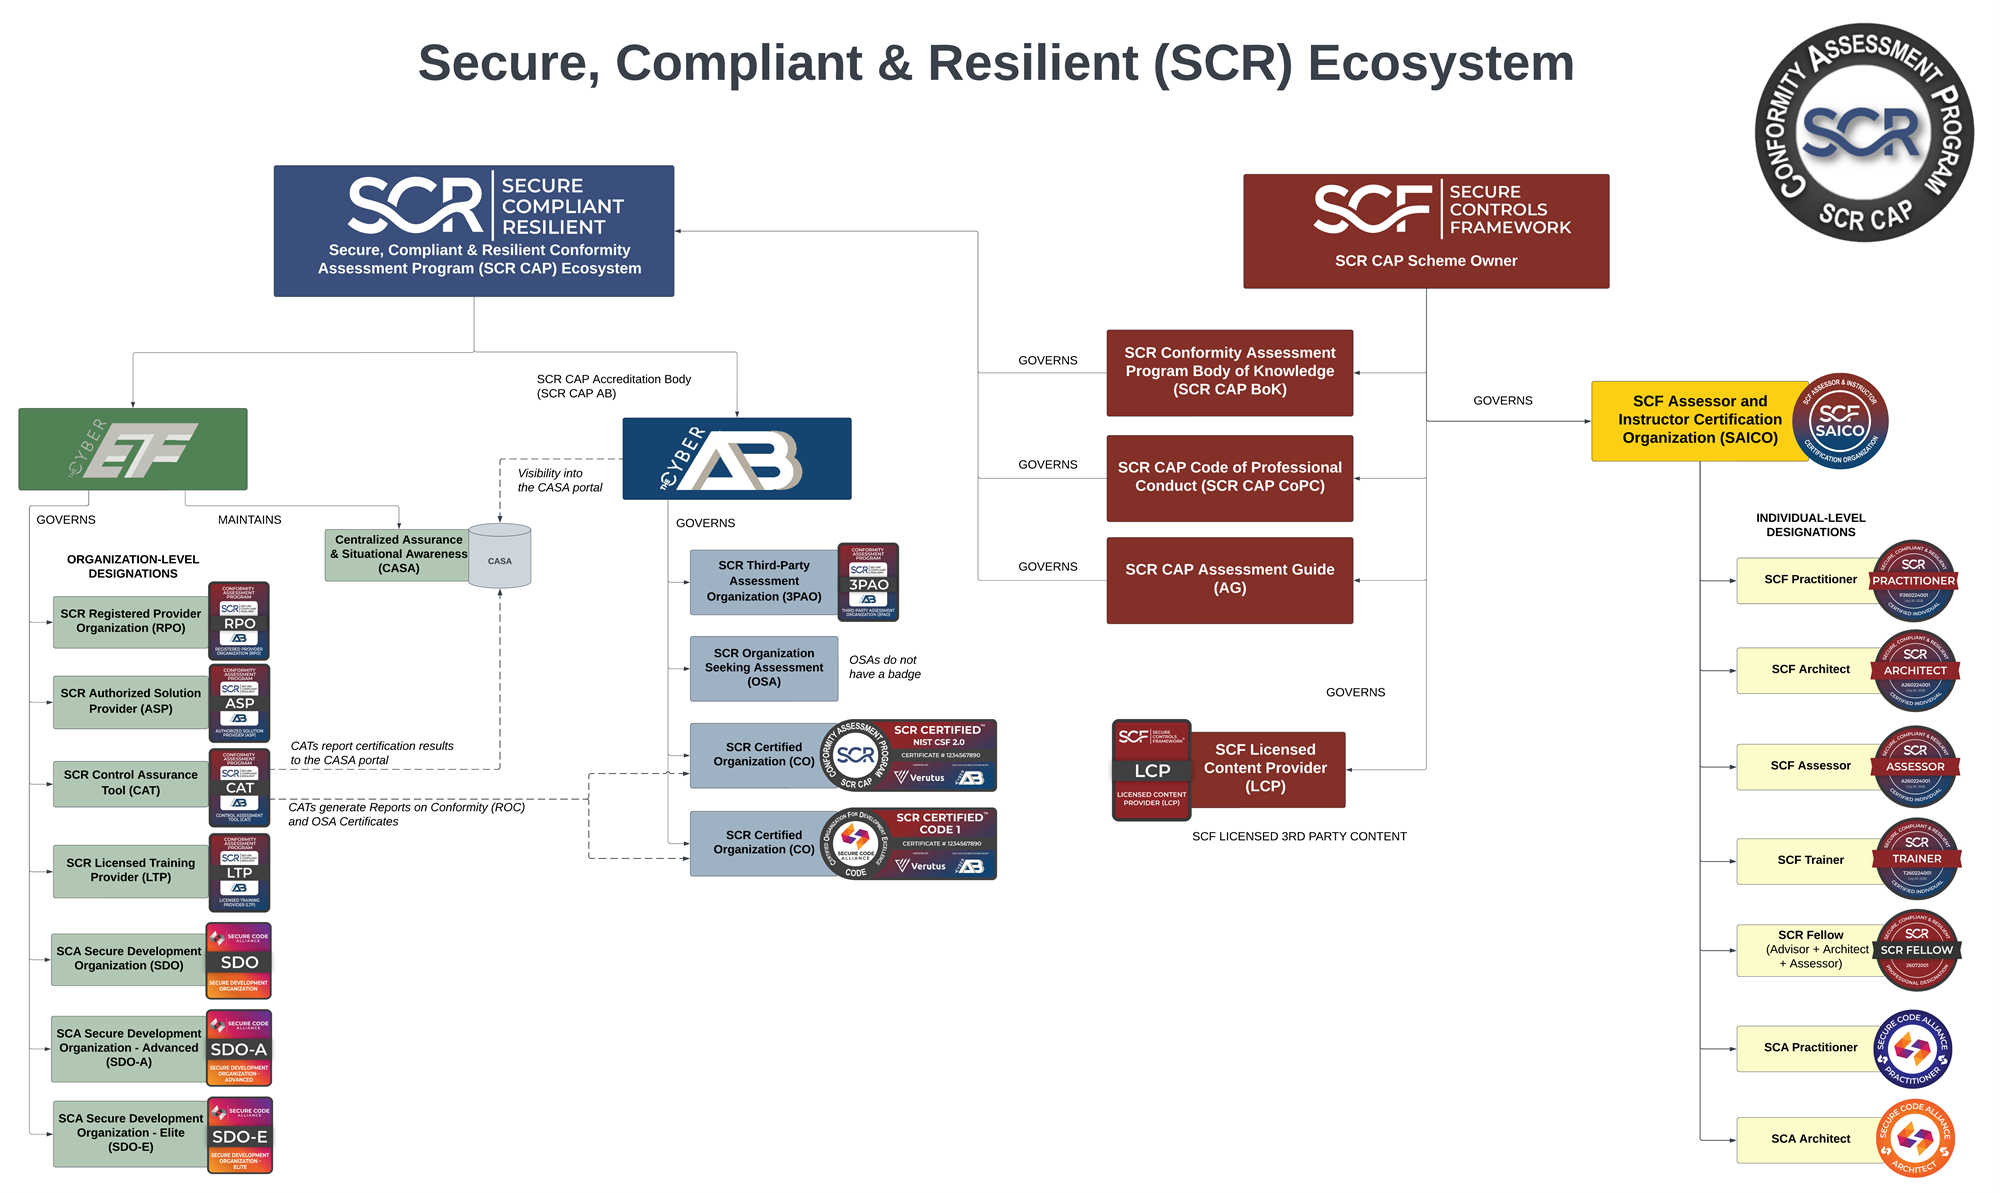
ASP
SCR Authorized Solutions Providers
Cloud-based platforms and service providers, including CSPs, MSPs and MSSPs, that operate within the defined scope of the SCF and give organizations a structured environment for implementing it.
RPO
SCR Registered Provider Organizations
Consulting and advisory organizations registered to provide SCF implementation, advisory, and assessment preparation services.
CAT
SCR Control Assurance Tools
Governance, Risk and Compliance platforms that specialize in integrating the SCF, so that compliance interpretation and risk management are operationalized inside the tools an organization already runs.
LTP
SCR Licensed Training Providers
Organizations certified by SAICO to deliver approved individual-level certification training programs using SCR Trainers.
Where Individual Certification Sits
Individual certification sits with SAICO. See the SCR Ecosystem page for the current division of responsibility across the three governing bodies.