
What Is an SCR Assessor?
SCR Assessors are SAICO-certified individuals qualified to participate in and/or lead SCR Third-Party Assessment Organization (3PAO) assessment teams, conducting SCR CAP conformity assessments that evaluate an organization’s cybersecurity and data protection controls against defined Assessment Objectives (AOs).
- SCR CAP assessment methodology and process
- Examine, interview, and test (EIT) assessment techniques
- Evidence collection, evaluation, and documentation
- Assessment Objective (AO) evaluation procedures
- SCR CAP report writing and findings documentation
- Roles and responsibilities within the SCR CAP Ecosystem
What the SCR Assessor Certification Covers
The SCR Assessor curriculum is built around the SCR CAP assessment methodology, the examine, interview, and test (EIT) approach that assessors use to evaluate whether organizations have properly implemented the controls required for their selected SCR CAP certification.
SCR CAP Assessment Methodology
The examine, interview, and test (EIT) methodology that underpins all SCR CAP conformity assessments. Covers how to plan, scope, execute, and document assessments in accordance with SCR CAP requirements.
Assessment Objective (AO) Evaluation
How to evaluate each Assessment Objective to determine whether the control is appropriately designed, properly implemented, and producing the desired security outcome. Covers conformity vs. non-conformity determinations.
Evidence Collection & Evaluation
Techniques for collecting, reviewing, and evaluating evidence during SCR CAP assessments. Covers what constitutes acceptable evidence, how to evaluate documentation quality, and how to conduct interviews and tests.
Assessment Reporting & Findings
How to document assessment findings, write conformity/non-conformity determinations, and produce SCR CAP assessment reports that meet program requirements.
3PAO Roles & Responsibilities
Roles and responsibilities of SCR Assessors within a 3PAO team, including team lead vs. team member responsibilities, conflict of interest requirements, and the relationship to the Cyber AB accreditation body.
SCR CAP Program Requirements
The complete SCR CAP program structure, including how to select applicable Minimum Security Requirements (MSR) for each certification track, how to interpret assessment guides, and how risk tolerance affects assessment scoping.
The SCR Assessor Role in the CAP Ecosystem
The SCR Assessor is the evaluation layer of the SCR CAP Ecosystem. Assessors perform the independent, third-party conformity assessments that produce the SCR Certified™ designation. They operate within authorized 3PAOs and are directly accountable to The Cyber AB’s accreditation standards.
Unlike Practitioners (who implement) and Architects (who design), Assessors must maintain independence from the organizations they assess. This independence is a core requirement of the SCR CAP program and is enforced through 3PAO accreditation standards.
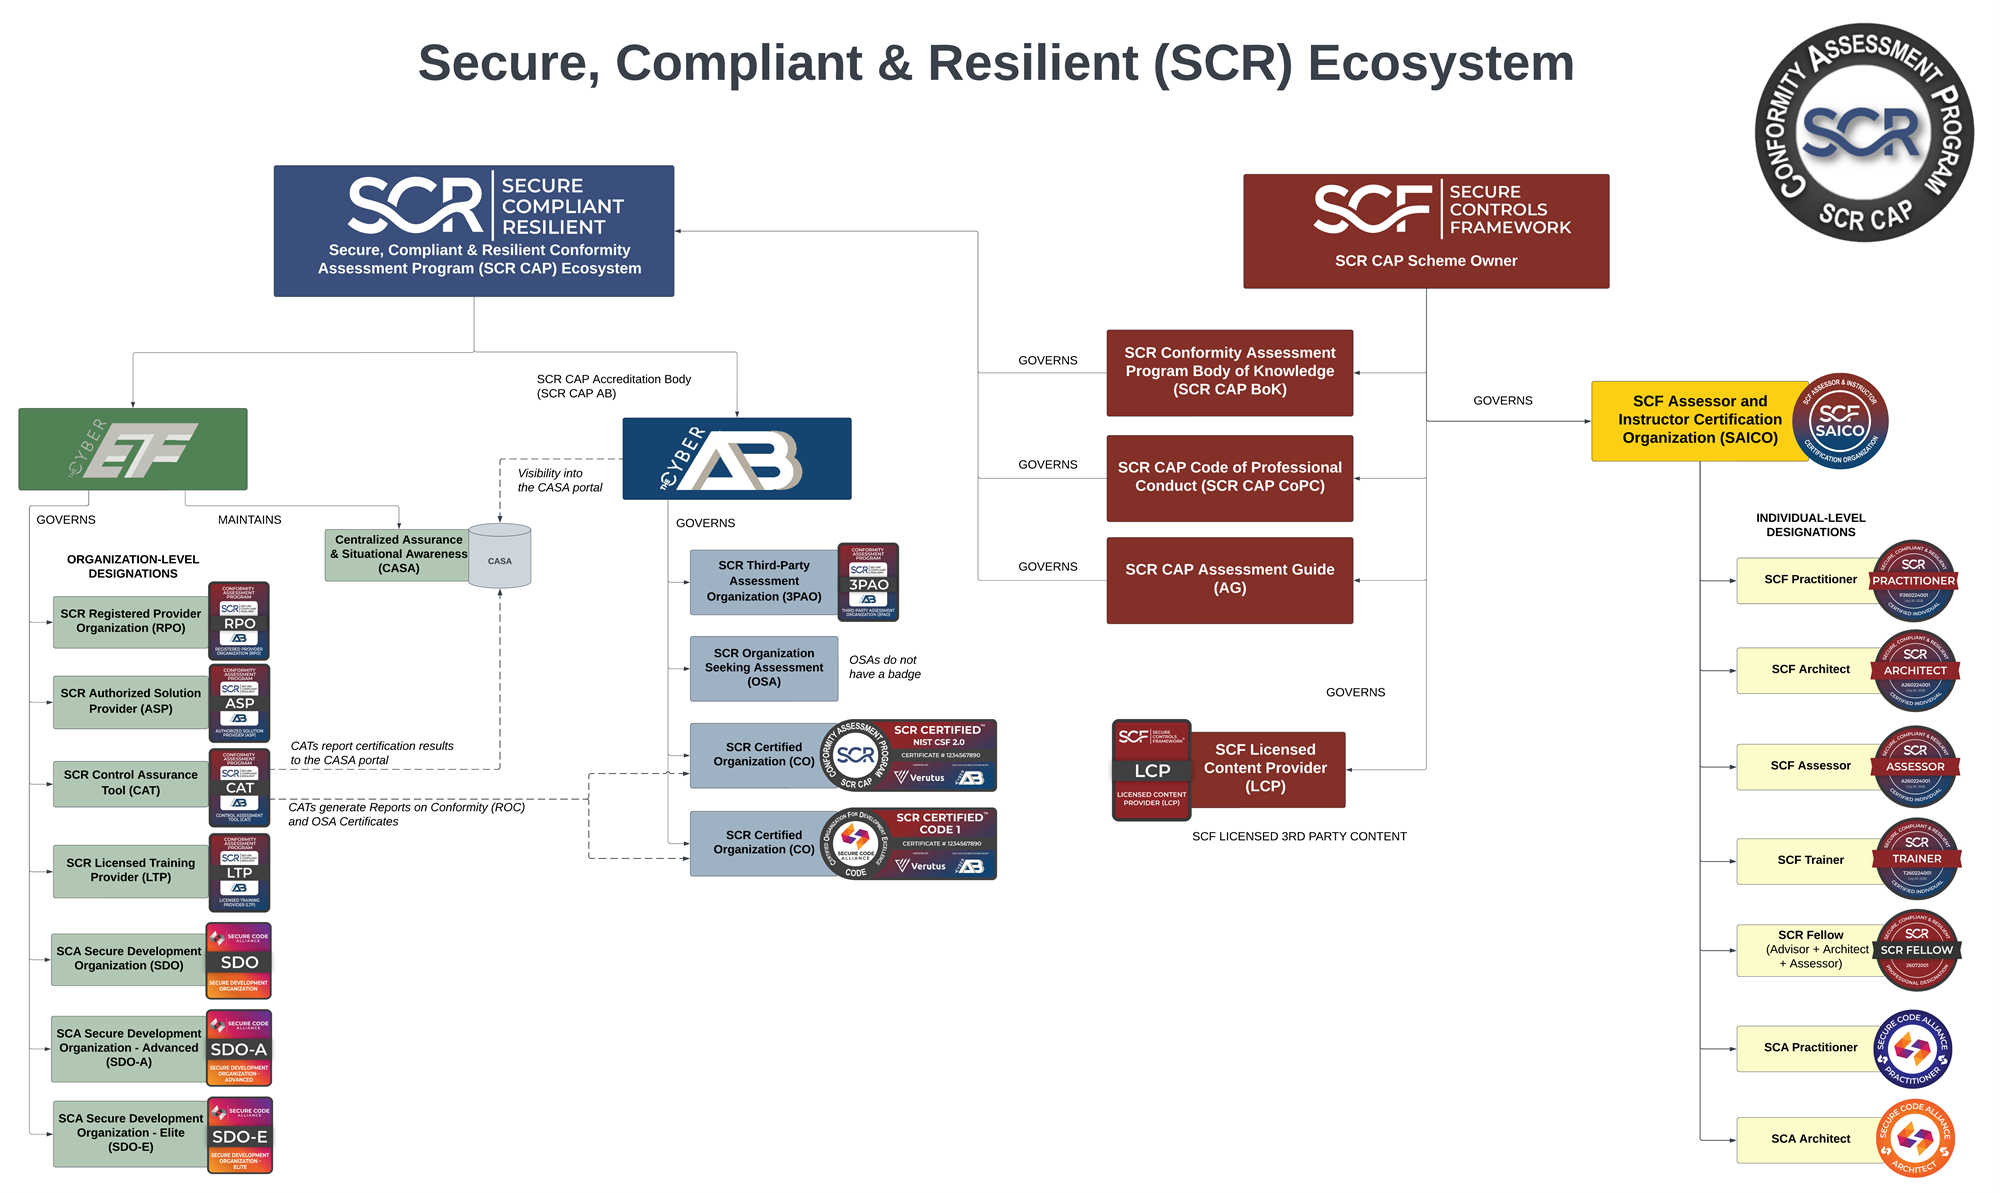
The Complete SAICO Certification Path
The SCR Assessor is the advanced and final track in the three-level SAICO certification path. It requires the foundational and intermediate knowledge built through the Practitioner and Architect tracks.
SCR Practitioner
Foundation: Step 1. Implement and maintain SCF controls. Foundation understanding of SCF structure, domains, and the SCF.
SCR Architect
Intermediate: Step 2. Design and architect SCF-based programs. Control selection, SCRMS implementation, and strategic alignment.
SCR Assessor
Advanced: Current. Lead SCR CAP assessment teams within a 3PAO. Evaluate controls against AOs. Conduct independent conformity assessments.
