Three Organizations, One Initiative
If a certification is going to hold up with a regulator or a customer, nobody should grade their own work.
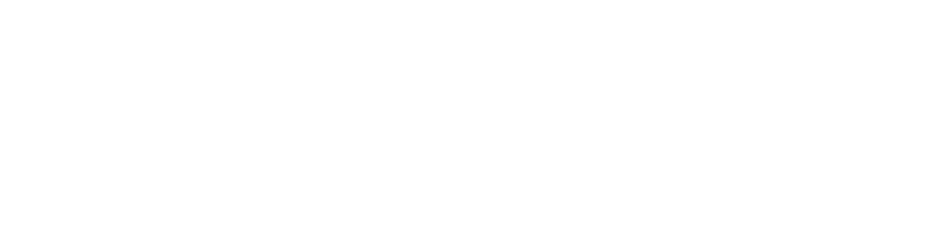
The SCF Council writes the content. It owns the control set, the body of knowledge and the assessment guides, but it does not accredit assessors or issue certifications.
The Cyber AB is the Accreditation Body for the SCR CAP and the same body that operates in the CMMC ecosystem. It decides who is qualified to assess and support organizations, and it lists them in the SCF Marketplace.

The Cyber EF is an entity of The Cyber AB dedicated to sustained engagement with CMMC and SCF stakeholders through training, education, outreach and market facilitation.
Individual certifications sit with SAICO, the SCR Assessor and Instructor Certification Organization.
Why Independence Is Built In
A certification is only worth what its independence is worth. If the same organization wrote the control set, trained the assessors, accredited the assessment firms and issued the certificates, the result would carry very little weight with a regulator or a customer.
The SCR CAP Ecosystem separates those functions. The SCF Council owns the content. The Cyber AB accredits the organizations that perform and support assessments, and the Cyber EF, an entity of The Cyber AB, supports them through training, education, outreach and market facilitation. SAICO certifies the individuals who do the work and the providers who train them.
The Cyber AB & Cyber EF
The Cyber AB accredits the organizations in the ecosystem, from assessment firms to the platforms and providers that support them. The Cyber EF engages and develops that community.
SAICO
Certifies individuals and licenses the organizations that deliver approved training.
The SCF Council
Owns the authoritative content: the body of knowledge, the assessment guides, and the licensing of derivative SCF content.
The Cyber AB & Cyber EF
If you work in CMMC, you already know The Cyber AB: it is the same body that operates in the CMMC ecosystem. For the SCR CAP it is the Accreditation Body, deciding who is qualified to assess and support organizations. The Cyber EF, its engagement arm, carries training, marketplace development, knowledge building and outreach across both the CMMC and SCF communities. Read more about The Cyber AB and the Cyber EF.
3PAO
SCR Third-Party Assessment Organizations
Independent assessment organizations accredited to conduct SCR CAP conformity assessments on behalf of organizations seeking certification.
ASP
SCR Authorized Solutions Providers
Cloud-based platforms and service providers, including CSPs, MSPs and MSSPs, that operate within the defined scope of the SCF and give organizations a structured environment for implementing it.
RPO
SCR Registered Provider Organizations
Consulting and advisory organizations registered to provide SCF implementation, advisory, and assessment preparation services.
OSA
SCR Organizations Seeking Assessment
The organization pursuing an SCF-based certification, whose security posture and controls implementation is being evaluated but which has not yet completed an SCR CAP conformity assessment.
CAT
SCR Control Assurance Tools
Governance, Risk and Compliance platforms that specialize in integrating the SCF, so that compliance interpretation and risk management are operationalized inside the tools an organization already runs.
LTP
SCR Licensed Training Providers
Organizations certified by SAICO to deliver approved individual-level certification training programs using SCR Trainers.
LCP
SCF Licensed Content Providers
Organizations authorized by the SCF Council to create derivative SCF content, such as SCF-based policies, standards and procedures.
CAP
SCR Conformity Assessment Program
The program framework that governs all ecosystem participant roles, assessment standards, and certification requirements. Accreditation Body: The Cyber AB.
Assessors Cannot Also Advise
The separation between an RPO, which helps you prepare, and a 3PAO, which assesses you, is what keeps the assessment independent. Treat them as distinct engagements.
SCR Assessor and Instructor Certification Organization (SAICO)
The people doing the work need proof of skill too.
SAICO certifies the individuals who implement, design and assess against the SCF, and licenses the organizations approved to train them. Full detail is on the SCR Training and Individual-Level Certifications page.
SCR Practitioner
Certified individuals with the knowledge and skills to implement SCF controls in line with SCF recommended practices and structure, and to maintain an organization's security, compliance and resilience program.
SCR Architect
Certified individuals with the advanced knowledge to architect and design SCF-based programs that address tactical, operational and strategic needs across an organization's People, Processes, Technologies, Data, Facilities and AI considerations.
SCR Assessor
Certified individuals qualified to participate in or lead a 3PAO assessment team performing SCR CAP assessments, and to analyze whether a control is appropriate, properly implemented and produces the intended result.
SCR Trainer
Certified individuals responsible for delivering initial and recurring SCF-based training for SAICO-approved certifications. The SCR Trainer role is expected to be available in 2027.
SCR Licensed Training Provider (SCR LTP)
LTPs are SAICO-certified organizations that deliver an approved individual-level certification training program using SCR Trainers. This role is coming later.
The SCF Council
The content is free and open, while the power to certify against it deliberately sits with separate organizations.
The SCF Council owns the authoritative content behind the program. It does not accredit assessors and it does not issue certifications, which is what keeps the content function separate from the assessment function.
SCR CAP Body of Knowledge
The authoritative source for what the SCR CAP is and how the assessment, attestation and certification activities are conducted. Start here before anything else.
SCR CAP Assessment Guides
Law, regulation and framework specific guidance for conducting SCF-related assessment activities, including the control scoping and assessment objectives for each certification.
LCP
SCF Licensed Content Providers: Entities authorized by the SCF Council to create derivative SCF content such as policies, standards and procedures, with quality control over how the SCF is operationalized in documentation.
How An Organization Moves Through The Ecosystem
Most organizations meet the ecosystem in four steps.
An organization typically meets the ecosystem in this order. It starts as an OSA, often engages an RPO to prepare and a CAT or ASP to operationalize the controls, then engages an accredited 3PAO whose SCR Assessors perform the assessment. A successful assessment makes it a Certified Organization.
Decide what you are certifying against: The SCR CAP Assessment Guides define the control scoping and assessment objectives for each available certification.
Prepare: An RPO can help you close gaps, and a CAT or ASP can give you somewhere to run the control set rather than a spreadsheet.
Get assessed: An accredited 3PAO conducts the assessment using SAICO-certified SCR Assessors and produces the Report on Conformity.
Maintain it: Certification is not a one-time event. It is held through ongoing compliance effort and periodic reassessment.