What Is the SCR CAP?
The SCR CAP exists to leverage SCF content to provide a company-level certification through a conformity assessment process. The Cyber AB is the Accreditation Body (AB) for the SCR CAP.
As a metaframework, the SCR CAP allows for a singular certification approach to cybersecurity and data protection requirements. The certification is designed to signify a real accomplishment, rather than be viewed as a “participation ribbon” with little practical value for the Organization Seeking Assessment (OSA) or its stakeholders.
The SCR CAP is designed for cybersecurity and privacy practitioners, by cybersecurity and data privacy practitioners. Key principles include: view compliance as a natural by-product of secure practices; scale to address multifaceted operational requirements simultaneously; acknowledge the stated risk tolerance of the OSA; minimize the risk of “gaming” the certification process; utilize technology to reduce labor-related assessment costs; and leverage existing, industry-recognized assessment practices.
Assessment Methodology: Examine, Interview & Test
The SCR CAP utilizes an examine, interview, and test assessment methodology to demonstrate conformity with multiple requirements simultaneously. This approach allows the SCR CAP to scale to cover multiple requirements in a single assessment. For example, it can demonstrate conformity with NIST CSF, HIPAA, and EU GDPR as part of one engagement rather than three separate assessments.
The SCR CAP also allows an organization to specify the statutory, regulatory, and contractual obligations that are applicable, establishing a Minimum Security Requirements (MSR) control set tailored to the organization’s specific obligations.
SCR CAP Body of Knowledge
Download the SCR CAP Body of Knowledge (PDF) for a comprehensive overview of the assessment methodology, accreditation requirements, and program structure.
SCF-Based Certifications Available
The following SCF-based certifications are available through the SCR CAP. See the SCR Assessment Guides for detailed assessment criteria and control scoping for each certification.
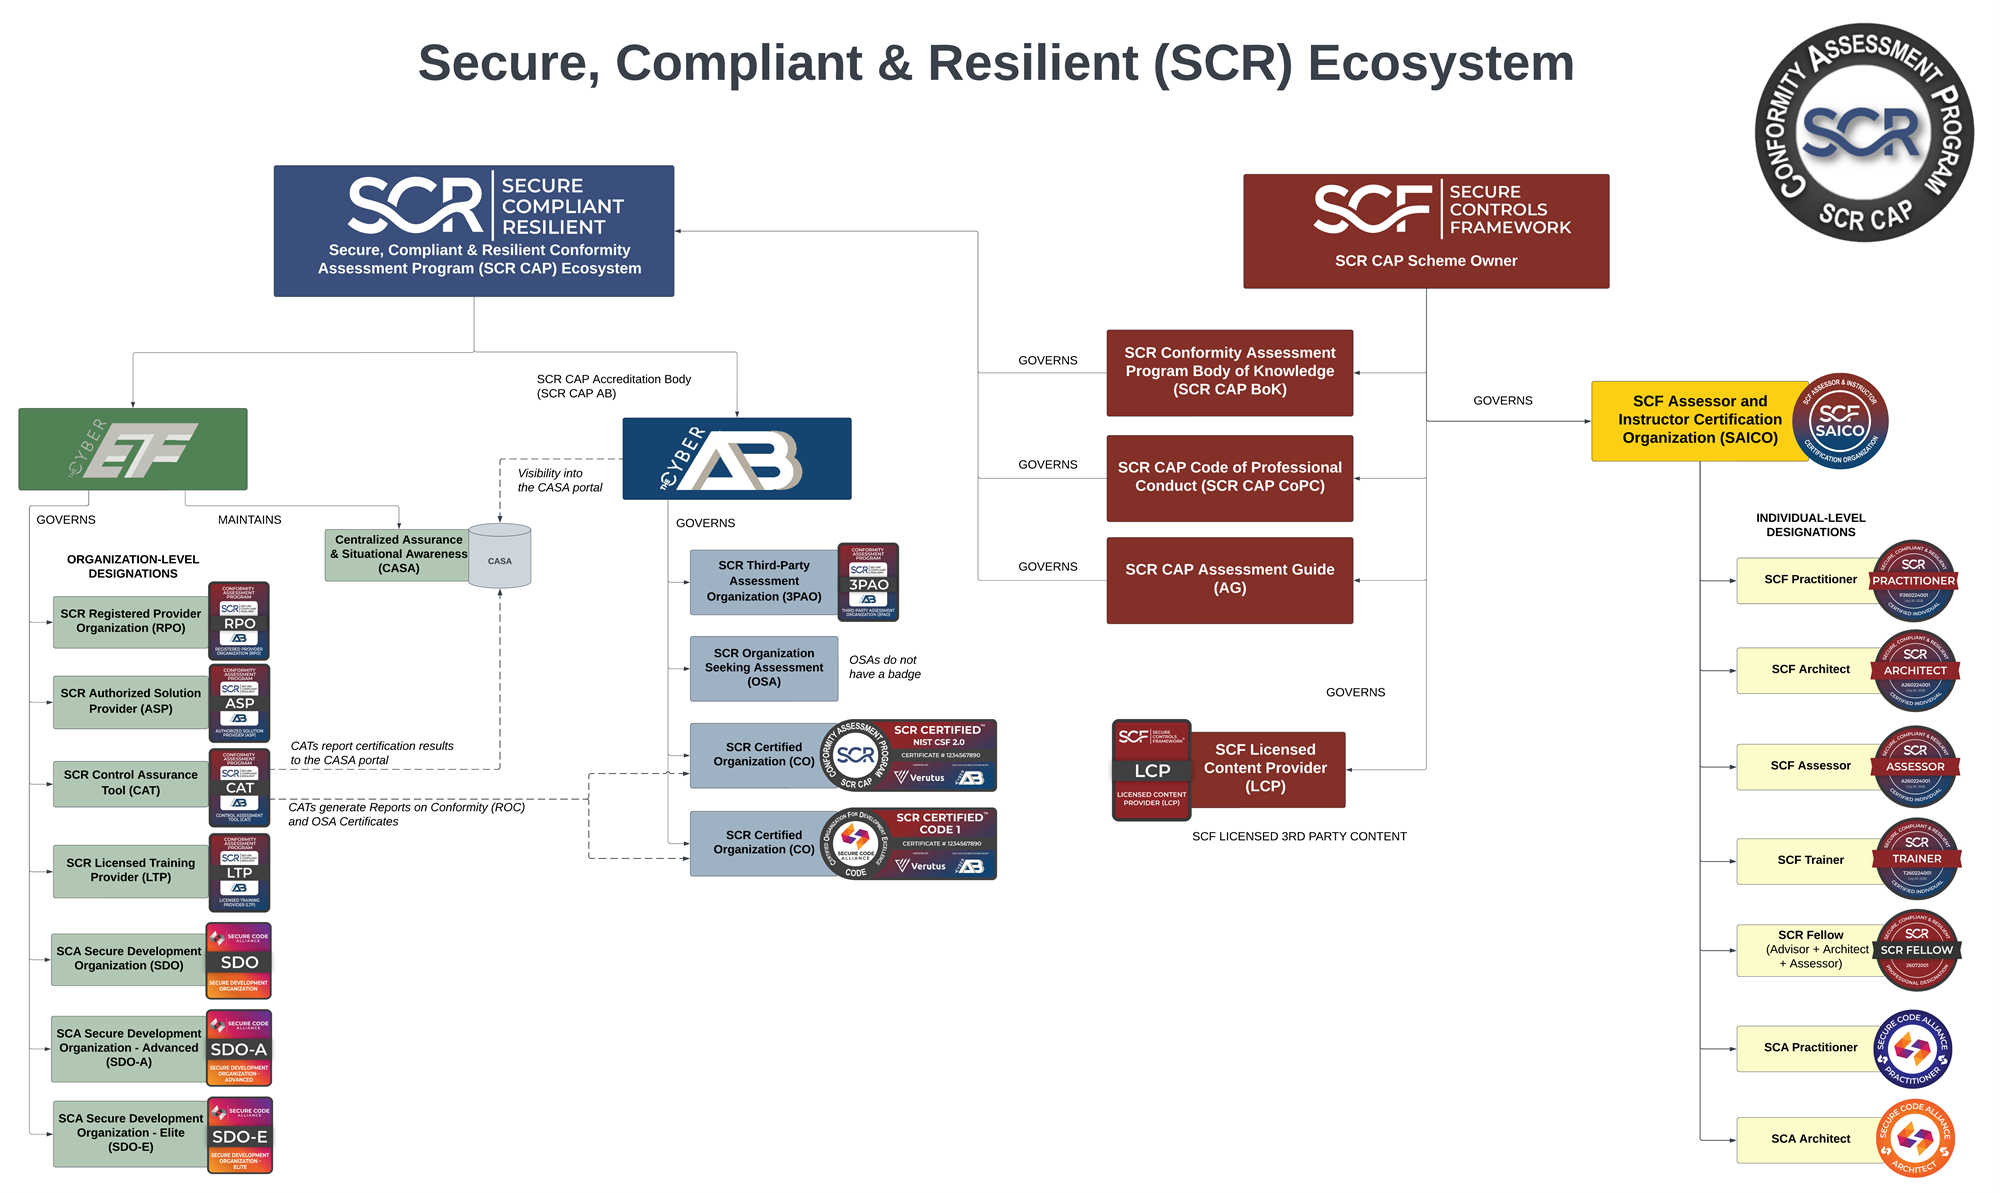
Key Players in the SCR CAP Ecosystem
There are several key players in the SCR CAP Ecosystem that are worth highlighting. Together, they form a complete, governed conformity assessment infrastructure. The ecosystem includes 3PAOs, ASPs, RPOs, OSAs, CATs, LTPs, and LCPs.
SCR Third-Party Assessment Organizations (3PAOs)
Independent organizations accredited to conduct SCR CAP conformity assessments. 3PAOs are accredited by The Cyber AB and must maintain qualified SCR Assessor personnel.
SCR Registered Provider Organizations (RPOs)
Consulting and advisory organizations registered to provide SCF implementation, advisory, and SCR CAP preparation services to Organizations Seeking Assessment.
SCF Licensed Content Providers (LCPs)
Organizations licensed to incorporate SCF content into their commercial products, tools, and platforms under the SCF licensing program.