Secure Controls Framework
Download The SCF

Set Theory Relationship Mapping (STRM)

Starting with release 2024.1, the SCF leverages NIST IR 8477 Set Theory Relationship Mapping for crosswalk mapping. This is the US Government's gold standard for evaluating cybersecurity and data privacy laws, regulations and frameworks.

Need Excel Versions Of STRM?

While the PDF versions of the STRM are free (scroll down the page to see them), the SCF offers editable Excel versions of all STRM mappings. The bundle of Excel versions is $25 (access to redownload is available for 30 days from date of purchase).

Secure Controls Framework - purchase Set Theory Relationship Mapping (STRM)
NIST IR 8477

The Gold Standard for Crosswalk Mapping

NIST IR 8477 provides the definitive practice for crosswalk mapping with no technology needed. It can be performed with a pencil and piece of paper.

Children learn the process of diagramming sentences in grade school (e.g., the Reed–Kellogg model) with pencil and paper. This same process of graphically identifying the relationships between elements forms the basis of STRM. What NIST IR 8477 does is formalize this with Set Theory mathematics to produce rigorous, defensible, and IP-protected crosswalk mappings.

STRM is part of NIST’s broader NIST OLIR Program, an effort to facilitate Subject Matter Experts in defining standardized Online Informative References between elements of their creation and NIST publications. The SCF has been participating in the NIST OLIR program for several years now to help make crosswalk mapping easier and more accessible.

You can click on the image to the side to see a PDF version of how the SCF is utilizing STRM, as well as an example for what that looks like with a few NIST CSF 2.0 controls:
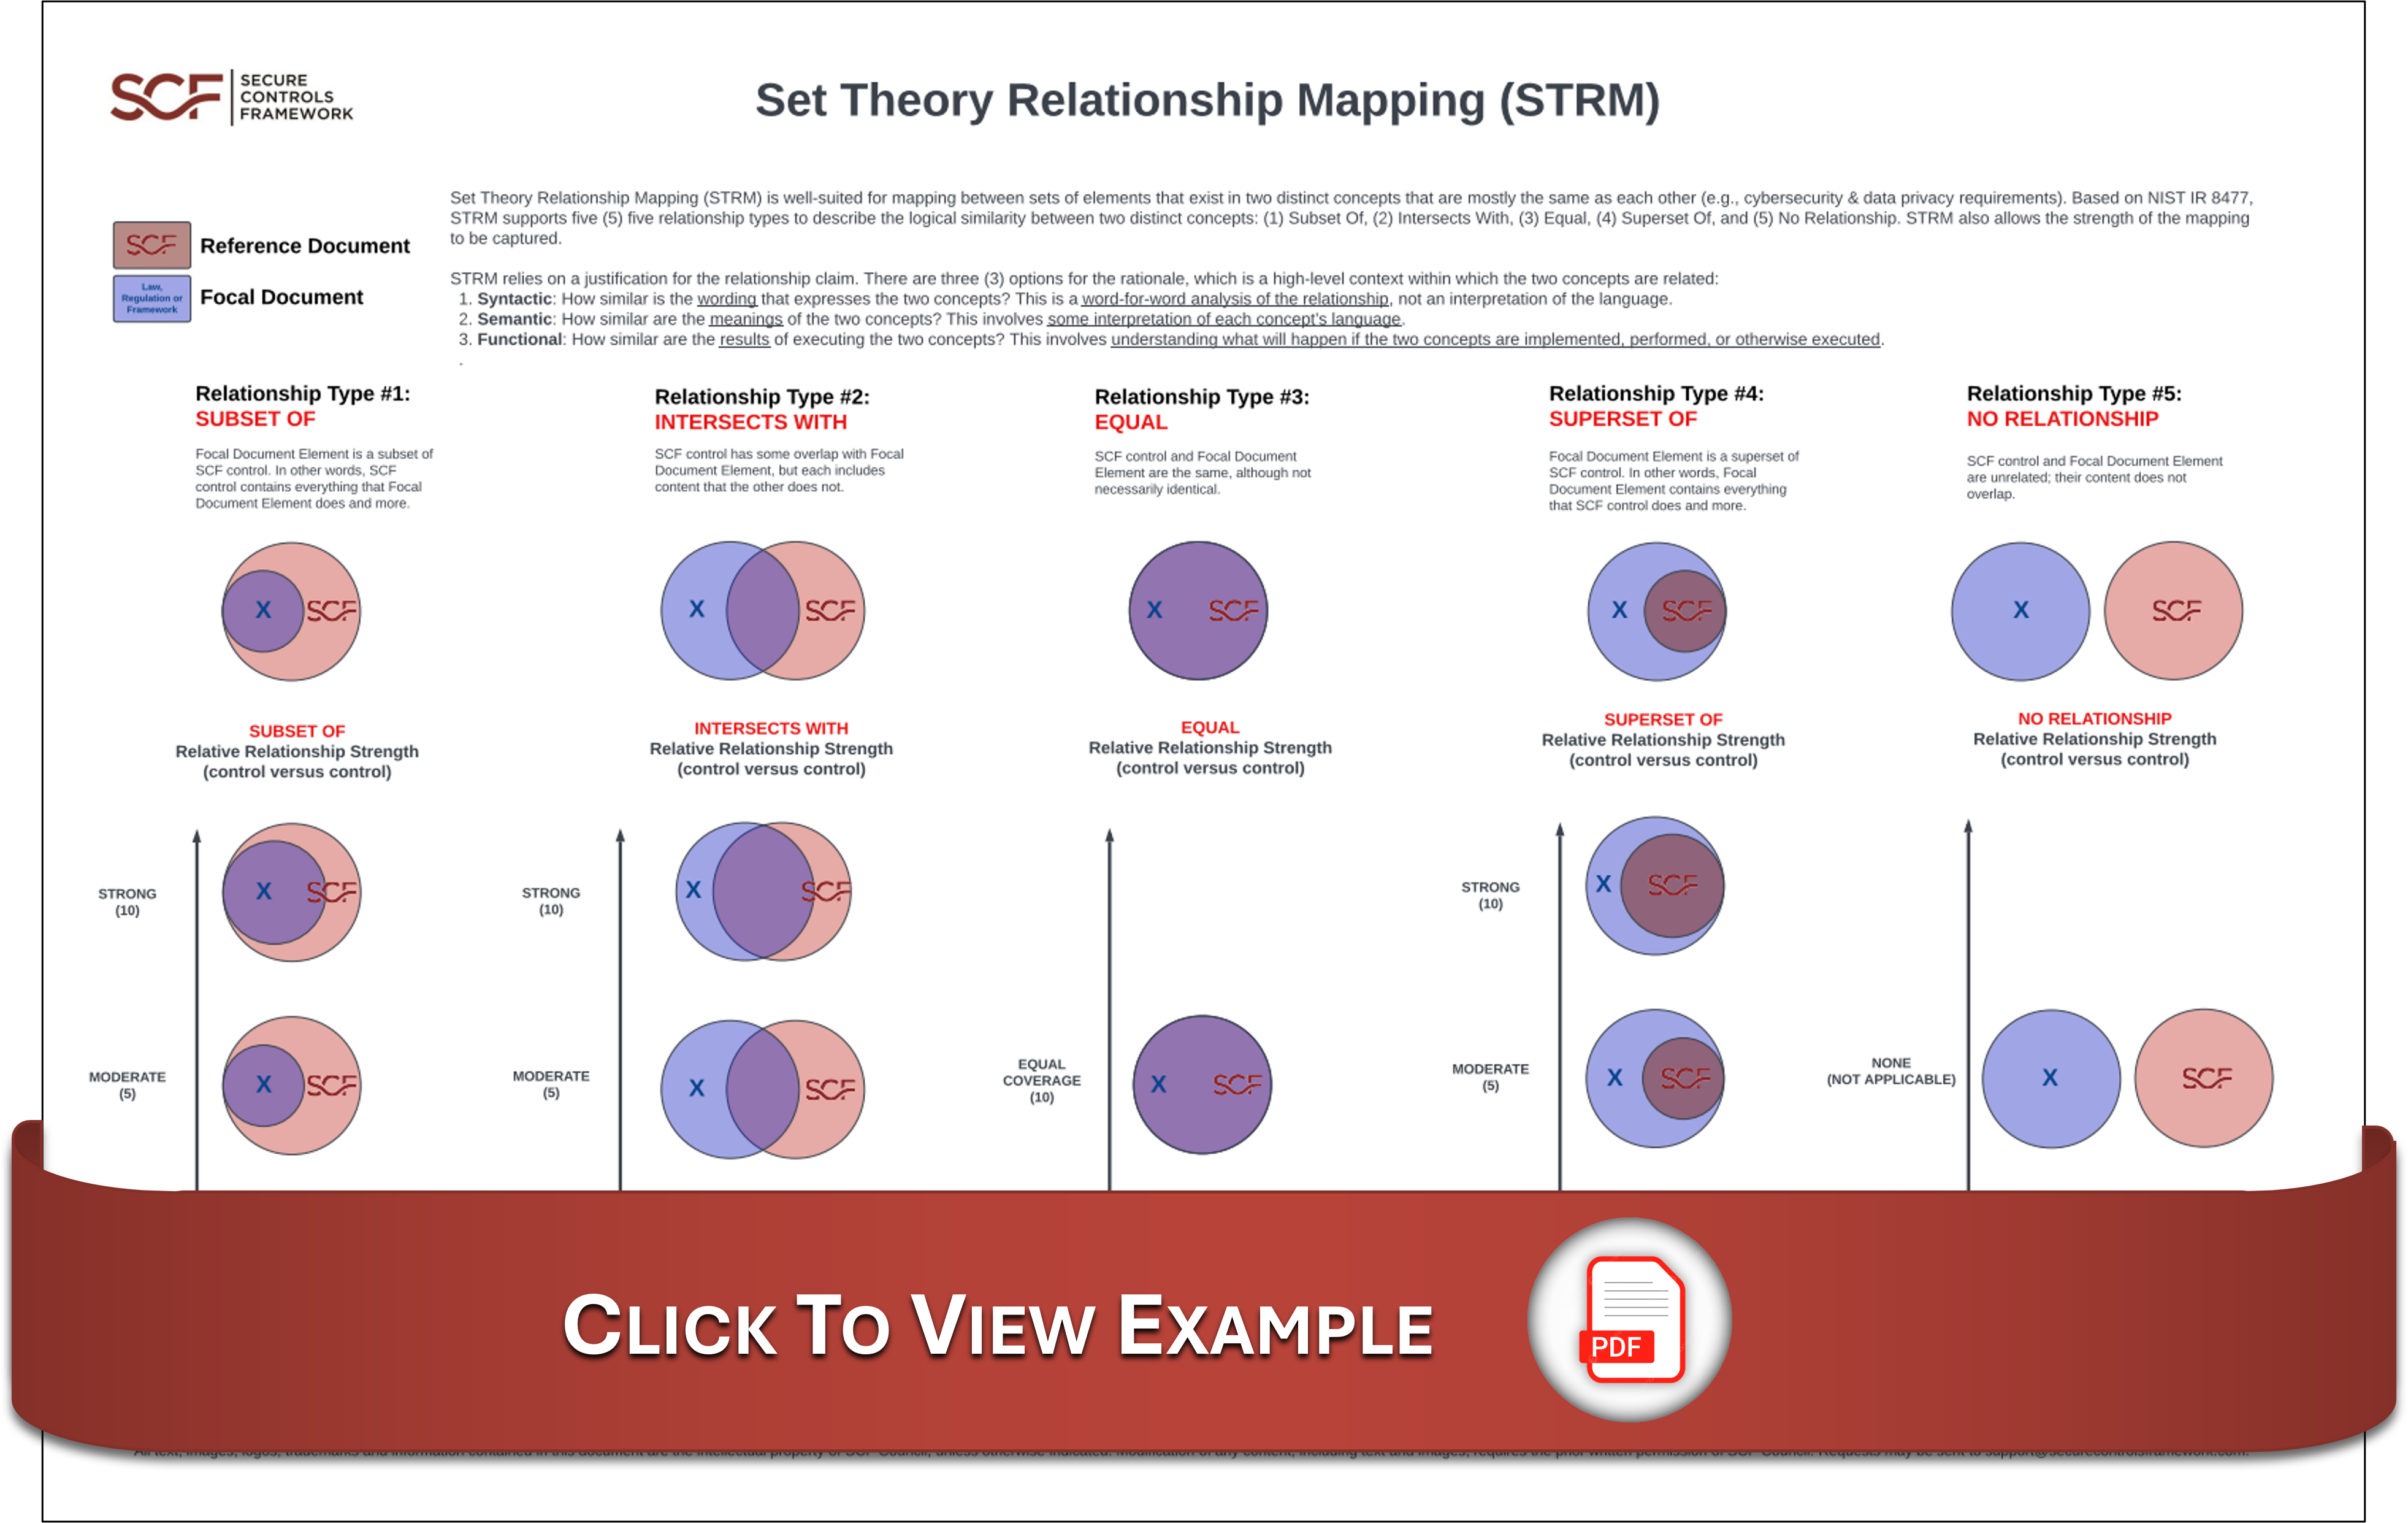
NIST IR 8477 Set Theory Relationship Mapping (STRM) example PDF showing how the SCF maps controls using set theory Venn diagrams with NIST CSF 2.0 crosswalk examples
STRM Methodology

The 5 STRM Relationship Types

Every crosswalk mapping in the SCF uses exactly one of these five mathematically-defined relationship types, ensuring precision and consistency across all 200+ mapped LRF.

STRM Relationship Types
⊂
Subset Of
The LRF requirement is fully contained within the SCF control. The SCF control is broader in scope and coverage.
=
Equal To
The LRF requirement and SCF control are semantically equivalent. They address the same concept at the same scope.
⊃
Superset Of
The SCF control is contained within the LRF requirement. The LRF requirement is broader in scope and coverage.
∩
Intersects With
The LRF requirement and SCF control share partial overlap. Neither is fully contained within the other.
∅
No Relationship
The LRF requirement and SCF control have no meaningful semantic overlap. No mapping is established.

Relationship Strength (1–10)

Relationship Strength (1–10): Each mapping also receives a numeric strength rating. A rating of 1 indicates a nominal relationship, 5 indicates moderately strong, and 10 indicates the strongest relationship, typically reserved for "Equal To" or where the LRF requirement is a "Subset Of" the SCF control.

Methodology Advantage

Expert-Derived Content (EDC) vs. Natural Language Processing (NLP)

The SCF exclusively uses human subject-matter experts to perform STRM crosswalk mapping. This is a deliberate choice with significant IP, legal and quality implications.

SCF: Expert-Derived Content (EDC)

The SCF leverages human SMEs to perform STRM mapping. This produces content that is:

  • Copyright-protected as original work by human creators
  • Patent-eligible under the “mental steps” doctrine
  • Defensible through documented expert judgment
  • Consistent with NIST IR 8477 gold standard practices

Other Vendors: Natural Language Processing (NLP)

AI/NLP-based crosswalk solutions face significant IP limitations:

  • AI-generated content is not copyright-protectable (no human creator)
  • Potentially free to copy under current US copyright rulings
  • Patent claims may be invalid under the 2014 Supreme Court “mental steps” doctrine
  • Quality depends on training data rather than professional expertise

Why it matters

The SCF's EDC approach means its crosswalk mappings are both higher-quality and legally protected intellectual property, which is exactly how NIST IR 8477 itself was designed to work.

SCF Implementation

How the SCF Utilizes STRM

The SCF applies STRM to every one of its 200+ mapped laws, regulations and frameworks. Each mapping documents the precise set-theoretic relationship between every LRF requirement and the corresponding SCF control.

Focal Document Element (FDE)

Each LRF requirement is defined as a Focal Document Element with a unique identifier. Without a unique FDE value, no granular mapping is possible because there is nothing to map to.

SCF Control Mapping

Each FDE is mapped to the most appropriate SCF control with a documented relationship type (Subset Of, Intersects With, Equal To, Superset Of, or No Relationship) and a strength score of 1–10.

Multi-Framework Compliance

Because all LRF are mapped to common SCF controls using STRM, a single SCF control can simultaneously satisfy requirements across dozens of laws, regulations and frameworks. This enables true multi-framework compliance efficiency.

Available STRMs

Published STRM Mappings

Excel versions of the STRM mappings are available for purchase at the SCF Store. The following STRM mappings are currently published:

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
AICPA
General
✓ STRM
American Institute of Certified Public Accountants (AICPA) Privacy Management Framework (PMF) (2020)
AICPA
General
✓ STRM
American Institute of Certified Public Accountants (AICPA) Trust Services Criteria (2017)
Argentina
Americas
✓ STRM
Argentina - Protection of Personal Data (2018)
APEC
General
✓ STRM
Asia - Pacific Economic Cooperation (APEC) Privacy Framework (2015)
Australia
APAC
✓ STRM
Australia - Cloud Controls Matrix (June 2026)
Australia
APAC
✓ STRM
Australia - Code of Practice - Securing the Internet of Things for Consumers (2020)
Australia
APAC
✓ STRM
Australia - Essential Eight maturity model and ISM mapping (2024)
Australia
APAC
✓ STRM
Australia - Information Security Manual (ISM) (June 2026)
Australia
APAC
✓ STRM
Australia - Privacy Principles (2026)
Australia
APAC
✓ STRM
Australia - Prudential Standard CPS 230 - Operational Risk Management (2023)
Australia
APAC
✓ STRM
Australia - Prudential Standard CPS 234 Information Security (2019)
Australia
APAC
✓ STRM
Australia - Security of Critical Infrastructure Act 2018 (Compilation No. 9, 4 June 2026)
Austria
EMEA
✓ STRM
Austria - Data Protection Act (2018)
Bahamas
Americas
✓ STRM
Bahamas - Data Protection Act (DPA) (2003)
Belgium
EMEA
✓ STRM
Belgium - Act of 30 July 2018
Bermuda
Americas
✓ STRM
Bermuda - Bermuda Monetary Authority (BMA) Insurance Sector Operational Cyber Risk Management Code of Conduct (2020)
Brazil
Americas
✓ STRM
Brazil - General Data Protection Law (LGPD) (2018)
BSI
General
✓ STRM
Bundesamt für Sicherheit in der Informationstechnik (BSI) - Standard 200-1 (v1.0)
Canada
Americas
✓ STRM
Canada - OSFI B-13 (2022)
Canada
Americas
✓ STRM
Canada - OSFI Cyber Security Self-Assessment Guidance
Canada
Americas
✓ STRM
Canada - Personal Information Protection and Electronic Documents Act (PIPEDA) (2000)
Canada
Americas
✓ STRM
Canada - Protecting controlled information in non-Government of Canada systems and organizations (ITSP.10.171) (2025)
CIS
General
✓ STRM
Center for Internet Security (CIS) Critical Security Controls (CSC) version 8.1
CIS
General
✓ STRM
Center for Internet Security (CIS) Critical Security Controls (CSC) version 8.1-IG1

No matching frameworks found. Try a different search term or filter.

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
AICPA
General
✓ STRM
American Institute of Certified Public Accountants (AICPA) Privacy Management Framework (PMF) (2020)
AICPA
General
✓ STRM
American Institute of Certified Public Accountants (AICPA) Trust Services Criteria (2017)
APEC
General
✓ STRM
Asia - Pacific Economic Cooperation (APEC) Privacy Framework (2015)
BSI
General
✓ STRM
Bundesamt für Sicherheit in der Informationstechnik (BSI) - Standard 200-1 (v1.0)
CIS
General
✓ STRM
Center for Internet Security (CIS) Critical Security Controls (CSC) version 8.1
CIS
General
✓ STRM
Center for Internet Security (CIS) Critical Security Controls (CSC) version 8.1-IG1
CIS
General
✓ STRM
Center for Internet Security (CIS) Critical Security Controls (CSC) version 8.1-IG2
CIS
General
✓ STRM
Center for Internet Security (CIS) Critical Security Controls (CSC) version 8.1-IG3
CSA
General
✓ STRM
Cloud Security Alliance (CSA) Cloud Controls Matrix (CCM) v4.1.0
CSA
General
✓ STRM
Cloud Security Alliance (CSA) Internet of Things Security Controls Framework v2
COSO
General
✓ STRM
Committee of Sponsoring Organizations (COSO) (2013)
ISACA
General
✓ STRM
Control Objectives for Information and Related Technologies (COBIT) (2019)
CR
General
✓ STRM
Cyber Resilience Capability Maturity Model (CR-CMM) (2026)
GovRAMP
General
✓ STRM
Government Risk and Authorization Management Program (GovRAMP)
GovRAMP
General
✓ STRM
Government Risk and Authorization Management Program (GovRAMP) - Core Controls
GovRAMP
General
✓ STRM
Government Risk and Authorization Management Program (GovRAMP) - High
GovRAMP
General
✓ STRM
Government Risk and Authorization Management Program (GovRAMP) - Low
GovRAMP
General
✓ STRM
Government Risk and Authorization Management Program (GovRAMP) - Low+
GovRAMP
General
✓ STRM
Government Risk and Authorization Management Program (GovRAMP) - Moderate
IEC
General
✓ STRM
International Electrotechnical Commission 62443-4-2 Ed. 1.0 b:2019 - Security for industrial automation and control systems - Part 4-2: Technical security requirements for IACS components
IEC
General
✓ STRM
International Electrotechnical Commission (IEC) 62443-2-1:2024 - Security for industrial automation and control systems - Part 2-1: Security program requirements for IACS asset owners
IEC
General
✓ STRM
International Electrotechnical Commission (IEC) 62443-3-3:2013 - Industrial communication networks - Network and system security - Part 3-3: System security requirements and security levels
IEC
General
✓ STRM
International Electrotechnical Commission (IEC) 62443-4-1:2018 - Security for industrial automation and control systems - Part 4-1: Secure product development lifecycle requirements
IEC
General
✓ STRM
International Electrotechnical Commission (IEC) Technical Report 60601-4-5:2021 - Medical electrical equipment - Part 4-5: Guidance and interpretation - Safety-related technical security specifications

No matching frameworks found. Try a different search term or filter.

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Federal
USA
✓ STRM
USA - 33 CFR Part 101 Subpart F (up to date as of 4-17-2026)
State
USA
✓ STRM
USA - Alaska Personal Information Protection Act (PIPA) (2009)
State
USA
✓ STRM
USA - California Consumer Privacy Act (CCPA) (January 2026) - amended California Privacy Rights Act (CPRA)
State
USA
✓ STRM
USA - California SB1386 (2002)
State
USA
✓ STRM
USA - California SB327 (2018)
Federal
USA
✓ STRM
USA - Centers for Medicare & Medicaid Services MARS-E Document Suite, Version 2.0
Federal
USA
✓ STRM
USA - Children's Online Privacy Protection Act (COPPA) (2024)
State
USA
✓ STRM
USA - Colorado Privacy Act (2021)
Federal
USA
✓ STRM
USA - Cybersecurity & Infrastructure Security Agency (CISA) Cross-Sector Cybersecurity Performance Goals 2.0
Federal
USA
✓ STRM
USA - Cybersecurity & Infrastructure Security Agency (CISA) Secure Software Development Attestation Form (SSDAF) (2024)
Federal
USA
✓ STRM
USA - Cybersecurity & Infrastructure Security Agency (CISA) Trusted Internet Connections 3.0 Security Capabilities Catalog
Federal
USA
✓ STRM
USA - Data Privacy Framework (2023)
Federal
USA
✓ STRM
USA - Defense Federal Acquisition Regulation Supplement (DFARS) 252.204-7012
Federal
USA
✓ STRM
USA - Department of Energy (DOE) - Cybersecurity Capability Maturity Model version 2.1
Federal
USA
✓ STRM
USA - Department of Justice - Criminal Justice Information Services (CJIS) Security Policy v6.0
Federal
USA
✓ STRM
USA - Department of War (DoW) - Computer Emergency Response Team (CERT) Resilience Management Model (RMM) Version 1.2
Federal
USA
✓ STRM
USA - Department of War (DoW) - Cybersecurity Maturity Model Certification (CMMC) v2.0 - Level 1
Federal
USA
✓ STRM
USA - Department of War (DoW) - Cybersecurity Maturity Model Certification (CMMC) v2.0 - Level 1 Assessment Objectives
Federal
USA
✓ STRM
USA - Department of War (DoW) - Cybersecurity Maturity Model Certification (CMMC) v2.0 - Level 2
Federal
USA
✓ STRM
USA - Department of War (DoW) - Cybersecurity Maturity Model Certification (CMMC) v2.0 - Level 3
Federal
USA
✓ STRM
USA - Department of War (DoW) - Zero Trust Execution Roadmap v1.1
Federal
USA
✓ STRM
USA - Department of War (DoW) - Zero Trust Reference Architecture v2
USA - Federal
USA
✓ STRM
USA - DoW Brilliant at the Basics: Top 10 IT Cybersecurity Best Practices for DIB Partners
USA - Federal
USA
✓ STRM
USA - DoW Brilliant at the Basics: Top 10 OT Cybersecurity Best Practices for DIB Partners

No matching frameworks found. Try a different search term or filter.

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Kenya
EMEA
✓ STRM
Kenya - Data Protection Act (DPA) (2019)
Nigeria
EMEA
✓ STRM
Nigeria - Data Protection Regulation (DPR) (2019)
Norway
EMEA
✓ STRM
Norway - Personal Data Act (PDA) (2018)
Poland
EMEA
✓ STRM
Poland - Act of 10 May 2018 on the Protection of Personal Data
Qatar
EMEA
✓ STRM
Qatar - Personal Data Privacy Protection Law (PDPPL) (2020)
Russia
EMEA
✓ STRM
Russia - Federal Law No. 152-FZ (2025)
Saudi Arabia
EMEA
✓ STRM
Saudi Arabia - Critical Systems Cybersecurity Controls (CSCC – 1: 2019)
Saudi Arabia
EMEA
✓ STRM
Saudi Arabia - Cybersecurity Guidelines for Internet of Things (CGIoT - 1:2024)
Saudi Arabia
EMEA
✓ STRM
Saudi Arabia - Essential Cybersecurity Controls (ECC – 1 : 2018)
Saudi Arabia
EMEA
✓ STRM
Saudi Arabia - Operational Technology Cybersecurity Controls (OTCC-1: 2022)
Saudi Arabia
EMEA
✓ STRM
Saudi Arabia - Personal Data Protection Law (PDPL) (2023)
Saudi Arabia
EMEA
✓ STRM
Saudi Arabia - SACS-002 Third Party Cybersecurity Standard (2022)
Saudi Arabia
EMEA
✓ STRM
Saudi Arabia - Saudi Arabian Monetary Authority (SAMA) Cyber Security Framework Version 1.0 (2017)
Serbia
EMEA
✓ STRM
Serbia - Act of 9 November 2018 on Personal Data Protection (Official Gazette No. 87/18)
South Africa
EMEA
✓ STRM
South Africa - Protection of Personal Information Act (POPIA) (2013)
Spain
EMEA
✓ STRM
Spain - ICT Security Guide CCN-STIC 825 (2026)
Spain
EMEA
✓ STRM
Spain - Royal Decree 311/2022
Switzerland
EMEA
✓ STRM
Switzerland - Federal Act on Data Protection (FADP) (2025)
Turkey
EMEA
✓ STRM
Turkey - Law on the Protection of Personal Data (LPPD) (2016)
UAE
EMEA
✓ STRM
UAE - National Information Assurance Framework (NIAF) (2023)
United Kingdom
EMEA
✓ STRM
UK - Cyber Assessment Framework (CAF) v4.0
United Kingdom
EMEA
✓ STRM
UK - Cyber Assessment Framework for Aviation Guidance (CAP1850) (2020)
United Kingdom
EMEA
✓ STRM
UK - Cyber Essentials: Requirements for IT Infrastructure v3.3
United Kingdom
EMEA
✓ STRM
UK - Data Protection Act (DPA) (2018)

No matching frameworks found. Try a different search term or filter.

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
New Zealand
APAC
✓ STRM
New Zealand - Privacy Act (2020)
Philippines
APAC
✓ STRM
Philippines - Data Privacy Act (DPA) (2012)
India
APAC
✓ STRM
Reserve Bank of India (RBI) - Master Direction on Digital Payment Security Controls, 2021
India
APAC
✓ STRM
Reserve Bank of India (RBI) - Master Direction on Prepaid Payment Instruments (PPI), 2021
India
APAC
✓ STRM
Reserve Bank of India (RBI) - Master Direction on Regulation of Payment Aggregators (PA) (2025)
India
APAC
✓ STRM
Reserve Bank of India (RBI) - Storage of Payment System Data - Data Localization, 2018
Singapore
APAC
✓ STRM
Singapore - Cyber Hygiene Practice (2019)
Singapore
APAC
✓ STRM
Singapore - Cybersecurity Code of Practice for Critical Information Infrastructure (CCP CII) (2026)
Singapore
APAC
✓ STRM
Singapore - Monitory Authority of Singapore (MAS) Technology Risk Management (TRM) Guidelines (2021)
Singapore
APAC
✓ STRM
Singapore - Personal Data Protection Ac (PDPA) (2012)
South Korea
APAC
✓ STRM
South Korea - Personal Information Protection Act (PIPA) (2011)
Taiwan
APAC
✓ STRM
Taiwan - Personal Data Protection Act (PDPA) (2025)

No matching frameworks found. Try a different search term or filter.

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Argentina
Americas
✓ STRM
Argentina - Protection of Personal Data (2018)
Bahamas
Americas
✓ STRM
Bahamas - Data Protection Act (DPA) (2003)
Bermuda
Americas
✓ STRM
Bermuda - Bermuda Monetary Authority (BMA) Insurance Sector Operational Cyber Risk Management Code of Conduct (2020)
Brazil
Americas
✓ STRM
Brazil - General Data Protection Law (LGPD) (2018)
Canada
Americas
✓ STRM
Canada - OSFI B-13 (2022)
Canada
Americas
✓ STRM
Canada - OSFI Cyber Security Self-Assessment Guidance
Canada
Americas
✓ STRM
Canada - Personal Information Protection and Electronic Documents Act (PIPEDA) (2000)
Canada
Americas
✓ STRM
Canada - Protecting controlled information in non-Government of Canada systems and organizations (ITSP.10.171) (2025)
Chile
Americas
✓ STRM
Chile - Act 19628 - Protection of Personal Data (1999)
Colombia
Americas
✓ STRM
Colombia - Law 1581 (2012)
Mexico
Americas
✓ STRM
Mexico - Federal Law on Protection of Personal Data held by Private Parties (2010)

No matching frameworks found. Try a different search term or filter.

Community Involvement

How To Submit a Community STRM Mapping

The SCF welcomes community involvement. The SCF Council provides a downloadable Community STRM Template that practitioners can use to perform their own crosswalk mapping and submit for possible inclusion in a future SCF release.

01

Define the Focal Document

Open the STRM template’s “STRM Overview” tab and complete the two highlighted cells identifying:

  • The Focal Document (FD), which is the law, regulation or framework you are mapping
  • The Reference Document (RD), which is the SCF (the document being mapped to)

Prerequisites: familiarity with NIST IR 8477 and professional competence to conduct crosswalk mapping.

02

Perform the STRM Mapping

Complete the “Community STRM submission” tab using these columns:

  • FDE number (mandatory unique identifier)
  • FDE name (if available)
  • FDE description (exact text of the requirement)
  • Proposed SCF control name
  • SCF control number
  • SCF control description
  • STRM relationship type (1 of 5 options)
  • Relationship strength (1–10 rating)
  • Optional notes / justification
03

Submit to the SCF Council

Once your STRM exercise is complete, email the completed Excel spreadsheet to the SCF Council for review:

support@securecontrolsframework.com

Submissions are evaluated by the SCF Council and may be included in a future SCF release. The SCF Council will contact you if there are questions about your submission.