
Organization-Level and Individual-Level Certifications
The SCR certification ecosystem serves two distinct audiences: organizations seeking a defensible, third-party-validated security conformity designation, and individual cybersecurity professionals seeking credentials that demonstrate mastery of the SCF and its implementation methodology.
Company-Level SCR Certifications
It is possible to become certified using SCF controls. For example, SCR Certified for NIST CSF 2.0, SCR Certified for HIPAA Security Rule and more. This is all part of the SCR Conformity Assessment Program (SCR CAP). The SCR CAP leverages the SCF's metaframework structure and no-cost content to make conformity assessments more cost-effective, efficient, and objective.
Available certifications include: NIST SP 800-171 R3, NIST Cybersecurity Framework 2.0 (NIST CSF 2.0), NY DFS 23 NYCRR Part 500, HIPAA Security Rule (NIST SP 800-66 R2), NIST SP 800-161 R1, SCF CORE Fundamentals and CMMC Level 1.
Individual-Level SCR Certifications
The SCR Assessor and Instructor Certification Organization (SAICO) is a separate entity responsible for individual-level certification and training within the SCR CAP Ecosystem. SAICO provides three certification programs that equip cybersecurity professionals with the expertise to evaluate and implement SCF controls effectively. Each course uses Computer-Based Training (CBT), enabling self-paced learning.
Three Certification Tracks:
- SCR Practitioner, which covers foundation-level understanding of the SCF
- SCR Architect, which covers designing and implementing SCF-based programs
- SCR Assessor, which covers conducting conformity assessments using SCF methodology.
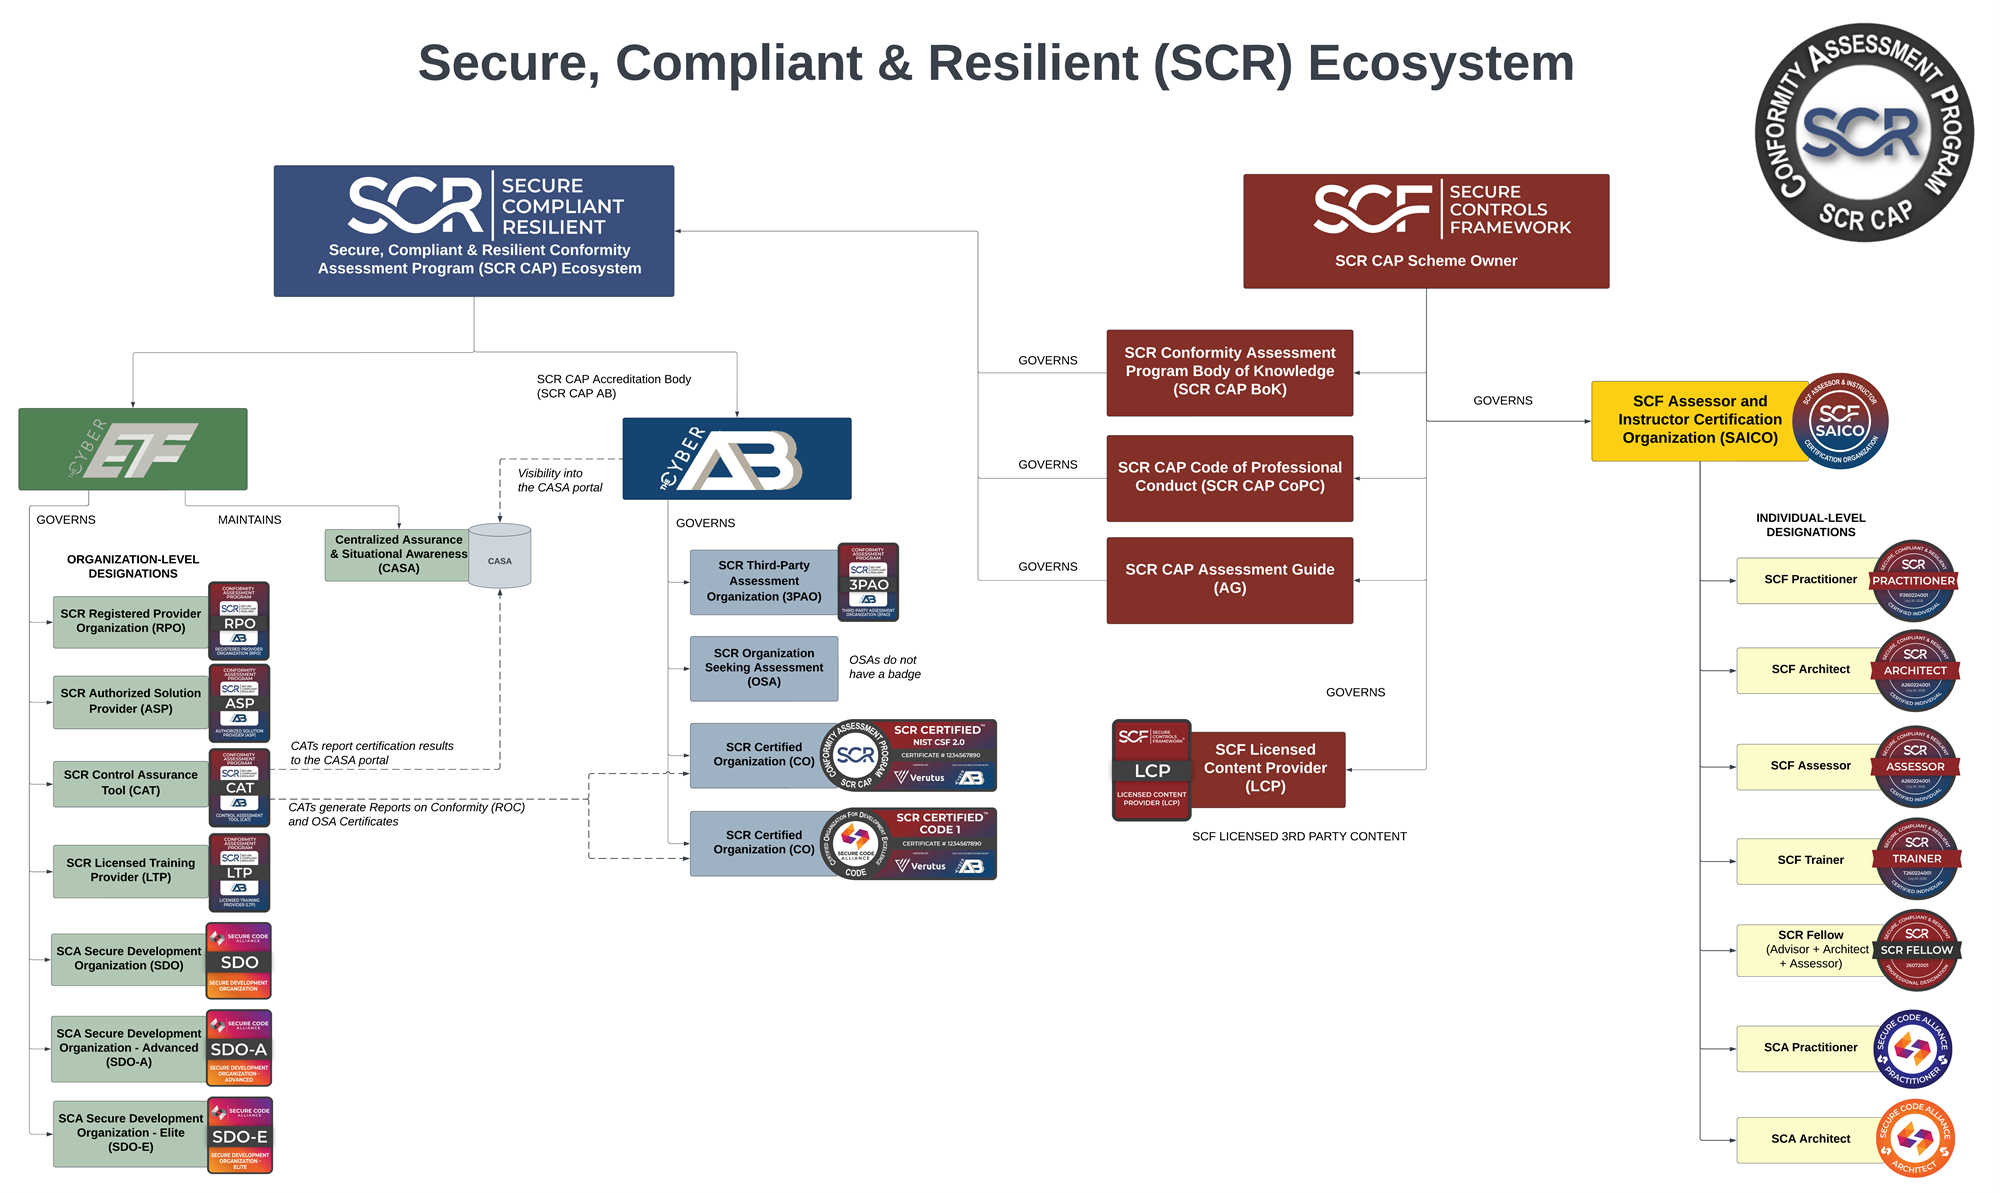
Seven Key Players in the SCR CAP Ecosystem
The SCR CAP Ecosystem consists of seven distinct roles that together enable a complete, auditable conformity assessment process, from initial assessment through ongoing oversight. Each role has defined responsibilities, qualifications, and relationships to other participants.
The SCR Ecosystem page is the full reference for who governs what, including The Cyber AB, the Cyber EF, SAICO and the SCF Council.
3PAO
SCR Third-Party Assessment Organizations
Independent assessment organizations accredited to conduct SCR CAP conformity assessments on behalf of organizations seeking certification.
OSA
SCR Organizations Seeking Assessment
The organization pursuing an SCF-based certification, whose security posture and controls implementation is being evaluated but which has not yet completed an SCR CAP conformity assessment.
ASP
SCR Authorized Solutions Providers
Cloud-based platforms and service providers, including CSPs, MSPs and MSSPs, that operate within the defined scope of the SCF and give organizations a structured environment for implementing it.
RPO
SCR Registered Provider Organizations
Consulting and advisory organizations registered to provide SCF implementation, advisory, and assessment preparation services.
CAT
SCR Control Assurance Tools
Governance, Risk and Compliance platforms that specialize in integrating the SCF, so that compliance interpretation and risk management are operationalized inside the tools an organization already runs.
LTP
SCR Licensed Training Providers
Organizations certified by SAICO to deliver approved individual-level certification training programs using SCR Trainers.
LCP
SCF Licensed Content Providers
Organizations authorized by the SCF Council to create derivative SCF content, such as SCF-based policies, standards and procedures.
CAP
SCR Conformity Assessment Program
The program framework that governs all ecosystem participant roles, assessment standards, and certification requirements. Accreditation Body: The Cyber AB.
Three Professional Certification Tracks
The SCR Assessor and Instructor Certification Organization (SAICO) provides three Computer-Based Training (CBT) certification programs. Each follows a defined syllabus to meet the specific learning objectives and standards of the certification track.
SCR Practitioner
Foundation Level: The entry-point certification for cybersecurity professionals who work with the SCF. Covers the structure and application of the SCF, its control domains, and how to use the framework as a practitioner implementing or managing a security program. Self-paced CBT with defined syllabus, SAICO-certified.
SCR Architect
Design & Implementation: For cybersecurity professionals who design and implement security programs using the SCF. Covers program architecture, control selection and rationalization, SCF implementation, and the SCRMS operational model. Self-paced CBT with defined syllabus, SAICO-certified.
SCR Assessor
Assessment & Audit: The advanced certification for professionals who conduct conformity assessments using the SCF methodology. Covers assessment planning, examine-interview-test methodology, evidence evaluation, and SCR CAP assessment procedures. Self-paced CBT with defined syllabus, SAICO-certified.
