
Foreword
Entities invest in security, compliance and resilience as a necessity, driven in large part by statutory, regulatory and/or contractual requirements. To build and maintain efficient and effective operations, a security, compliance and resilience program must have a hierarchical vision, mission and strategy that directly supports broader strategic objectives and business processes.
A Secure, Compliant & Resilient Management System (SCRMS) is a framework and technology-agnostic approach to design, implement and maintain secure, compliant and resilient capabilities to cover an entity’s People, Processes, Technology, Data, Facilities & Artificial Intelligence (PPTDF-AI), regardless of how or where data is stored, processed and/or transmitted.
Built To Withstand Scrutiny
The underlying expectation is for those charged with developing, implementing and governing security, compliance and resilience capabilities to do so in a reasonable manner that would withstand scrutiny that could take the form as an external auditor, regulator or prosecuting attorney.
About The SCRMS
1.2 Framework-Agnostic Approach
By design, the SCRMS expands upon and modernizes the concept of traditional Information Security Management System (ISMS) models, due to the archaic nature of multiple, siloed “management systems” that are necessary to provide reasonable governance practices (e.g., Artificial Intelligence Management System (AIMS) add-on). The use of siloed ISMS, AIMS and similar stand-alone management systems fails to address the reality of modern business practices, since it is overly leveraged for marketing purposes. This does not serve assurance needs to demonstrate security, compliance or resilience that entities require. The SCRMS offers a broader “security, compliance and resilience ecosystem” mindset that is designed to provide the necessary coverage to address applicable risks and threats that entities face.
The SCRMS enables an entity to align with one, or more, laws, regulations and/or frameworks. For example, an entity that aligns with NIST CSF 2.0, but also has obligations for PCI DSS, ISO 27001, ISO 42001, HIPAA Security Rule and SOC 2 can leverage a “living control set” that is capable of adjusting to the specific security, compliance and resilience requirements it must address.
1.3 Target Audience
The SCRMS is written for senior cybersecurity practitioners and executives, specifically those in the following roles:
- Chief Information Security Officer (CISO); and
- Governance, Risk & Compliance (GRC) Director.
While any cybersecurity practitioner can benefit from the information provided in the SCRMS, those roles listed above are the primary decision-makers within an entity that enable a focus on secure, compliant and resilient practices. Their utilization of the SCRMS will trickle down to all other parts of the entity’s security, compliance and resilience program.
1.4 Intent
The SCRMS is not a “one-size-fits-all” playbook, since the information in this document is meant to be adopted and tailored to the unique size, resources and risk circumstances of the entity. The SCRMS is:
- Framework-agnostic, allowing entities to leverage one or more frameworks that it needs to align with (e.g., NIST CSF 2.0, SOC 2, NIST 800-171, ISO 27001, etc.);
- Focused on supporting processes and practices that must exist for a security, compliance and resilience program to operate effectively and efficiently;
- Designed to proactively address the strategic, operational and tactical nature of operating an entity’s security, compliance and resilience program; and
- Designed to address both internal controls, as well as the broader concept of Cybersecurity Supply Chain Risk Management (C-SCRM).
This document can help an entity understand the variables that make up the “Who? What? When? Where? How? and Why?” questions that arise when designing, implementing and maintaining secure, compliant and resilient capabilities.
1.5 Risk-Based Governance Practices
Secure, compliant and resilient capabilities exist when applicable controls are properly scoped and implemented. The SCRMS specifically addresses the need to clarify the difference between "compliant" versus "secure" since that understanding is necessary to have coherent risk management discussions.
To assist in this process, an entity’s applicable controls are categorized according to “must have” vs “nice to have” requirements:
- Minimum Compliance Requirements (MCR) are the absolute minimum requirements that must be addressed to comply with applicable laws, regulations and contracts (e.g., mandatory requirements). MCR are primarily externally-influenced, based on industry, government, state and local regulations. MCR should never imply adequacy for secure practices and data protection, since they are merely compliance-related.
- Discretionary Security Requirements (DSR) are tied to the entity’s risk appetite since DSR are “above and beyond” MCR, where the entity self-identifies additional security, compliance and resilience controls to address voluntary industry practices or internal requirements, such as findings from internal audits or risk assessments (e.g., discretionary requirements). DSR are primarily internally-influenced, based on the entity’s respective industry and risk tolerance. While MCR establish the foundational floor that must be adhered to, DSR are where entities often achieve improved efficiency, automation and enhanced security.
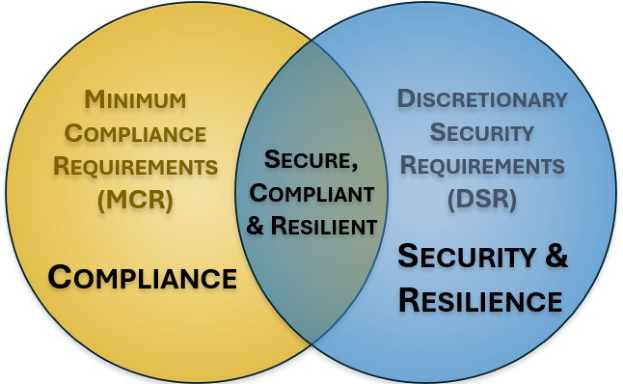
The combination of MCR and DSR equate to an entity’s Minimum Security Requirements (MSR), which define the “must have” and “nice to have” requirements in one control set. This control set defines the Minimum Viable Product (MVP) technical and business requirements from a security, compliance and resilience perspective. The MSR can be considered to be an entity’s IT General Controls (ITGC), which establish the necessary controls that must be applied to applicable Technology Assets, Applications, Services and/or Data (TAASD).
1.6 Integrated Controls Management (ICM): Controls Centric Mindset
The SCRMS is controls-centric, where controls are viewed as the nexus, or central pivoting point, for an entity’s security, compliance and resilience operations. This affects the entity’s overall business rhythm, since the controls used to define “secure practices” have both direct and indirect impacts on the TAASD that business operations rely upon.
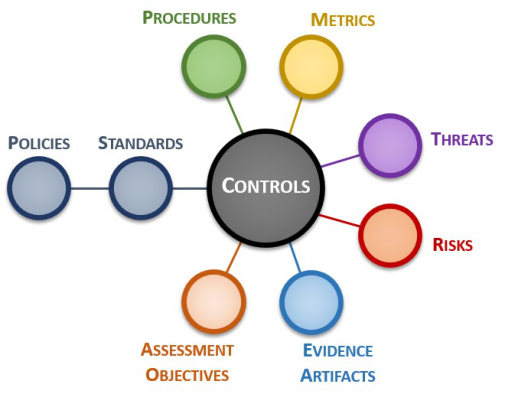
The graphic helps visualize the controls-centric nature of the SCRMS:
- Policies are enforced by standards, which map to controls.
- Procedures are “control activities” that describe the formal processes in place to operationalize a control.
- Metrics (including analytics) are tied to control execution.
- Threat catalogs should map threats to controls, since threats affect control execution.
- Risk catalogs should map risk to controls, since risks exist from control deficiencies and/or absences.
- Evidence artifacts provide evidence of due diligence and due care that controls operate.
- Assessment Objectives (AOs) are tied to controls to provide objective criteria to determine control implementation and operation.
1.7 Understanding Risks vs Threats
With the understanding that controls are the nexus of a security, compliance and resilience program. To progress from identifying an entity’s specific MCR and DSR to making a determination of risks and threats, it is important to baseline the understanding of risk and threat management terminology.
Risk Determination
A risk is:
- Noun: A situation where someone, or something valued, is exposed to danger, harm or loss; or
- Verb: To expose someone or something valued to danger, harm or loss.
In order to determine if something is a risk, address it as a question of, “Does the issue / event being assessed relate to either (1) the existence of or (2) a deficiency with an existing control (e.g., safeguard)?”
- If it does, the entity may be exposed to one, or more, risks.
- Those risks are expected to be documented in a risk catalog that is specific to the entity.
If the issue / event being assessed does not relate to either (1) the existence of or (2) a deficiency with an existing control, then it may be a threat.
Threat Determination
A threat:
- Noun: Is a person, or thing, likely to cause damage or danger; or
- Verb: Indicates impending damage or danger.
In order to determine if something is a threat, address it as a question of “Does the issue / event being assessed affect control execution (e.g., the ability of the safeguard to function as intended)?”
- If it does, the entity may be exposed to one, or more, threats; and
- Those threats are expected to be documented in a threat catalog that is specific to the entity. Ideally, the threats are broken down into natural and man-made threats.
Risk vs Threat Ecosystem: Path To Better Communications
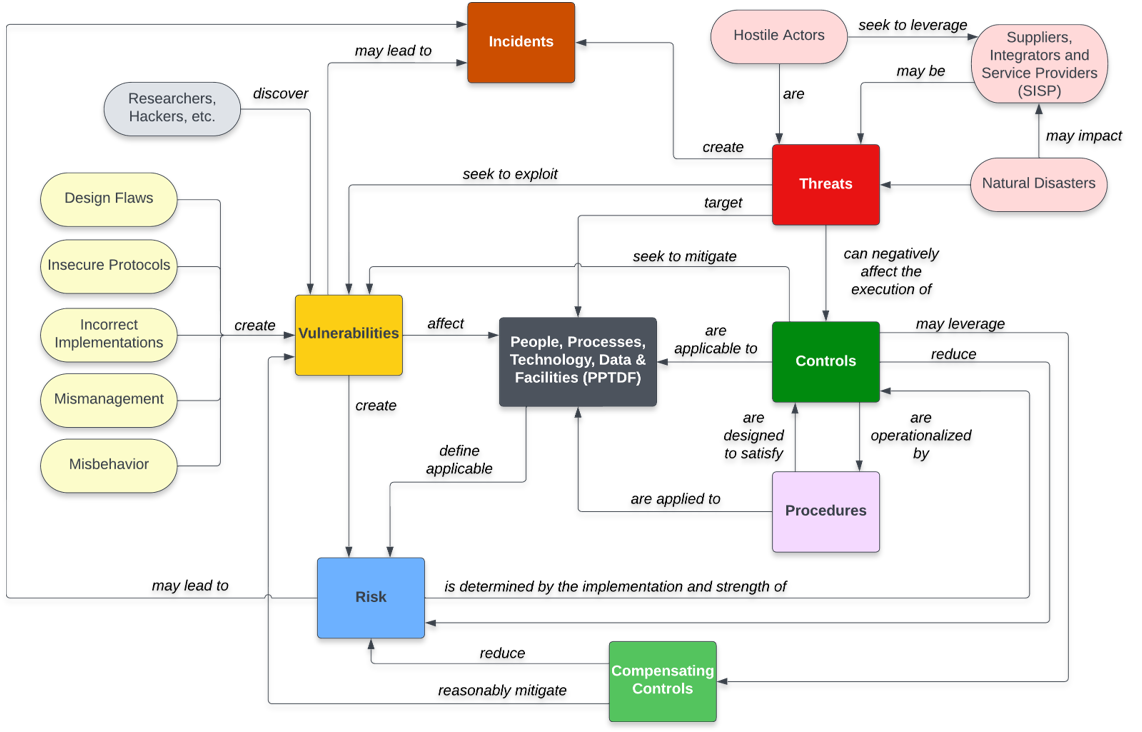
Risk, threat and vulnerability management practices are meant to achieve a minimum level of protection that equates to a reduction in the total risk due to the safeguards an entity implements via controls. From an ecosystem perspective, the many components have unique meanings that need to be understood to reasonably protect PPTDF. Understanding the context of how these components integrate can lead to more meaningful communications and practical risk management practices:
1.8 Prohibitions
The following usages of this content are strictly prohibited:
- Use without proper attribution to the SCF Council;
- Creating derivative works based on this content;
- Training Artificial Intelligence (AI) technologies; and/or
- Use as part of an AI dataset or any other AI-related activities.
1.9 Liability Limitations
THIS CONTENT IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE CONTENT OR THE USE OR OTHER DEALINGS IN THE CONTENT.
Normative References & Terminology Standardization
SCF Council Guidance
A normative reference is a reference document that is considered to be essential and indispensable to establish foundational practices.
Without the following normative reference(s) being utilized, the entity’s Secure, Compliant & Resilient Management System (SCRMS) is unlikely to be fully or correctly implemented:
- Secure Controls Framework (SCF);
- Unified Scoping Guide (USG);
- Secure, Compliant & Resilient Risk Management Model (SCR-RMM);
- Secure, Compliant & Resilient Capability Maturity Model (SCR-CMM); and
- Secure, Compliant & Resilient Assessment Standards (CDPAS).
From the context of applying a standard to the Secure, Compliant & Resilient Management System (SCRMS), it is important to clarify mandatory versus optional criteria:
3.1 Authoritative Sources
The SCF Council recognizes two (2) primary sources for authoritative definitions for security, compliance and resilience terminology:
- The National Institute of Standards and Technology (NIST) IR 7298, Glossary of Key Cybersecurity Terms, is the approved reference document used to define cybersecurity-related terminology; and
- NIST Glossary.
3.2 Definitions & Acronyms
The SCRMS defines the security, compliance and resilience terms it uses, from Adequate Security to Trust, and includes a full list of acronyms. Both lists are in the SCRMS PDF.
How Is The SCRMS Organized?
Sections 1 to 10 set out the model, including its nine principles and how to determine the control set. Section 11 lists the due diligence requirements by Secure Controls Framework (SCF) domain, Section 12 covers due care, and Section 13 covers demonstrating assurance to stakeholders.
Introduction
There are two (2) fundamental goals of the Secure, Compliant & Resilient Management System (SCRMS):
- Provide the structure for an entity to be secure, compliant and resilient; and
- Generate defensible evidence of due diligence and due care that is capable of defending the entity’s security, compliance and resilience practices to against legal challenges, if an incident should occur.
This defensibility is anchored in the Living Control Set (LCS), which converts governance intent into defined, prioritized and testable control expectations.
An entity’s status can be visualized as being in one (1) of four (4) maturity-based quadrants where that entity is either:
- Not secure, resilient or compliant (negligent);
- Secure & resilient, but not compliant;
- Compliant, but not secure or resilient; or
- Secure, resilient & compliant.
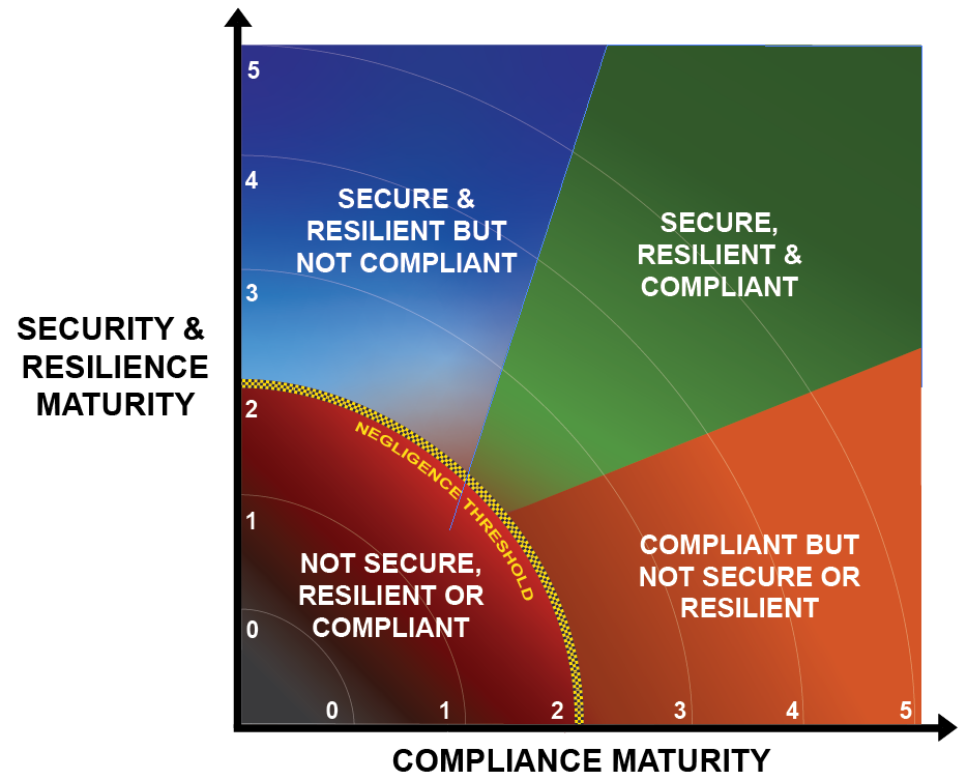
This concept of identifying a negligence threshold is addressed in the SCF’s Secure, Compliant & Resilient Capability Maturity Model (SCR-CMM).
4.1 Defensible Evidence
Artifacts must be adequate and sufficient. Defensible evidence is documented evidence that is so well-collected and preserved that the adequacy and sufficiency of those artifacts are:
- Irrefutable, where its authenticity and integrity make the artifacts admissible in court or formal proceedings; and
- Capable of withstanding legal challenges (e.g., auditor, regulator, class action lawsuit, etc.).
Defensible evidence:
- Should be viewed as the “natural byproduct” of secure, compliant and resilient practices, where this evidence can be leveraged to support a claim or argument effectively because its origin(s) and handling are standardized and legally sound; and
- Must demonstrate conformity with the entity’s LCS, including validation of material controls and documented risk decisions.
4.2 Understanding Security vs Compliance vs Resilience
The terms security, compliance and resilience are unique, where each has its own specific meaning.
What Does It Mean To Be Secure?
An entity can reasonably claim it is secure if it has implemented and operational defenses focused on Confidentiality, Integrity, Availability and Safety (CIAS). An entity’s level of security is dynamic, based on its:
- Implemented defensive capabilities; and
- Applicable risks and threats.
Effective security requires a unified effort involving those that interact with the entity’s Technology Assets, Applications, Services and/or Data (TAASD). Commensurate with applicable risk and threats, security, compliance and resilience measures must be implemented to guard against unauthorized access to, alteration, disclosure or destruction of TAASD. This also includes protection against accidental loss or destruction. The protection of TAASD must include safeguards to offset possible threats, as well as controls to ensure confidentiality, integrity, availability and safety:
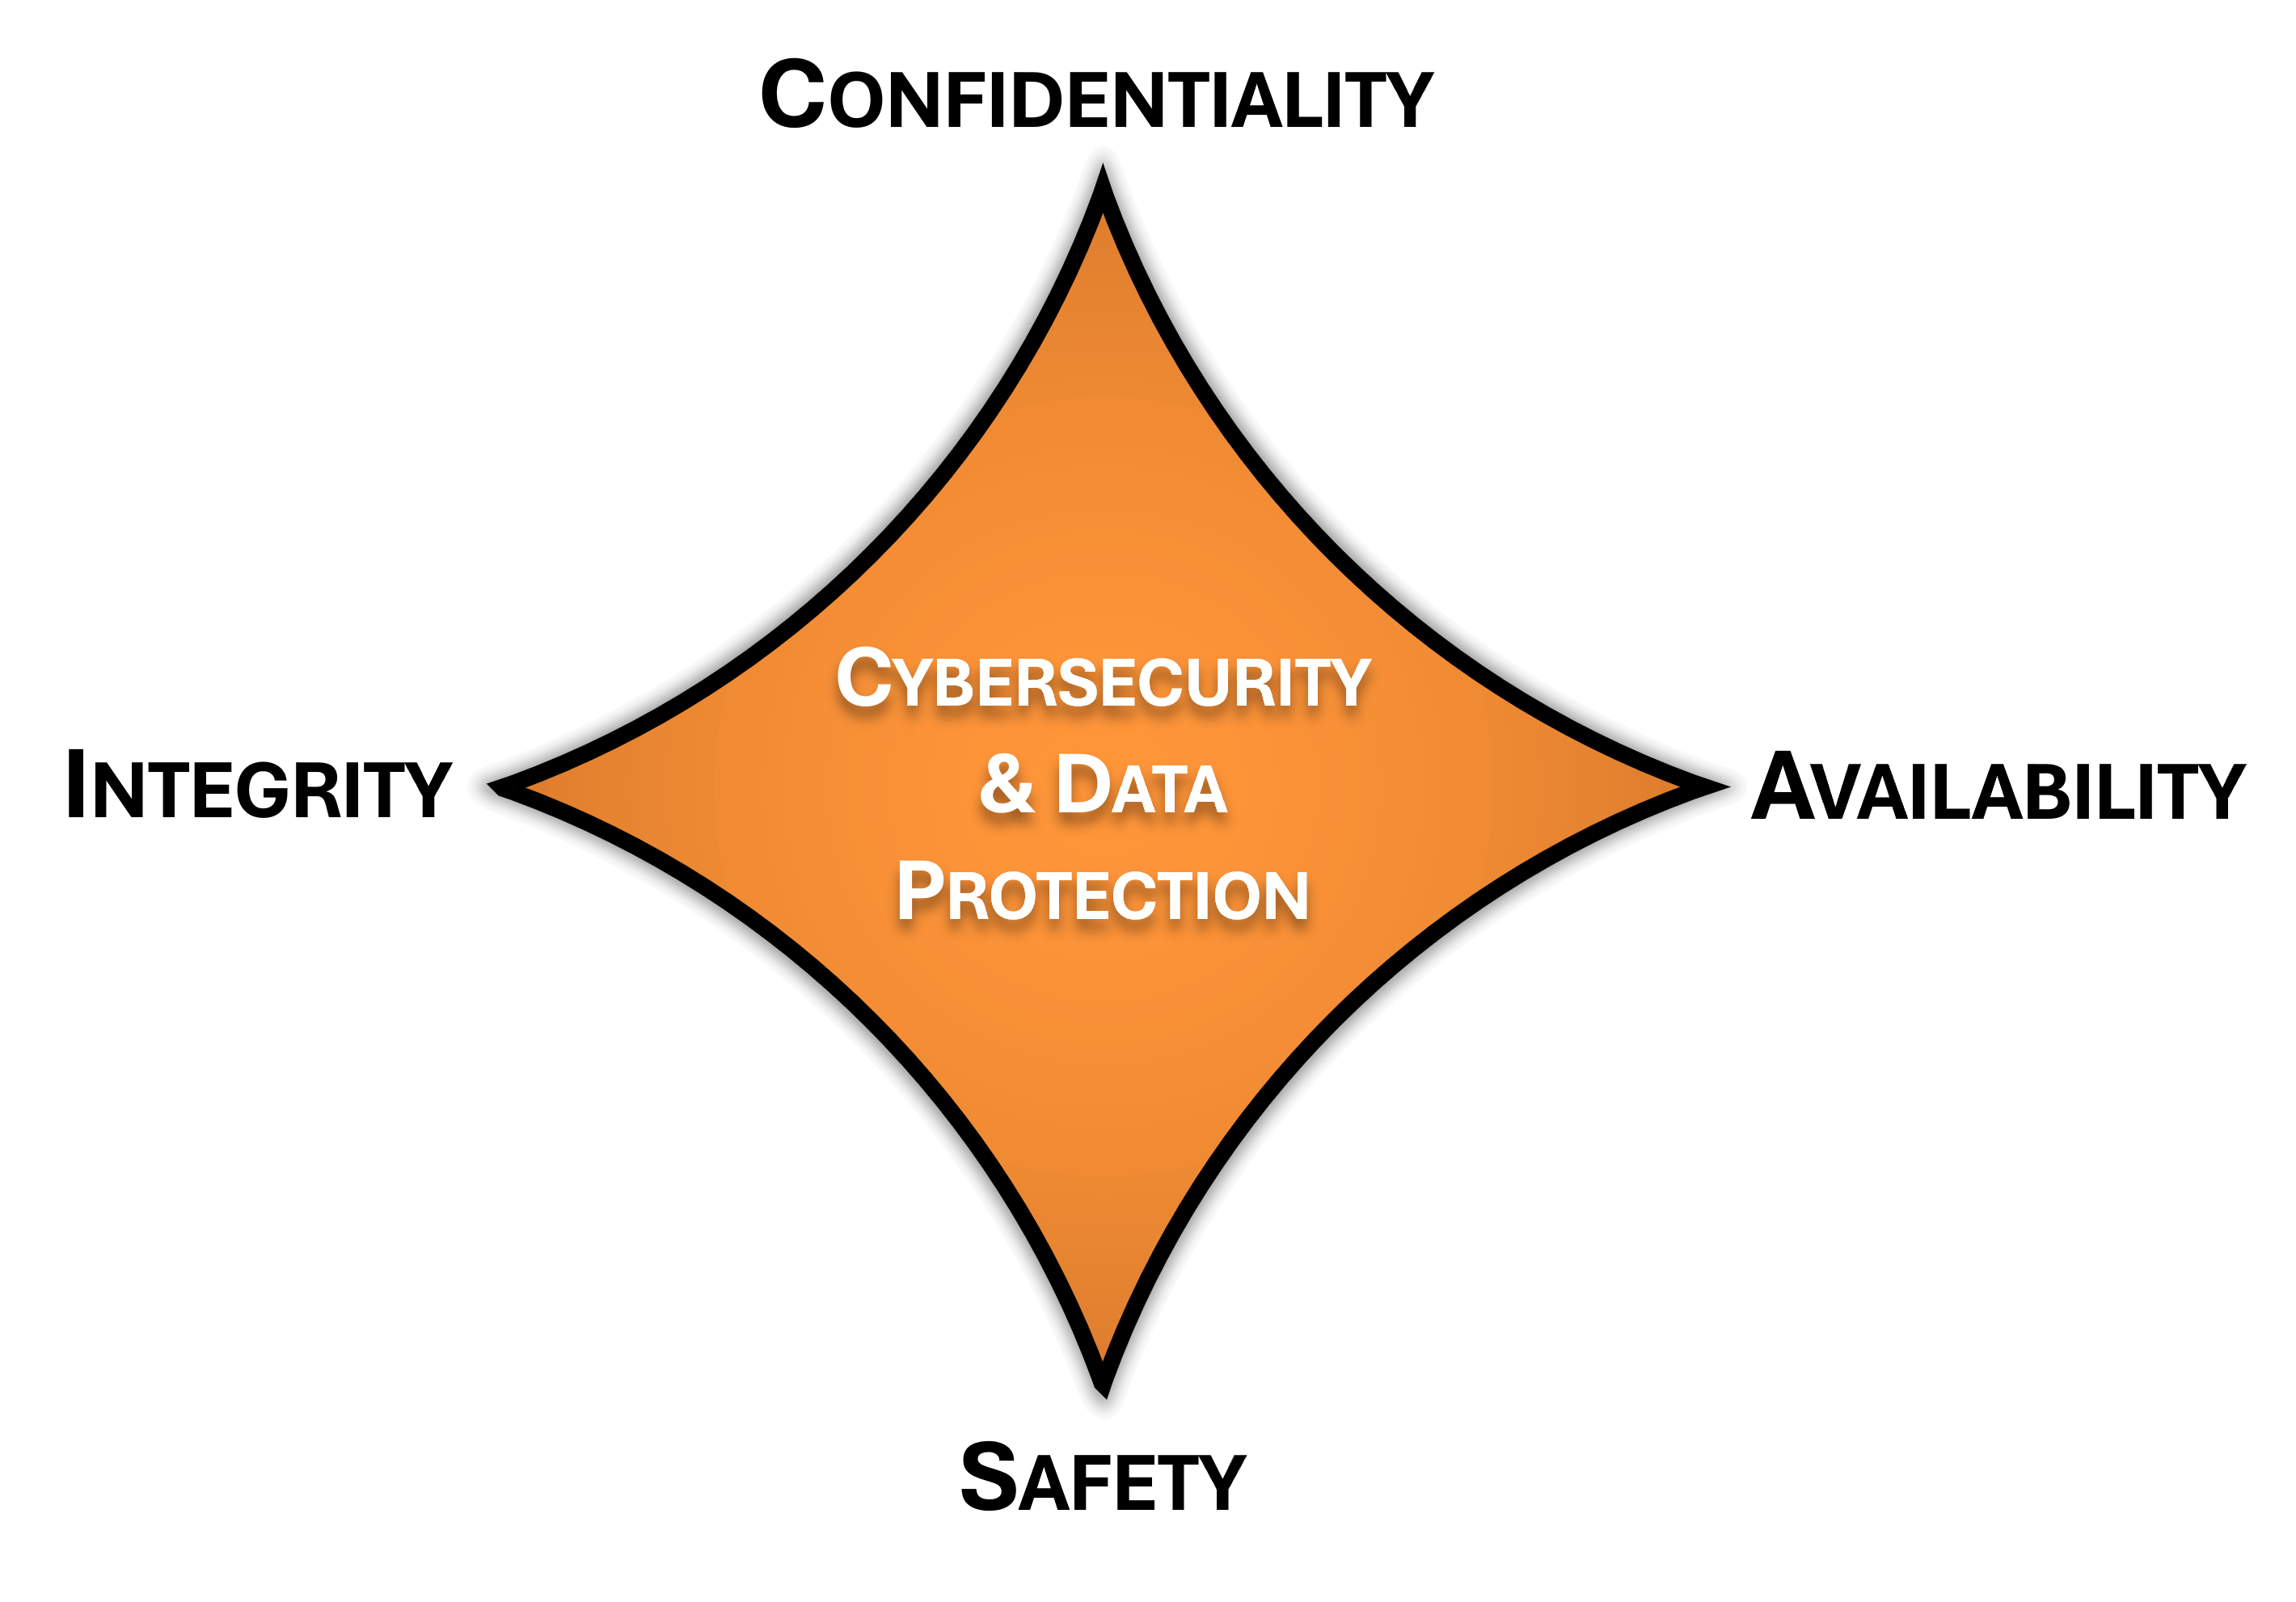
- Confidentiality: Addresses preserving authorized restrictions on access and disclosure to authorized users and services, including means for protecting personal data privacy and proprietary information.
- Integrity: Addresses protecting against improper modification or destruction, including ensuring non-repudiation and authenticity.
- Availability: Addresses timely, reliable access to data, systems and services for authorized users, services and processes.
- Safety: Addresses reducing risk associated with technologies that could fail or be manipulated by nefarious actors to cause death, injury, illness, damage to or loss of equipment.
What Does It Mean To Be Compliant?
An entity can reasonably claim it is compliant if it has the ability to demonstrate conformity with applicable laws, regulations and other obligations. The scope of compliance includes both external and internal requirements.
What Does It Mean To Be Resilient?
An entity can reasonably claim it is resilient if it has prepared for and has the ability to adapt to changing conditions, where it can withstand and/or recover rapidly from disruption.
Resilience includes the ability to withstand and recover from deliberate attacks, accidents or naturally occurring threats or incidents.
4.2.3.1 Pre-Event Focus
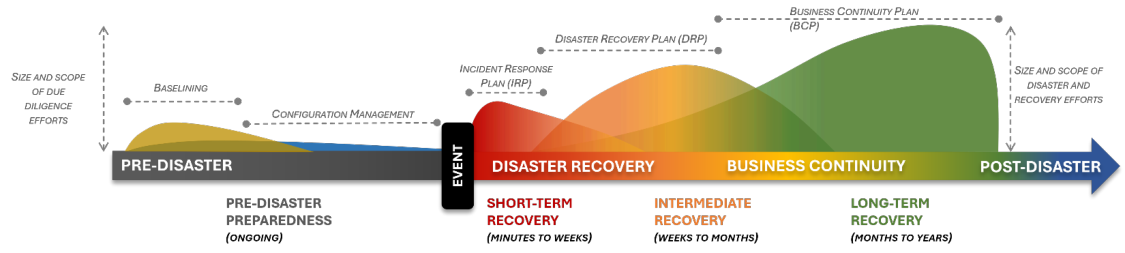
An entity that focuses on “left of event,” or pre-event preparedness, indicates a commitment to resiliency, based on its ability to minimize negative business impacts from reasonably anticipated incidents and/or threats.
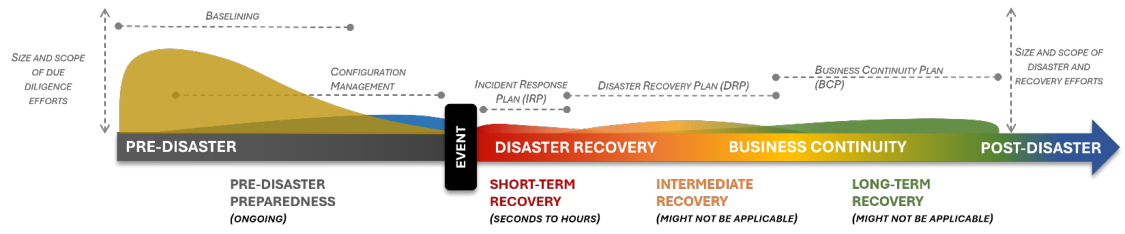
4.2.3.2 Post-Event Focus
An entity that focuses on “right of event,” or post-event preparedness, indicates a lack of commitment to resiliency, based on the forecast difficulties and length of duration the business will experience operational impacts. Recovery planning by itself does not equate to resiliency, since the business interruptions during the recovery phase may be insurmountable if not tied to business uptime requirements (e.g., meet Service Level Agreements (SLAs), customer satisfaction goals, etc.).
4.3 Defining Negligence As It Pertains To Secure, Compliant & Resilient Practices
The following content is leveraged from Cornell’s Law School Legal Information Institute (LII) to provide context on the concept of negligence.
Negligent conduct may consist of either an act or an omission to act when there is a duty to do so. Primary factors to consider in ascertaining whether the person's conduct lacks reasonable care are:
- The foreseeable likelihood that the person's conduct will result in harm;
- The foreseeable severity of any harm that may ensue; and
- The burden of precautions to eliminate or reduce the risk of harm.
Four (4) elements are generally required to establish a prima facie case of negligence:
- Existence of a legal duty that the defendant owed to the plaintiff.
- Example: A requirement to comply with NIST SP 800-171 to protect Controlled Unclassified Information (CUI) as part of a contract.
- Defendant's breach of that duty.
- Example: A failure to protect CUI in accordance with NIST SP 800-171 requirements under applicable DFARS clauses.
- Plaintiff's sufferance of an injury.
- Example: Financial losses due to fines and/or lost contracts stemming from non-compliance with DFARS clauses.
- Proof that defendant's breach caused the injury.
- Example: A whistleblower claims, forensic investigations and/or publicity about the data breach or other evidence pointing to the entity being the source of the data breach.
Typically, to meet the injury element of the prima facie case, the injury must be one (1) of two (2) things:
- Bodily harm; and/or
- Harm to property (can be personal property or business property (physical or digital)).
Determining A Breach Of Duty
In determining whether the defendant has breached a duty, courts may use the Learned Hand Formula, which is an algebraic approach to determining liability. If B < PL, then there will be negligence liability for the party with the burden of taking precautions where:
- B = Burden of taking precautions
- P = Probability of loss
- L = Gravity of loss
If the burden of taking such precautions is less than the probability of injury multiplied by the gravity of any resulting injury, then the party with the burden of taking precautions will have some amount of liability.
Determining Whether There Was A Duty To Act
Typically, if the defendant had a duty to act, did not act (resulting in a breach of duty) and that breach of duty caused an injury, then the defendant's actions will be classified as misfeasance. There are several ways to determine whether the defendant had a duty to act:
- The defendant engaged in the creation of the risk which resulted in the plaintiff's harm;
- The defendant volunteered to protect the plaintiff from harm;
- The defendant knew / should have known that the conduct will harm the plaintiff; or
- Business/voluntary relationships.
Scope of Secure, Compliant & Resilient Activities
An entity’s Secure, Compliant & Resilient Management System (SCRMS) is designed to address a Plan, Do, Check and Act (PDCA) approach for continuous improvements that span development, implementation, maintenance and remediation activities.
SCF Council Guidance
Scoping is an activity that spans both due diligence and due care. The concept of “gaming” the scope of an assessment or accreditation boundary to minimize the deployment of reasonable controls for the sake of obtaining a certification is disingenuous and borders on fraud when that audit or certification is used to market the security, compliance and/or resilience capabilities of an entity. Activities that alter the scope of controls for the perceived benefit of the entity create a potential material misrepresentation of risk.
From a SCRMS perspective, the goal is for compliance to be a natural byproduct of secure and resilient capabilities, so entities should focus on secure engineering and data protection principles to guide the development, implementation and operation of its security, compliance and resilience program.
5.1 Scope Determination
The scope of the SCRMS encompasses:
- The entity, as a whole (e.g., business units, departments, geographies, personnel, etc.); and
- Any entity that directly or indirectly affects the security, compliance and/or resilience of the entity.
Entities that have the potential to directly or indirectly affect security, compliance and/or resilience capabilities include:
- Cloud Service Providers (CSPs) are external entities that provide on-demand network access to shared, configurable computing resources such as networks, servers and storage (e.g., Platform as a Service (PaaS), Infrastructure as a Service (IaaS) and Software as a Service (SaaS)).
- External Service Providers (ESPs) include, but are not limited to:
- Software as a Service (SaaS) solutions include, but are not limited to:
- Managed Service Provider (MSP) that includes but is not limited to the following managed Information Technology (IT) services: Helpdesk; Remote data backups; Network administration; and System maintenance.
- Managed Security Services Provider (MSSP) include but are not limited to the following cybersecurity services: Threat detection and analytics; Vulnerability assessments; and Incident response.
- Human Resources (HR) augmentation, including but not limited to: Timesheets; Personnel management; Recruitment; Benefits management; and Payroll.
- Business operations augmentation, including but not limited to: Managed phone systems; Facilities management automation;
- Delivering supplementing resources where a third-party provides skills or capacity that is lacking by the entity. This includes, but is not limited to:
- Staff augmentation;
- Specialized expertise (e.g., consultants);
- Software development;
- Marketing agency support;
- Facilities maintenance services;
- Legal services;
- Financial services; and
- Colocation facilities (COLO); and
- Material suppliers include, but are not limited to:
- Raw materials; and
- Components needed for products and/or services.
SCF Council Guidance
The difference between a CSP and ESP can sometimes be nuanced. Following the stringent definitions set forth by the US Department of Defense, the SCRMS adopts the following interpretation:
CSP means an external company that provides cloud services based on cloud computing. Cloud computing is a model for enabling ubiquitous, convenient, on-demand network access to a shared pool of configurable computing resources (e.g., networks, servers, storage, applications and services) that can be rapidly provisioned and released with minimal management effort or service provider interaction.
An ESP would be considered a CSP when it provides its own cloud services based on a model for enabling ubiquitous, convenient, on-demand network access to a shared pool of configurable computing that can be rapidly provisioned and released with minimal management effort or service provider interaction.
An ESP would not be considered a CSP when it provides technical support services to its clients. It would be considered a Managed Service Provider (MSP) or Managed Security Services Provider (MSSP) where:
- It does not host its own cloud platform offering;
- It may utilize cloud offerings to deliver services to clients without being a CSP; and
- An ESP that manages a third-party cloud service on behalf of a client would not be considered a CSP.
5.2 Control Applicability
Cybersecurity practitioners generally agree that the importance of robust security, compliance and resilience controls cannot be overstated. However, the applicability of those controls is sometimes in question since not all controls are applicable. To help demonstrate the applicable nature of controls:
- An employee cannot have a secure baseline configuration applied.
- An Incident Response Plan (IRP) cannot sign a Non-Disclosure Agreement (NDA), use Multi-Factor Authentication (MFA) or be patched.
- An entity cannot apply end user training to a firewall.
- Sensitive and/or regulated data cannot be assigned roles and responsibilities.
- A data center cannot undergo employee background screening.
Note
Applicability determinations directly affect inclusion within the Living Control Set (LCS) and therefore must be formally documented.
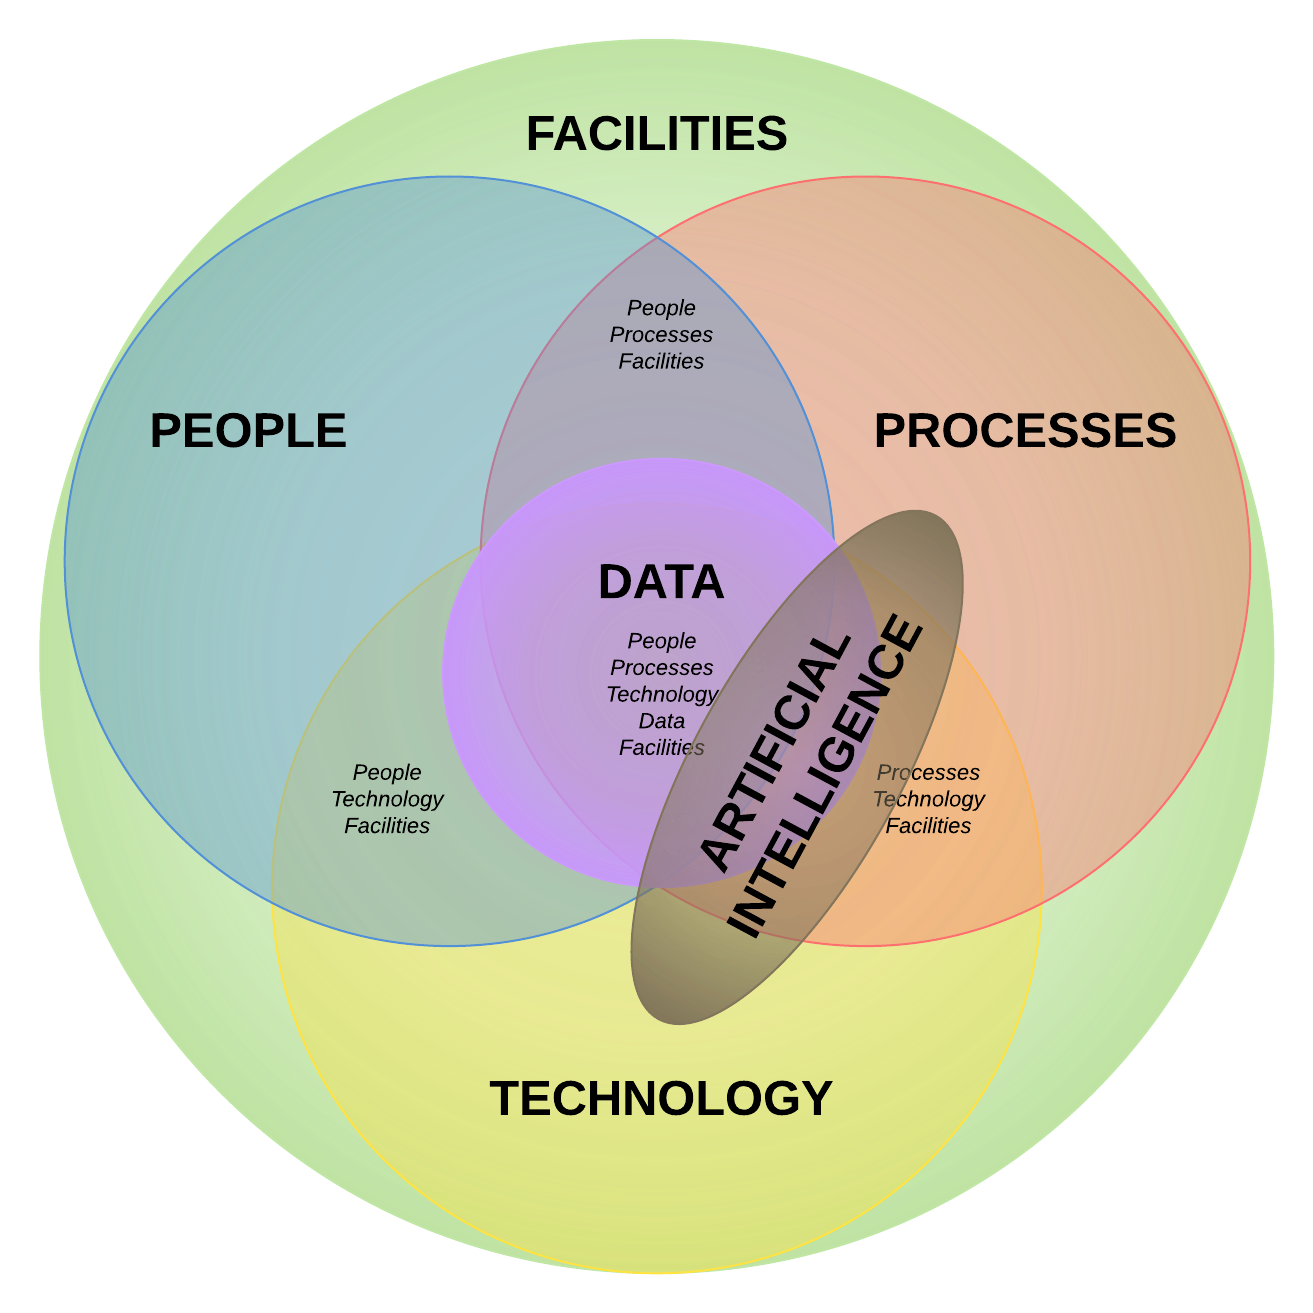
5.3 People, Processes, Technology, Data, Facilities & Artificial Intelligence (PPTDF-AI)
The People, Processes, Technology, Data, Facilities & Artificial Intelligence (PPTDF-AI) model provides a comprehensive approach to address control applicability. These five (5) core components provide a lens to view the applicability of controls:
- People. Control directly applies to humans (e.g., training, background checks, non-disclosure agreements, etc.).
- Processes. Control directly applies to administrative work performed (e.g., processes, procedures, administrative documentation, etc.).
- Technologies. Control directly applies to systems, applications and services (e.g., secure baseline configurations, patching, etc.).
- Data. Control directly applies to data protection (e.g., encrypting sensitive and/or regulated data, applying metatags, etc.).
- Facilities. Control directly applies to infrastructure assets (e.g., physical access, HVAC systems, visitor control, etc.).
Artificial Intelligence (AI), Machine Learning (ML) and related autonomous technologies span technologies and processes.
Secure, Compliant & Resilient Management System (SCRMS) Principles
An entity’s cybersecurity program becomes defensible when evidence exists to prove:
- Risks were identified;
- Controls were recommended; and
- Leadership made informed decisions.
This methodical approach creates a legally defensible paper trail. The principles of the SCRMS can help an entity create and maintain this defensible evidence. The following Annexes provide CISO-focused guidance on this topic:
- Annex 3: Defensible Evidence; and
- Annex 4: Planning For Resistance.
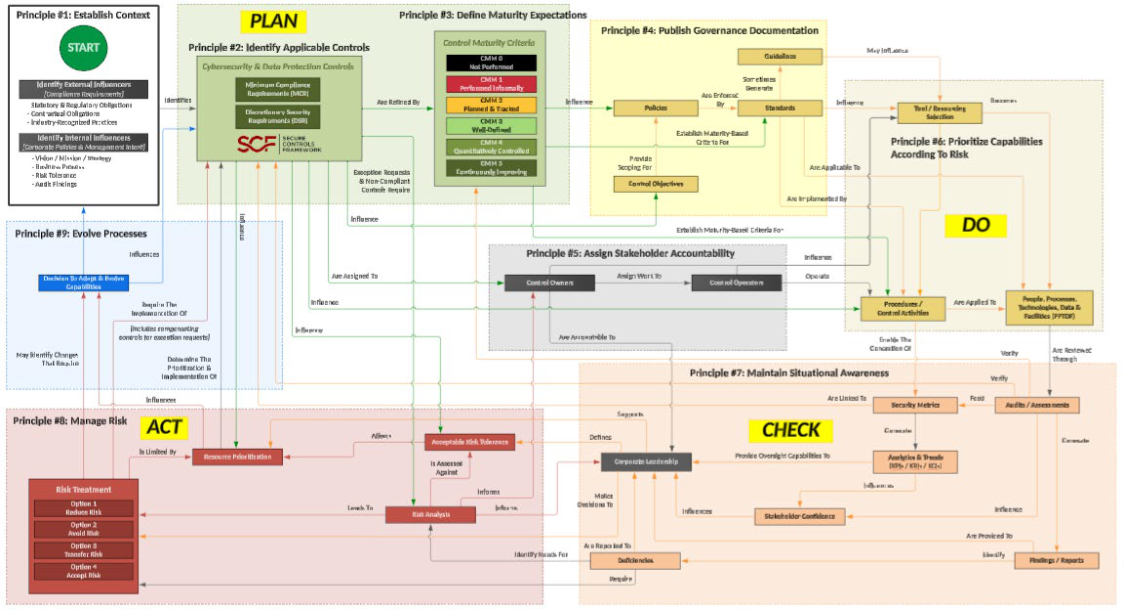
6.1 SCRMS Principles
There are nine (9) principles associated with the Secure, Compliant & Resilient Management System (SCRMS):
- Establish Context
- Identify Applicable Controls
- Define Maturity Expectations
- Publish Governance Documentation
- Assign Stakeholder Accountability
- Prioritize Capabilities According To Risk
- Maintain Situational Awareness
- Manage Risk
- Evolve Processes
Note
Principle #2 is where the Living Control Set (LCS) is established. As processes evolve and require adjustment, the LCS should be updated in Principle #9.
6.2 SCRMS Principle 1: Establish Context
To build and maintain efficient and effective operations, a security, compliance and resilience program must have a hierarchical vision, mission and strategy that directly supports the entity’s broader strategic objectives and business processes. This process of establishing context involves identifying all applicable external compliance requirements (e.g., laws, regulations and contractual obligations), internal directives (e.g., Board of Directors, corporate policies, etc.). This also includes understanding applicable risks and threats, since the entity’s exposure to those may influence the need for controls beyond those that are mandated as compliance obligations.
Establishing context is both a due diligence and due care element of an entity’s security, compliance and resilience program, since context changes with time. Things to consider when establishing context:
- Mission / vision / strategy of the entity;
- Statutory (law), regulatory (regulation) and contractual requirements for security, compliance and resilience;
- Fiscal constraints;
- The entity’s structure;
- The entity’s risk profile (including risk appetite, risk tolerance and risk threshold considerations);
- Planned entity changes (e.g., Mergers, Acquisitions & Divestitures (MA&D));
- Corporate culture (e.g., how receptive is the entity to change); and
- Geographic-specific requirements.
SCF Council Guidance
Part of an entity’s due diligence activities involve establishing the context for the SCRMS. Practical steps to establish context for the SCRMS include talking with representatives outside of IT and cybersecurity to document the following information:
- The entity’s structure:
- Reporting structure (e.g., chain of command);
- IT / cybersecurity governance stakeholders;
- Supply chain partners; and
- Geographic locations;
- The entity’s:
- Mission;
- Vision; and
- Strategy;
- Risk management practices:
- Risk tolerance;
- Risk appetite; and
- Risk thresholds; and
- Constraints that affect business operations:
- Applicable legal obligations:
- Statutory (law);
- Regulatory (regulation); and
- Contractual requirements;
- Fiscal constraints; and
- Corporate culture (e.g., how receptive the entity is to change).
- Applicable legal obligations:
6.3 SCRMS Principle 2: Identify Applicable Controls
A tailored set of security, compliance and resilience controls must exist for an entity to implement a SCRMS. This control set needs to be tailored for the entity’s unique requirements, such as a combination of Minimum Compliance Requirements (MCR) and Discretionary Security Requirements (DSR). This blend of “must have” and “nice to have” requirements establish an entity’s tailored control set to help ensure secure, compliant and resilient capabilities.
SCF Council Guidance
Part of an entity’s due diligence process is to identify applicable security, compliance and resilience controls. Practical steps to identify applicable controls include:
- Reading through the Secure Controls Framework (SCF) principles to become familiar with the thirty-three (33) domains to understand how they come together to address the security, compliance and resilience considerations for a modern security, compliance and resilience program.
- As “business enablers,” CISOs should talk with representatives outside of IT and cybersecurity to gain an understanding of the entity’s complete scope of compliance requirements (e.g., legal, procurement, physical security, etc.).
- Developing a list of the “must have” laws, regulations and frameworks that the entity must comply with.
- Developing a list of “nice to have” requirements that the entity’s Board of Directors, or other stakeholders, feel are necessary.
Understanding the requirements for both security, compliance and resilience principles involves a simple process of distilling expectations. This process is all part of documenting reasonable expectations that are “right-sized” for an entity, since every entity has unique requirements.
There is no expectation for an entity to utilize all 1,400+ controls in the SCF catalog. It is best to visualize the SCF as a “buffet of security, compliance and resilience controls,” where the entity only selects those controls necessary to address its unique requirements. Once the entity knows what is applicable, it is possible to use the SCF to generate a customized control set that is specific to address the entity’s MCR and DSR.
Things to consider when defining applicable controls:
- Controls to address “must have” requirements from laws, regulations and contractual obligations to ensure the entity is compliant with its obligations;
- Controls to address “discretionary” requirements that exist to ensure the entity has secure and resilient operations; and
- There needs to be at least an annual review to ensure the applicable controls are accurate to the current needs for compliance, security and resilience.
6.4 SCRMS Principle 3: Define Maturity Expectations
The entity must define maturity expectations for its security, compliance and resilience controls. From the perspective of the SCRMS, the maturity expectations define entity-specific “what right looks like” expectations for control implementation and continued operation. The maturity-based criteria are applicable to People, Processes, Technologies, Data & Facilities (PPTDF).
Maturity targets are expected to directly support the entity’s need for security, compliance and resiliency capabilities. These maturity targets can be used by an entity’s leadership for:
- Multi-year business planning;
- Budgeting; and
- Assessment criteria.
SCF Council Guidance
The SCF uses the Secure, Compliant & Resilient Capability Maturity Model (SCR-CMM) criteria for each control. The SCR-CMM is an available option for maturity expectations for entities that lack maturity targets.
The SCR-CMM draws upon the high-level structure of the Systems Security Engineering Capability Maturity Model v2.0 (SSE-CMM), where it can be used to demonstrate varying levels of maturity for PPTDF at a control level.
Things to consider when assigning maturity-based criteria:
- Not all controls need to be the same level of maturity, since each control has an associated cost. The higher the level of maturity, the higher the cost. This is a risk management decision to define what right looks like for the entity;
- The expected level of maturity needs to at least comply with applicable statutory, regulatory and contractual requirements; and
- Lower levels of maturity may be considered negligent behavior from a due care perspective.
6.5 SCRMS Principle 4: Publish Governance Documentation
Cybersecurity and data protection documentation must exist, otherwise an entity’s governance practices are both unenforceable and indefensible. Formalizing entity-specific requirements via documented policies, standards and procedures are necessary to operationalize security, compliance and resilience controls.
Documented policies, standards and procedures provide evidence of due diligence that the entity identified and implemented reasonable steps to address its applicable requirements. The output of procedures provides evidence of due care that controls were operated as described.
Note
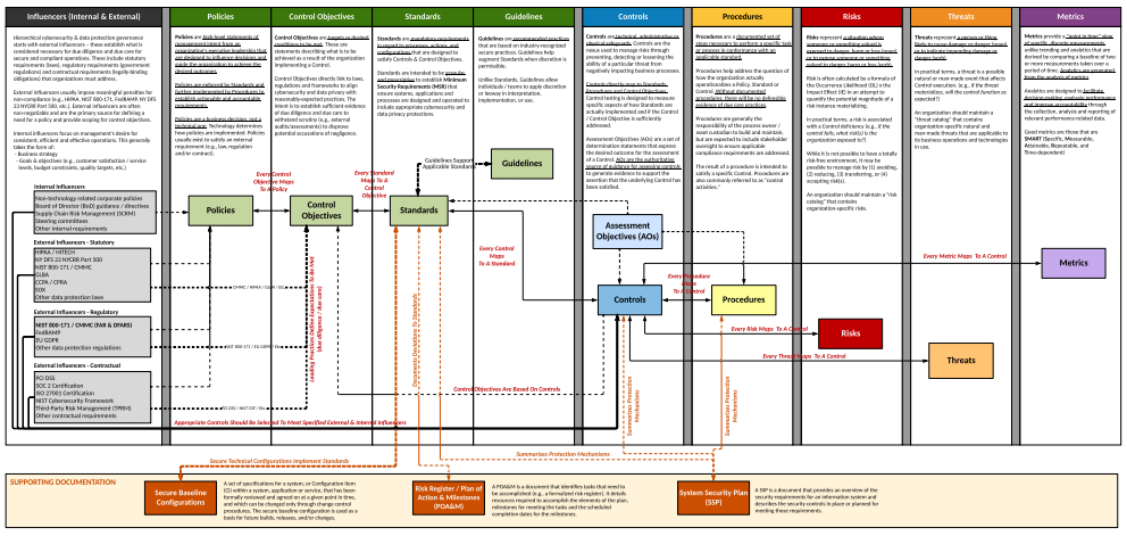
For governance practices, a reference model should be used to encourage clear communication by defining generally accepted security, compliance and resilience documentation components and how those are linked. This can provide a comprehensive understanding of primary documentation components that are necessary to demonstrate evidence of due diligence and due care. As a reference, the Hierarchical Cybersecurity Governance Framework (HCGF) addresses the interconnectivity of key cybersecurity documentation components.
SCF Council Guidance
There are generally three (3) options to generate security, compliance and resilience documentation:
- Use internal resources to write it in-house;
- Hire a consultant to write a bespoke set of documentation; or
- Purchase semi-customized templates online.
Things to consider when publishing policies & standards:
- Departments other than cybersecurity and data privacy publish policies, standards and procedures (e.g., HR, IT, Procurement, Legal, etc.) and those need to be reconciled to ensure interoperability.
- The policies and standards need to reflect both the “must have” and “nice to have” requirements identified in SCRMS Principle 2;
- Policies are designed as “high level statements of management intent” and are not expected to change often;
- Standards should be designed to assign granular requirements to enforce policies. As technologies change/evolve, those standards must be reviewed and updated, as necessary, to ensure secure, compliant and resilient capabilities; and
- Procedures should be written at a level of detail that makes it repeatable through clear steps, but should avoid unnecessary content that makes the procedures too difficult to maintain. As business processes or technologies change, procedures must be updated to reflect the new method(s) necessary to operate a control.
6.6 SCRMS Principle 5: Assign Stakeholder Accountability
Controls must be assigned to stakeholders to ensure accountability (e.g., business units, teams and/or individuals). These “control owners” are expected to assign the task of executing controls to “control operators” at the Individual Contributors (IC)- level.
- Stakeholders utilize the prescriptive requirements from policies and standards to develop Standardized Operating Procedures (SOP) that enable ICs to execute those controls.
- The documented execution of procedures provides evidence of due care that reasonable practices are being performed.
SCF Council Guidance
Assigning stakeholder accountability offers unique challenges for entities, since it is beyond IT, security, compliance and resilience. Common stakeholders involve Human Resources (HR), procurement, facilities management, legal and many other teams to ensure accountability is enforceable. Realistically, this step is an executive-management function since it requires inter-departmental enforcement by an entity’s management.
Things to consider when assigning stakeholder accountability:
- Procedures are not “owned” by the cybersecurity or privacy teams. Procedures are the responsibility of the control owner / operator; and
- The NIST SP 800-181, Workforce Framework for Cybersecurity (NICE Framework), is a methodology to identify security, compliance and resilience-related roles and associated responsibilities. The NICE Framework offers an efficient way to assign stakeholder accountability for internal and external stakeholders.
6.7 SCRMS Principle 6: Prioritize Capabilities According To Risk
Security, compliance and resilience capabilities must be prioritized based on applicable risks and threats. Not all risks and threats are equal, so a risk-based prioritization must occur.
SCF Council Guidance
Prioritization should be based on a CISO-level business plan that supports the entity’s broader mission and strategy. That department-level business plan would reasonably be a multi-year approach to address security, compliance and resilience capabilities. That formalized plan is used for resource allocation (e.g., staffing, technology purchases, service contracts, etc.) based on approval from the entity’s executive leadership.
Things to consider when prioritizing capabilities:
- Resources are finite, so a prioritized plan is expected to be spread out across multiple years; and
- The entity’s executive leadership is expected to approve the prioritized plan, where the decision for the approved Course of Action (CoA) is elevated above the CISO role.
6.8 SCRMS Principle 7: Maintain Situational Awareness
Situational awareness must involve more than merely “monitoring controls” (e.g., metrics). While metrics are a point-in-time snapshot into discrete controls performance, the broader view of metrics leads to a longer-term trend analysis (e.g., analytics). When properly tied in with current audits, control deficiencies, risk, threat and vulnerability information, this broader insight provides “situational awareness” that is necessary for an entity’s leadership to adjust plans to operate within the defined risk threshold.
SCF Council Guidance
Things to consider when maintaining situation awareness:
- Metrics/analytics tell the long-term story of how the security, compliance and resilience program is doing. This historical performance provides context to an entity’s senior leaders for decision-making purposes; and
- The metrics/analytics need to be tied to measurable controls that can help eliminate Fear, Uncertainty and Doubt (FUD) reporting.
Maintaining situational awareness has different meanings, based on the security culture of an entity. Metrics / analytics reporting is often plagued by the problem of Garbage In, Garbage Out (GIGO). Often, the GIGO issue is rooted in an entity’s executive leadership trying to explain their perceived needs for metrics to cybersecurity practitioners in a way that describes the design of a "football bat" (e.g., nonsensical solution). To combat GIGO, it is advisable to approach the problem from the perspective that executive management often just wants a simple answer to a relatively-straightforward question: “Are we secure?” The metrics and analytics should be able to answer that question with irrefutable evidence.
6.9 SCRMS Principle 8: Manage Risk
Proactive risk management processes must exist across all phases of Technology Assets, Applications, Services and/or Data (TAASD) life cycles to address Confidentiality, Integrity, Availability and Safety (CIAS) aspects. Based on finite resources (e.g., time, personnel and money), it is necessary to utilize prioritized risk management practices that ensure issues posing the highest risk are addressed first.
Risk management must address internal and external factors, including data privacy, Artificial Intelligence (AI), embedded technology and Supply Chain Risk Management (SCRM) considerations. To manage risk, it requires the entity to enforce a clearly-defined risk threshold and ensure reasonable security practices are operational.
SCF Council Guidance
Risk management involves coordinated activities that optimize the management of potential opportunities and adverse effects. Proactive risk management activities provide a way to realize potential opportunities without exposing an entity to unnecessary peril.
The goal of risk analysis is to determine the potential negative implications of an action or situation to determine one (1) of two (2) decisions:
- Acceptable Risk: the criteria fall within a range of acceptable parameters; or
- Unacceptable Risk: The criteria fall outside a range of acceptable parameters.
Traditional risk management practices have four (4) options to address identified risk:
- Reduce the risk to an acceptable level;
- Avoid the risk;
- Transfer the risk to another party; or
- Accept the risk.
In a mature risk program, the results of risk assessments are evaluated with the entity's risk appetite into consideration. For example, if the entity has a Moderate Risk Appetite and there are several findings in a risk assessment that are High Risk, then action must be taken to reduce the risk. Accepting a High Risk would violate the Moderate Risk Appetite set by management. In reality, this leaves remediation, transferring or avoiding as the remaining three (3) options, since accepting the risk would be prohibited.
There are many ways to manage risk. However, the SCF’s Secure, Compliant & Resilient Cybersecurity & Data Privacy Risk Management Model (SCR-RMM) contains a control-centric:
- Risk catalog;
- Threat catalog; and
- Methodology to not only perform a risk assessment, but manage risk across the entity.
The value of the SCR-RMM is having a standardized methodology where controls are tied to specific risks and threats. Based on the other criteria offered by the SCF (e.g., weighting and maturity criteria), the SCR-RMM makes calculating risk a straightforward process.
Controls are the nexus of a security, compliance and resilience program, so it is vitally important to understand how controls should be viewed from a high-level risk management perspective. To progress from identifying a necessary control to a determination of risk, it is a journey that has several steps, each with its own unique terminology. Therefore, it is important to baseline the understanding of risk management terminology.
6.10 SCRMS Principle 9: Evolve Processes
Cybersecurity and data protection measures must adapt and evolve to address business operations and the evolving threat landscape. This requires the adoption of a Plan, Do, Check & Act (PDCA) approach (e.g., Deming Cycle) to ensure the entity proactively identifies its requirements, implements appropriate protections, maintains situational awareness to detect incidents, operates a viable capability to respond to incidents and can sustain key business operations, if an incident occurs.
Things to consider when evolving processes:
- Changes in the compliance landscape (e.g., laws, regulations and contractual obligations);
- Technology changes; and
- Budget/resourcing constraints that affect how processes are implemented.
SCF Council Guidance
Things to consider when evolving processes:
- Changes in the compliance landscape (e.g., laws, regulations and contractual obligations);
- Technology changes; and
- Budget/resourcing constraints that affect how processes are implemented.
Without an overarching concept of operations for the SCRMS, entities will often find that their governance, risk management, compliance and data privacy teams are siloed in how they think and operate. These siloed functions and unclear roles often stem from a lack of a strategic understanding of how these specific functions come together to build a symbiotic working relationship between the individual teams that enables quality control over PPTDF.
The SCRMS utilizes a Plan, Do, Check & Act (PDCA) approach that is a logical way to design a governance structure:
- Plan. The overall SCRMS process beings with planning. This planning will define the policies, standards and controls for the entity. It will also directly influence the tools and services that an entity purchases, since technology purchases should address needs that are defined by policies and standards.
- Do. Arguably, this is the most important section for security, compliance and resilience practitioners. Controls are the “security glue” that make processes, applications, systems and services secure. Procedures (also referred to as control activities) are the processes in which the controls are actually implemented and performed.
- Check. In simple terms, this is situational awareness. Situational awareness is only achieved through reporting through metrics and reviewing the results of audits/assessments.
- Act. This is essentially risk management, which is an encompassing area that deals with addressing two main concepts (1) real deficiencies that currently exist and (2) possible threats to the entity.
Control Set Determination
The core of the SCRMS is the entity’s control set. Controls are central to security, compliance and resilience operations, as well as the overall business rhythm of any entity:
- Policies and standards should be hierarchically designed to support control objectives;
- Procedures are a form of control activity, describing how the control is operationalized; and
- Controls should be tied to metrics, threats and risks.
7.1 Establishing Minimum Security Requirements (MSR)
The combination of MCR and DSR equate to an entity’s Minimum Security Requirements (MSR), which define the “must have” and “nice to have” requirements for PPTDF in one control set. It defines the Minimum Viable Product (MVP) technical and business requirements from a security, compliance and resilience controls perspective.
Controls that comprise the MSR are expected to be applied to Technology Assets, Applications, Services and/or Data (TAASD) across the entity. ITGC provide the foundation of assurance for an entity’s decision makers. MSR:
- Includes traditional IT General Controls (ITGC) controls; and
- Enables an entity’s governance function to define how Technology Assets, Applications and Services (TAAS) are designed, implemented and operated.
Together, MCR and DSR form the entity’s MSR.
7.2 Living Control Set (LCS)
The concept of a Living Control Set (LCS) is to define the authoritative definition of what “reasonable security, compliance and resilience” means for the entity at a specific point in time. The LCS is not a static catalog of controls, nor is it a generic framework mapping. It is the entity-specific instantiation of control expectations derived from:
- MCR;
- DSR;
- The entity’s risk appetite, risk tolerance and risk thresholds; and
- Explicit materiality criteria for risks, threats, incidents and controls.
The MSR defines the minimum defensible baseline required for the entity to demonstrate that its steady-state operations are secure, compliant and resilient:
- The MCR establishes the “ground floor” for compliance efforts that is based on non-negotiable obligations imposed by laws, regulations and contracts.
- The DSR represents risk-justified enhancements necessary to operate within the entity’s defined risk tolerance and threat environment.
- It is important to clarify that DSR are not optional enhancements, since the entity’s risk, threat exposure, or materiality thresholds justify them; and
- DSR should be viewed as mandatory elements of the LCS, just as MCR are.
The LCS functions as the foundational layer of the SCRMS (e.g., SCRMS Principle #2). It establishes:
- What controls must exist;
- How those controls are prioritized;
- Which controls are considered material; and
- How control effectiveness is validated over time.
All subsequent governance, risk management, assessment and oversight activities operate against the LCS as the single source of truth.
Authoritative Nature of the LCS
The LCS is approved under the entity’s defined governance authority (e.g., steering committee, CISO or GRC Director). Changes to the LCS must be documented, justified and traceable to one or more of the following:
- Changes in statutory, regulatory and/or contractual obligations;
- Emerging threats or shifts in risk exposure;
- Adjustments to risk appetite, tolerance and/or threshold;
- Lessons learned from incidents and/or capability testing; or
- Significant business changes (e.g., new products, acquisitions, divestitures, geographic expansion, etc.).
Managing the triggers for adjusting the LCS ensures that the definition of “reasonable” evolves deliberately, rather than informally.
Control Weighting and Material Controls
Not all controls are equal. Within the LCS, controls are assigned relative weighting to reflect their impact on the entity’s ability to operate within its defined risk thresholds. Controls designated as material controls represent conditions where:
- No reasonable compensating control can offset their failure; and
- A deficiency would likely exceed defined materiality thresholds.
Material controls receive:
- Elevated maturity expectations;
- Increased oversight and reporting visibility;
- Priority in funding and remediation sequencing; and
- Explicit validation cadence requirements.
This weighting model prevents the false equivalence of controls commonly found in certification-driven management systems.
Evolution of the LCS
The LCS is referred to as “living” because it is subject to continuous governance review and modification. Its evolution is driven by:
- Evolving risk and threat landscape;
- Evolving compliance obligations;
- Results from conformity testing (e.g., control testing);
- Results from periodic risk assessments;
- Threat intelligence updates;
- Incident root cause analysis;
- Third-party risk findings; and
- Directives from the entity’s strategic business planning cycles.
Updates to the LCS must preserve traceability so that historical decisions can be reconstructed for the possible scenarios where those decisions will be scrutinized by regulators, auditors, insurers and/or courts.
Governance and Oversight
The entity’s mid-level and senior management roles are responsible for implementing and operating controls defined in the LCS.
The entity’s executive leadership and the Board of Directors (BoD) are responsible for:
- Approving risk appetite and materiality thresholds;
- Reviewing material control status;
- Monitoring unresolved material risks; and
- Challenging assumptions regarding control effectiveness and risk exposure.
Through this separation, the LCS becomes the anchor for both due diligence (building capabilities) and due care (governing and evolving them).
Outcome
By defining, weighting and governing the LCS in this manner, the entity can demonstrate that:
- Controls were selected intentionally;
- Resources were allocated based on material risk;
- Oversight occurred at appropriate levels; and
- Security, compliance and resilience decisions were reasonable, documented and defensible.
The LCS is therefore not merely a control inventory, but the structural mechanism by which the SCRMS converts:
- Risk appetite into operational reality; and
- Operational activity into defensible evidence.
7.3 Minimum Compliance Requirements (MCR)
Compliance-related controls are viewed as “must have” requirements that are non-discretionary (e.g., not optional). These requirements are directly sourced from an entity’s applicable laws, regulations and other obligations (e.g., contracts).
The process of clearly identifying non-discretionary controls generally involves interviewing multiple stakeholders to gain appropriate situational awareness of all pertinent compliance obligations. Stakeholders who can provide valuable insights are:
- Process owners;
- Procurement / Contracts Management;
- Project Management Office (PMO);
- Data Privacy;
- Enterprise Risk Management (ERM);
- Legal;
- Physical Security; and
- Human Resources.
Statutory Obligations
Statutory obligations are required by law and refer to current laws that were passed by a state or federal government. From a security, compliance and resilience perspective, statutory compliance requirements include state, Federal and international laws. From a security, compliance and resilience perspective, statutory compliance examples include, but are not limited to:
- Fair and Accurate Credit Transactions Act (FACTA);
- Family Education Rights and Privacy Act (FERPA);
- Federal Information Security Management Act (FISMA);
- Federal Trade Commission (FTC) Act;
- Gramm-Leach-Bliley Act (GLBA);
- Health Insurance Portability and Accountability Act (HIPAA);
- Sarbanes-Oxley Act (SOX);
- California: SB 1386 / CCPA / CPRA;
- Massachusetts: 201 CMR 17.00;
- Oregon: ORS 646A.622;
- Canada: Personal Information Protection and Electronic Documents Act (PIPEDA); and
- UK: Data Protection Act (DPA).
Regulatory Obligations
Regulatory obligations are required by law, but are different from statutory requirements in that these requirements refer to rules issued by a regulating body that is appointed by a state or federal government. These are legal requirements through proxy, where the regulating body is the source of the requirement. It is important to keep in mind that regulatory requirements tend to change more often than statutory requirements. From a security, compliance and resilience perspective, regulatory compliance examples include, but are not limited to:
- Defense Federal Acquisition Regulation Supplement (DFARS);
- Federal Acquisition Regulation (FAR);
- Federal Risk and Authorization Management Program (FedRAMP);
- National Industrial Security Program Operating Manual (NISPOM);
- Financial Industry Regulatory Authority (FINRA);
- New York Department of Financial Services (NY DFS) 23 NYCRR 500; and
- European Union General Data Protection Regulation (EU GDPR).
Contractual Obligations
Contractual obligations are required by legal contract between private parties. This may be as simple as a cybersecurity or data privacy addendum in a vendor contract that calls out unique requirements. It also includes broader requirements from an industry association that membership brings certain obligations. From a cybersecurity and privacy perspective, common contractual compliance requirements include, but are not limited to:
- Payment Card Industry Data Security Standard (PCI DSS);
- ISO 27001 certification;
- Service Entity Control (SOC) audits; and
- Contractual requirement to adhere to a specific set of requirements, such as:
- NIST Cybersecurity Framework;
- Center for Internet Security Critical Security Controls (CIS CSC); and
- Cloud Security Alliance Cloud Controls Matrix (CSA CCM).
7.4 Discretionary Security Requirements (DSR)
Cybersecurity and data protection controls that are not required by a law, regulation or contractual obligation are “nice to have” controls that are discretionary for an entity to implement. Any aspect of non-compliance with a discretionary control would be isolated within the realm of the stakeholder making the requirement, since the requirement is internal to the entity. The source of these discretionary requirements may be from:
- Board of Director (BoD) guidance;
- Steering Committee recommendations;
- Internal Audit findings;
- Prior incidents and/or events;
- Third-party audit/assessment recommendations; and/or
- Internal staff preferences.
The importance of these discretionary controls is that those are often entity-specific considerations to mitigate risk that is specific to an entity’s business practices.
Discretionary Secure, Compliant & Resilient Considerations
A common frustration amongst cybersecurity practitioners is about the gaps that exist in many “best practice” cybersecurity frameworks that are used by entities to demonstrate a level of assurance (e.g., ISO 27001 certification, SOC 2 audit, CMMC certification, etc.). The remedy to address perceived gaps is through discretionary security, compliance and resilience controls that are not directly mandated by a compliance obligation. Examples of discretionary controls, include but are not limited to:
- Data Loss Prevention (DLP);
- Network Access Control (NAC);
- File Integrity Monitoring (FIM);
- 24/7 Security Operations Center (SOC);
- Artificial Intelligence (AI) governance controls;
- Sandboxing / detonation chambers;
- Segmented development / test / production environments;
- Cloud infrastructure-specific controls; and
- Embedded technology-specific controls.
Discretionary Resilience Considerations
NIST defines resilience as, “The ability to prepare for and adapt to changing conditions and withstand and recover from disruption. Resilience includes the ability to withstand and recover from deliberate attacks, accidents, or naturally occurring threats or incidents.” From a discretionary control perspective, this may require the addition of technologies and processes to help ensure the continuity of business operations, such as:
- Continuity of Operations Plan (COOP);
- Business Continuity / Disaster Recovery (BC/DR) Plan;
- Failover / redundancy capabilities;
- Business continuity test exercises;
- Offsite, online backup storage;
- Offsite, offline backup storage; and
- Transactional-level backups.
Due Diligence vs Due Care As Foundational Constructs of the SCRMS
The SCRMS defines what it means to be secure, compliant and resilient in a holistic, framework-agnostic manner to provide a structure that can help an entity demonstrate both:
- Due diligence in building secure, compliant and resilient capabilities; and
- Due care in governing and evolving them over time.
By explicitly integrating due diligence and due care, the SCRMS enables an entity to demonstrate that:
- Risks were identified and addressed in a structured manner;
- Capabilities were implemented based on known requirements, risks and threats;
- Deficiencies were tracked and managed based on risk-based prioritization;
- Oversight occurred at appropriate governance levels; and
- Decisions were documented and revisited as conditions evolved.
This approach aligns with expectations commonly applied when evaluating the reasonableness of security, compliance and resilience practices.
Due Diligence Considerations
Due diligence answers the question: “Has the entity taken reasonable steps to build and operate secure, compliant and resilient capabilities?”
Note: Due diligence refers to the reasonable design, implementation and operation of security, compliance and resilience capabilities based on known requirements, risks and business context.
Due diligence is about building capability in a way that is economically justified and risk-aligned, not just technically complete. Within the SCRMS, due diligence includes:
- Establishing governance structures and authority;
- Defining the entity’s security, compliance and resilience controls, based on:
- Applicable statutory, regulatory and contractual obligations; and
- Risk-based requirements and industry expectations that augment compliance obligations;
- Implementing security, compliance and resilience capabilities in a structured, prioritized manner; and
- Producing objective evidence that controls exist and operate as intended.
Due Care Considerations
Due care answers the question: “Is leadership actively governing and adapting security, compliance and resilience capabilities in response to changing risks and conditions?”
Note: Due care refers to the ongoing oversight, validation and evolution of security, compliance and resilience capabilities after those capabilities are implemented and operational.
Due care is what protects directors and officers by demonstrating informed oversight and documented risk decisions. Within the SCRMS, due care includes:
- Executive-level oversight and accountability;
- Situational awareness of risk and threat exposure;
- Validation of control effectiveness;
- Risk acceptance and prioritization tied into Enterprise Risk Management (ERM); and
- A commitment to improve capabilities as conditions change.
Integrating Secure, Compliant & Resilient Into Business Planning Activities
The Secure, Compliant & Resilient Management System (SCRMS) is designed to integrate with an entity’s broader business planning activities, so that by design the capabilities exist to be secure, compliant and resilient, while meeting the business and technical requirements. This “security, compliance and resilience ecosystem” mindset is meant to exist beyond just typical security, compliance and resilience functions.
9.1 Trusted Advisor Guardrail
The cybersecurity industry is renowned for marketing professional services as a “trusted advisor” to an entity’s executive leadership. Essentially, this is the process of telling an entity’s leaders what steps to take next, as part of a broader journey that never ends.
The SCRMS provides a means to minimize Fear, Uncertainty and Doubt (FUD) by focusing on capabilities that reasonably need to exist to be secure, compliant and resilient. This is where the SCRMS can act as a “guardrail” to ensure advice from internal and third-parties enables secure, compliant and resilient practices.
Minimizing FUD can be achieved by focusing on these questions:
- Is this approach defensible?
- Does this approach reduce reinterpretation?
- Does this approach preserve meaning over time?
- Does this approach make maturity easier to explain?
- Does this approach help scale without additional headcount?
9.2 Prioritized Roadmap Concept
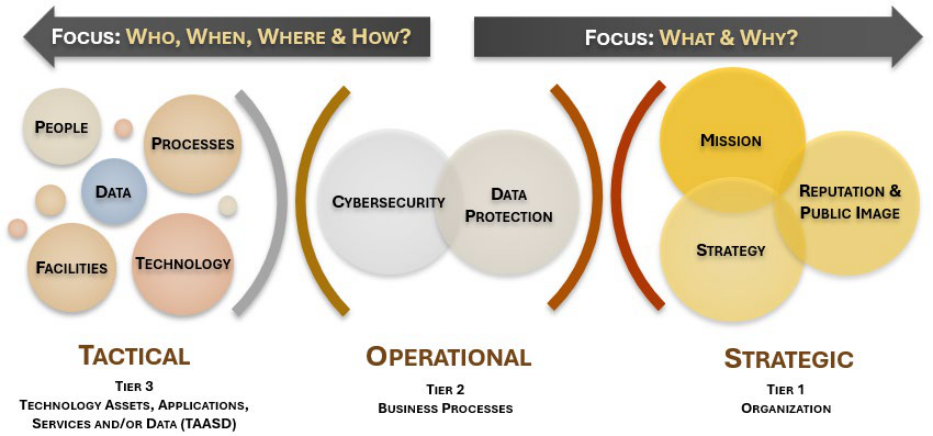
Practically, the SCRMS should be leveraged to create a prioritized roadmap that is based on a hierarchical, risk-based approach to successfully accomplishing the entity’s stated goals. From a top-down perspective, the SCRMS can assist decision makers understand the variables that make up the “Who? What? When? Where? How? and Why?” questions that arise in the process of designing, implementing and maintaining secure, compliant and resilient capabilities.
Strategic Objectives
Tier 1 provides strategic management direction using entity-level mission/business goals, policies, governance structures and entity-wide resource allocation. Tier 1 activities help to ensure that security, compliance and resilience strategies are cost-effective, efficient and consistent with the broader strategic goals and objectives of the entity.
Operational Objectives
Tier 2 addresses security, compliance and resiliency from a mission/business process perspective and is informed by the context established at Tier 1. In this tier, program requirements are defined and managed, including cost, schedule, performance and a variety of critical nonfunctional requirements. These nonfunctional requirements include concepts such as reliability, dependability, safety, security and quality. Many threats to and through the supply chain are addressed at this level in the management of trust relationships with system integrators, suppliers and external service providers of technology-related products and services.
Tactical Objectives
Tier 3 is where security, compliance and resiliency activities are integrated into the entity’s Technology Assets, Applications, Services and/or Data (TAASD), prioritized by the context established at Tier 2.
9.3 SCRMS Governance Considerations: Potential Gaps & Exposures
Entities are expected to tailor the implementation of the SCRMS for their specific needs, based on applicable People, Processes, Technology, Data and/or Facilities (PPTDF).
The following topics address areas of potential gaps that entities must avoid assumptions on. This requires due diligence and due care actions to avoid, or minimize, potential gaps and/or exposures.
Operational Control Assumptions
A potential capabilities gap exists for operational control assumptions. This issue is based on how SCRMS assumes governance intent translates into execution without explicitly enforcing operational control mechanisms.
Problematic issues associated with potential capabilities gap include, but are not limited to:
- Compliance without operational stability; and
- Periods of time where security and resilience capabilities diminish between audits.
Due Care Verifiability
A potential capabilities gap exists for due care verifiability. This issue is based on due care activities that are conceptually defined but lack defensible, evidence-based proof requirements.
Problematic issues associated with potential capabilities gap include, but are not limited to:
- “Security theater” where due care activities are merely theoretical through documentation; and
- Available defensible evidence is insufficient to demonstrate reasonable due care practices.
Control Drift & Capability Decay
A potential capabilities gap exists for control drift and capability decay. This issue is based on scenarios when there are no explicit mechanisms to detect or prevent control erosion caused by routine change.
Problematic issues associated with potential capabilities gap include, but are not limited to:
- Point-in-time snapshot compliance instead of durable security posture; and
- Governance practices lose focus on security, compliance and resilience prioritization.
AI Governance Depth
A potential capabilities gap exists for the depth of AI governance. This issue is based on AI being treated as a risk category, not as a governed lifecycle system.
Problematic issues associated with potential capabilities gap include, but are not limited to:
- AI governance is run as a siloed activity that negatively affects situational awareness across the entity; and
- Cross-functional expertise does not exist to properly perform AI governance activities.
Supply Chain Threats
A potential capabilities gap exists for Third-Party Risk Management (TPRM) governance. This issue is based on TPRM treated as an extension, not a co-equal attack surface.
Problematic issues associated with potential capabilities gap include, but are not limited to:
- “Check box” approach to security, compliance and resilience reviews for third-parties, where pertinent risks and threats are ignored for misguided efficiency purposes; and
- Indirect compromise despite evidence of conformity.
Decision Making Authority
A potential capabilities gap exists for authority to make decisions. This issue is based on roles being defined, but decision authority and escalation paths are unclear.
Problematic issues associated with potential capabilities gap include, but are not limited to:
- A lack of designated alternative decision-makers; and
- Governance paralysis during incidents.
Resilience Stress Testing
A potential capabilities gap exists for resilience stress testing. This issue is based on scenarios where resilience planning lacks compounded, adversarial stress testing requirements.
Problematic issues associated with potential capabilities gap include, but are not limited to:
- Misunderstanding of service dependencies provides gaps in resilience planning activities; and
- False confidence in resilience capabilities.
Linear Maturity Assumptions
A potential capabilities gap exists for maturity assumptions. This issue is based on maturity models that assume rational progression.
Problematic issues associated with potential capabilities gaps include, but are not limited to:
- Incorrect assumption that all controls are weighted equally for maturity planning needs (e.g., material controls); and
- Misleading maturity scores.
Metrics Without Guardrails
A potential capabilities gap exists for metrics and analytics governance. This issue is based on scenarios where Key Performance Indicators (KPIs) and Key Risk Indicators (KRIs) are encouraged without defining metrics that may be misleading and lead to false assumptions.
Problematic issues associated with potential capabilities gap include, but are not limited to:
- Developing metrics that are not “SMART”:
- Specific;
- Measurable;
- Achievable;
- Relevant; and
- Time-bound; and
- Executive dashboards may mask systemic risk.
Economic Decision Framing
A potential capabilities gap exists for framing decisions that ignore economic realities for the entity. This issue is based on the absence of an explicit economic model for security tradeoffs.
Problematic issues associated with potential capabilities gap include, but are not limited to:
- Potential instances of negligent behaviors, based on low maturity capabilities; and
- Underfunded or strategically rejected programs.
9.4 Surviving Real-World Challenges
From a governance perspective, the following questions should be addressed to determine if an entity’s SCRMS is capable of surviving real-world challenges:
Nested Approach To Risk Management Practices
The alternative to risk management is crisis management. Risk management is a multi-layered capability. From a security, compliance and resilience perspective, there should be at least three (3) layers of risk management focus:
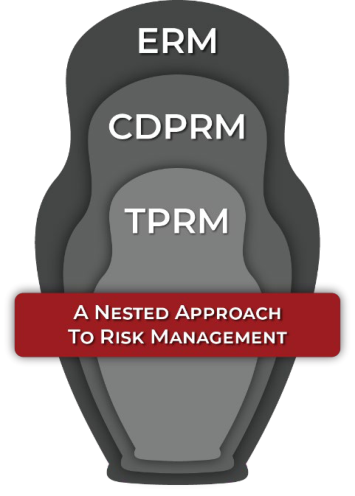
- Enterprise Risk Management (ERM);
- Secure, Compliant & Resilient Risk Management (CDPRM); and
- Third-Party Risk Management (TPRM) (inclusive of Supply Chain Risk Management (SCRM) activities).
Similar in concept to traditional “Russian nesting dolls,” from a risk management hierarchy perspective:
- TPRM should be subordinate to CDPRM; and
- CDPRM should be subordinate to ERM.
10.1 Risk Profile
Per NIST, a risk profile is a “prioritized inventory of the most significant risks identified and assessed through the risk assessment process versus a complete inventory of risks.” The ability to prioritize and assess risks requires the entity to create entity-specific definitions and associated criteria for:
- Risk appetite;
- Risk tolerance; and
- Risk threshold.
The reasoning for this is simple, the entity needs to speak the same language for risk management operations, where everyone understands the thresholds associated with low, moderate, high, etc. risks. Only through this level of standardization will an entity be able to efficiently and effectively manage risk associated with Technology Assets, Applications, Services and/or Data (TAASD).
Risk Appetite
A risk appetite is a broad “risk management concept” used to inform employees about what is and is not acceptable, regarding risk management from an entity's executive leadership team. A risk appetite does not contain granular risk management criteria and is primarily a “management statement” that is subjective. Similar in concept to how a policy is a "high-level statement of management intent," an entity's defined risk appetite is a high-level statement of how all risk, or certain types of risk, are willing to be accepted.
Risk Tolerance
Risk tolerance is based on objective criteria, unlike the subjective, conceptual nature of a risk appetite. Defining objective criteria is a necessary step to categorize risk on a graduated scale. Establishing objective criteria to quantify the impact of risk enables risk assessments to leverage those same criteria and assist decision-makers in their risk management decisions (e.g., accept, mitigate, transfer or avoid).
Risk Thresholds
Risk thresholds are directly tied to risk tolerance and utilize entity-specific criteria (e.g., acceptable and unacceptable parameters). These risk thresholds exist between the different levels of risk tolerance (e.g., Low, Moderate and High Risk). By establishing these risk thresholds, it provides a means of comparing relative risk to an entity. Risk thresholds are criteria that are unique to an entity such as entity-specific activities / scenarios that could:
- Damage the entity’s reputation;
- Negatively affect short-term and long-term profitability; and/or
- Impede business operations.
Risk thresholds are entirely unique to each entity, based on several factors that include:
- Financial stability;
- Management preferences;
- Compliance obligations (e.g., statutory, regulatory and/or contractual); and
- Insurance coverage limits.
10.2 Materiality
Defining materiality is an executive leadership determination, not a cybersecurity determination. This is entity-specific and is primarily based on a clearly-defined financial threshold.
Once the materiality threshold is clearly defined, it then requires a look at an entity’s risk and threat management practices to identify those specific risks and threats that could lead to a material incident. Ideally, this means reviewing established risk and threat catalogs to identify known risks and threats that have material implications.
The SCF Council defines the materiality threshold for an entity’s security, compliance and resilience program as, “A deficiency, or a combination of deficiencies, in an entity’s cybersecurity and/or data protection controls (across its supply chain) where it is probable that reasonable threats will not be prevented or detected in a timely manner that directly, or indirectly, affects assurance that the entity can adhere to its stated risk tolerance.”
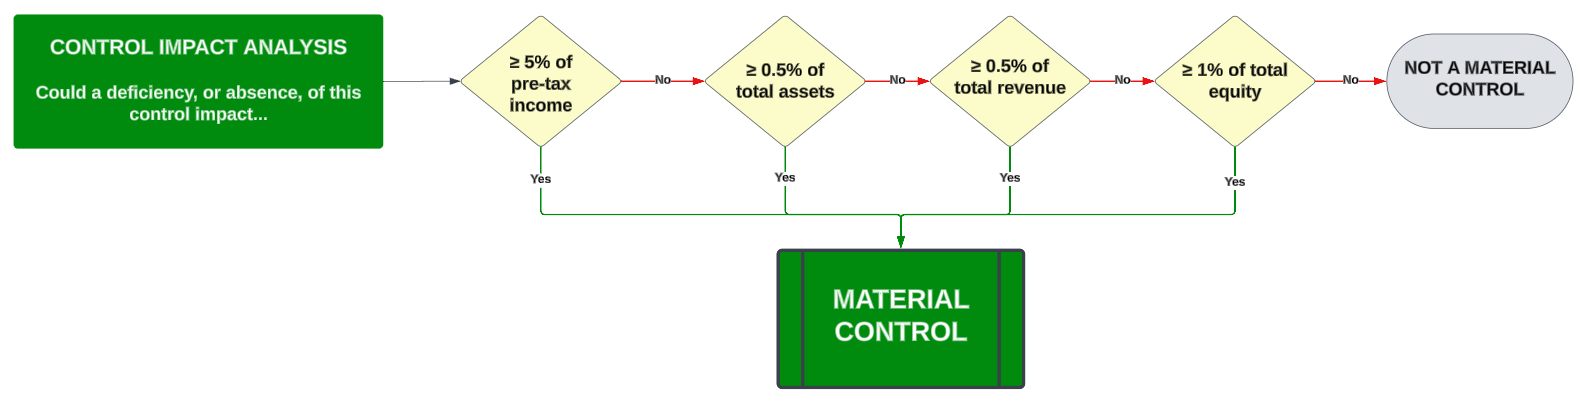
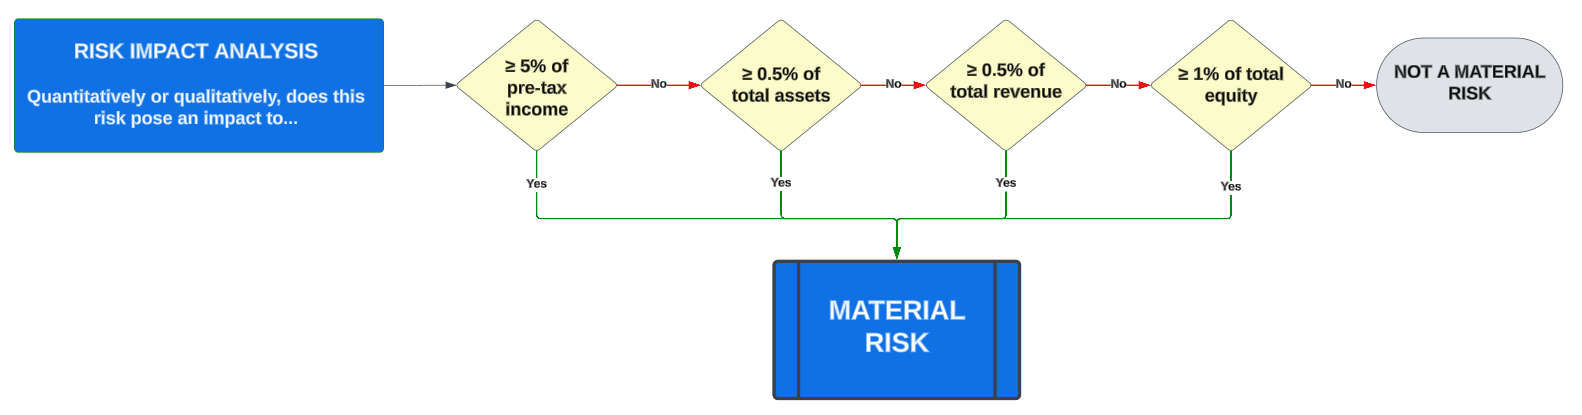
Generally, account criteria from pre-tax income, total assets, total revenue and total equity to provide options for both "single criteria determinations" and "averaged determinations" to establish objective thresholds. From a financial benchmark perspective, for something to be considered material, the control deficiency, risk, threat or incident (singular or a combination) generally must meet one, or more, of the following criteria where the potential financial impact is measured as:
- ≥ 5% of Earnings Before Tax (EBT) (e.g., total revenue after subtracting expenses, except taxes);
- ≥ 0.5% of total assets (e.g., net book value of tangible and intangible assets);
- ≥ 1% of total equity (e.g., residual value of the entity after subtracting liabilities); and/or
- ≥ 0.5% of total revenue (e.g., gross sales plus other income).
Material Control Identification
When a deficiency, or absence, of a specific control poses a material impact, that control is designated as a material control. A material control is such a fundamental cybersecurity and/or data protection control that:
- It is not capable of having compensating controls; and
- Its absence, or failure, exposes an entity to such a degree that it could have a material impact.
Material Risk Identification
When an identified risk that poses a material impact, that is a material risk. A material risk:
- Is a quantitative or qualitative scenario where the exposure to danger, harm or loss has a material impact (e.g., significant financial impact, potential class action lawsuit, death related to product usage, etc.); and
- Should be identified and documented in an entity's "risk catalog" that chronicles the entity's relevant and plausible risks.
Material Threat Identification
When an identified threat poses a material impact, that is a material threat. A material threat:
- Is a vector that causes damage or danger that has a material impact (e.g., poorly governed Artificial Intelligence (AI) initiatives, nation state hacking operations, dysfunctional internal management practices, etc.); and
- Should be identified and documented in an entity's "threat catalog" that chronicles the entity's relevant and plausible threats.
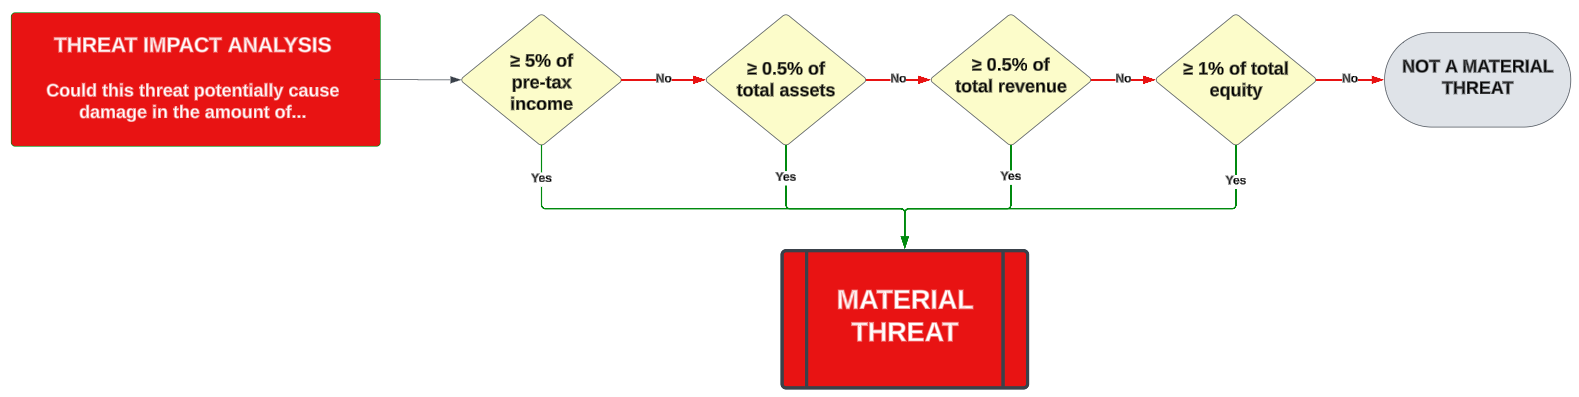
Material Incident Identification
When an incident poses a material impact, that is a material incident. A material incident is an occurrence that does or has the potential to:
- Jeopardize the Confidentiality, Integrity, Availability and/or Safety (CIAS) of a system, application, service or the data that it processes, stores and/or transmits with a material impact on the entity; and/or
- Constitute a violation, or imminent threat of violation, of an entity's policies, standards, procedures or acceptable use practices that has a material impact (e.g., malware on sensitive and/or regulated systems, emergent AI actions, illegal conduct, business interruption, etc.).
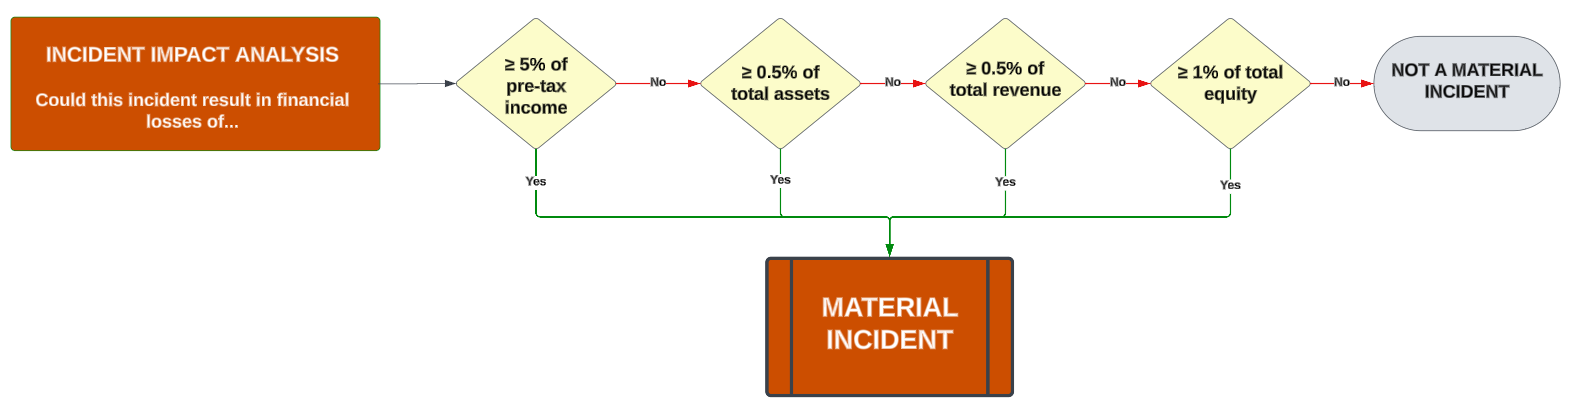
10.3 Integration of Risk Management & Business Planning
These key concepts of how risk appetite, risk tolerance and risk thresholds interact with strategic, operational and tactical actions and decisions can be visualized in the following graphic:
- At the strategic layer, where corporate-level actions and decisions are made, the entity’s risk appetite is defined. The scope of the risk appetite can be entity-wide or compartmentalized to provide enhanced granularity.
- At the operational level, where Line of Business (LOB)-level actions and decisions are made, the entity’s risk tolerance is put into practice. The entity’s risk tolerance is defined by its established risk appetite.
- At the tactical level, where department / team-level actions and decisions are made, the entity’s risk thresholds are used to provide criteria to assess operational risk. That operational risk must adhere to the entity’s risk tolerance and therefore, its risk appetite.
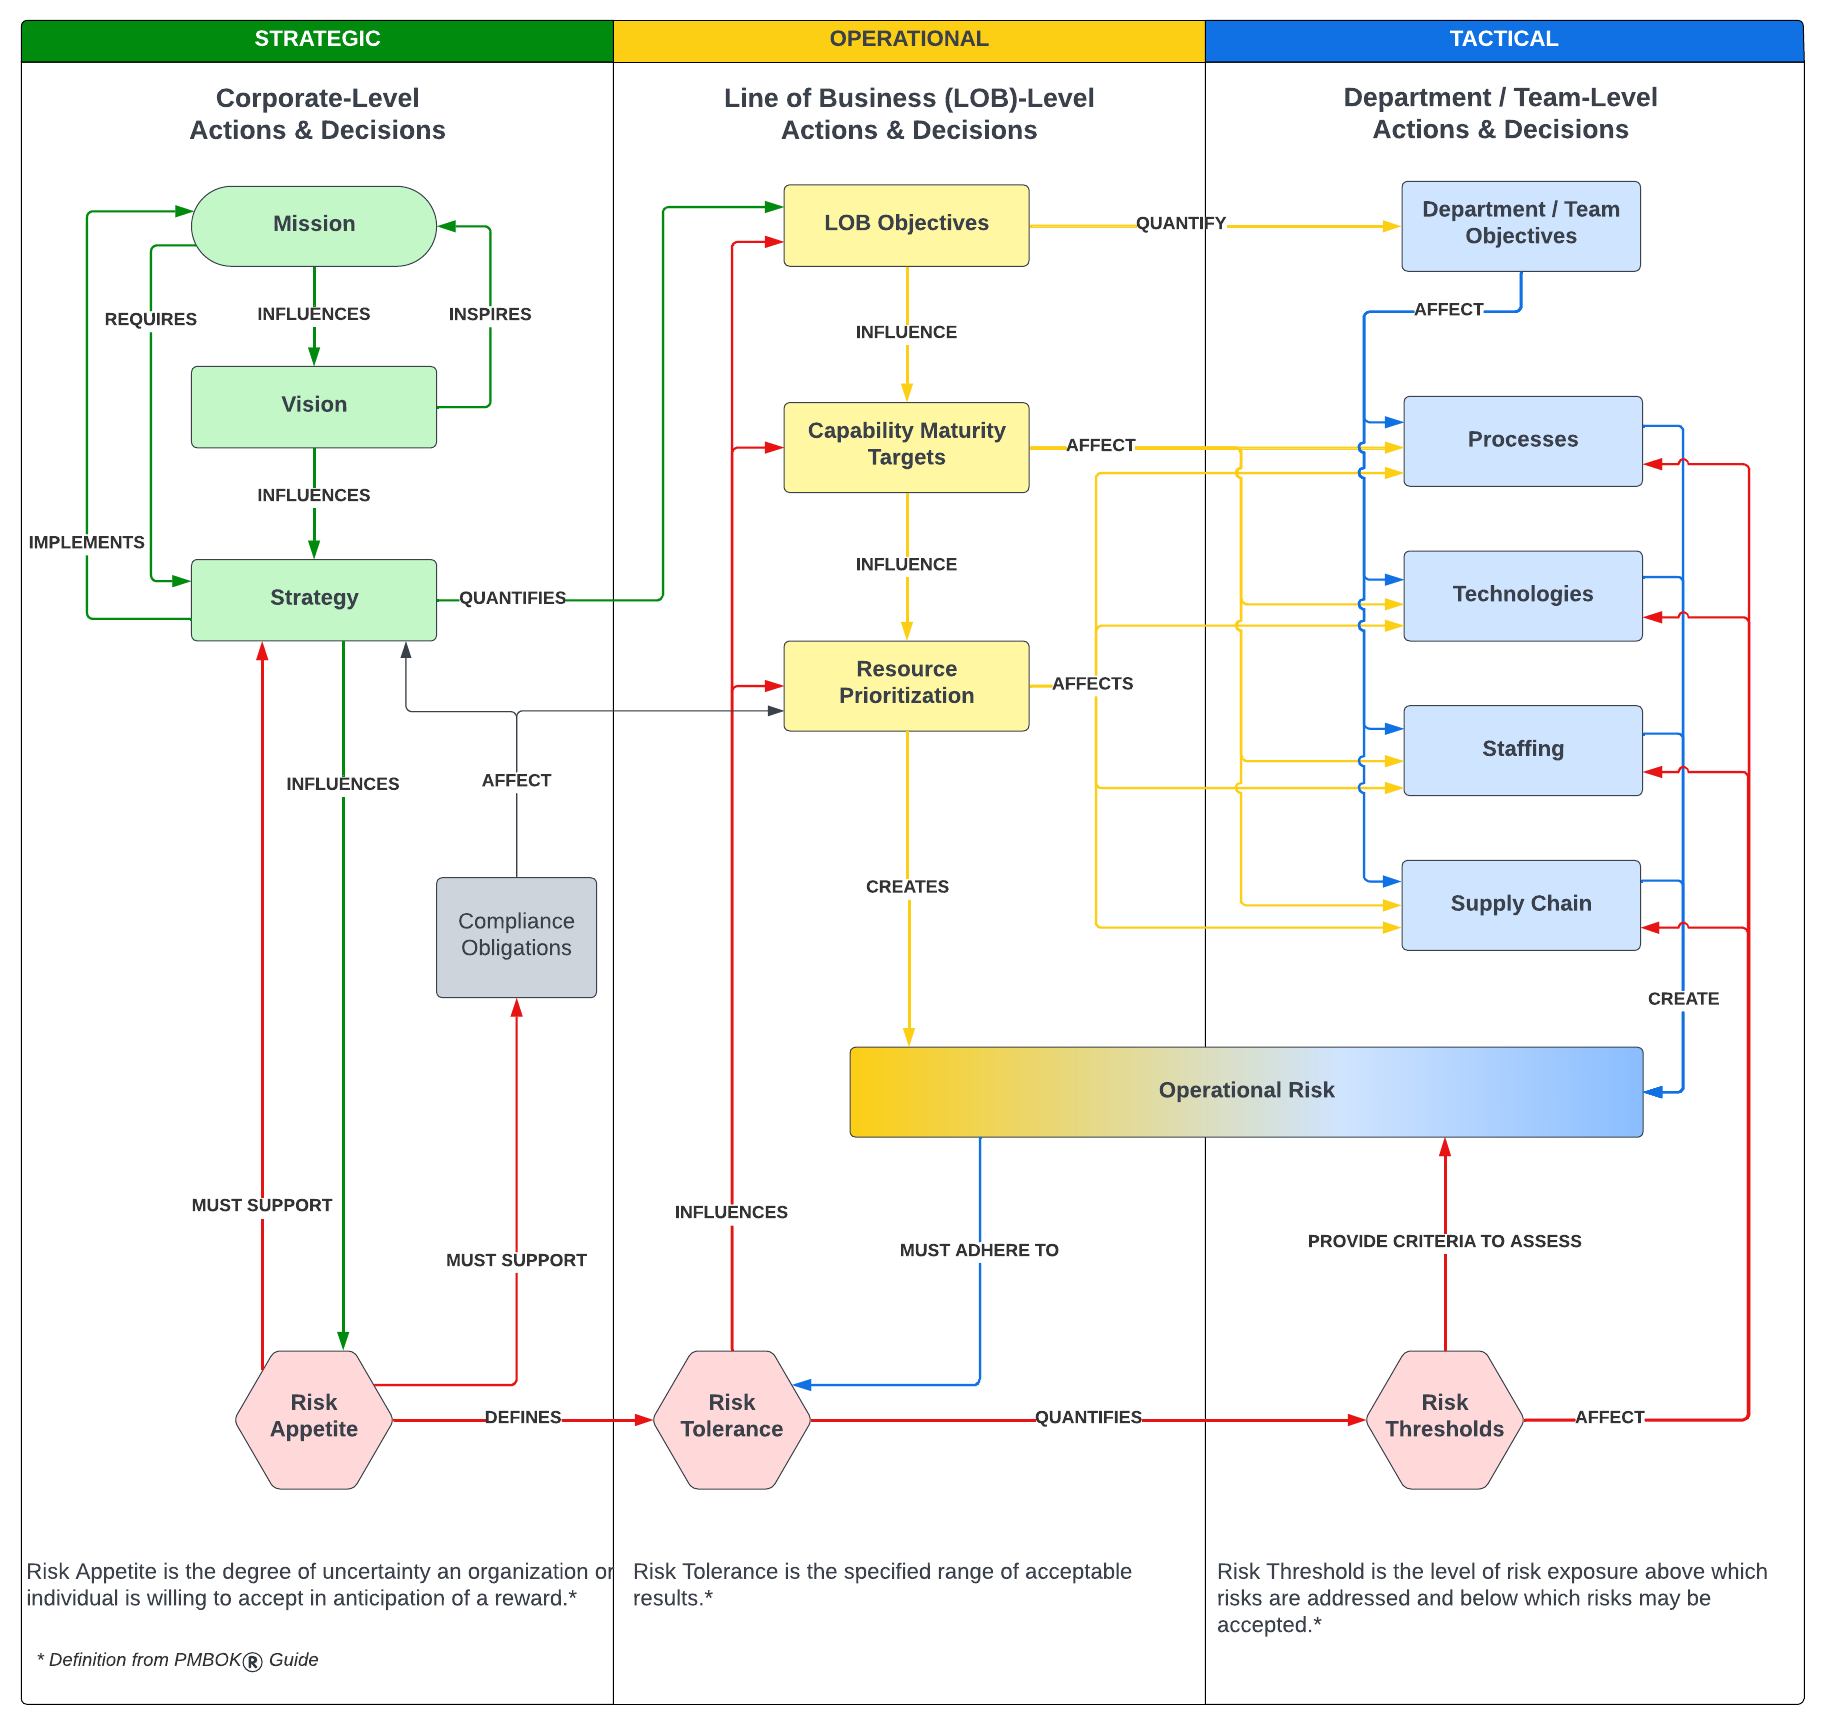
10.4 Enterprise Risk Management (ERM)
ERM focuses on risk management at the entity level. ERM is expected to clearly define the criteria that constitute what is allowed and what is prohibited from a risk management perspective:
- Acceptable Risk. The criteria fall within a range of acceptable parameters; and
- Unacceptable Risk. The criteria fall outside a range of acceptable parameters.
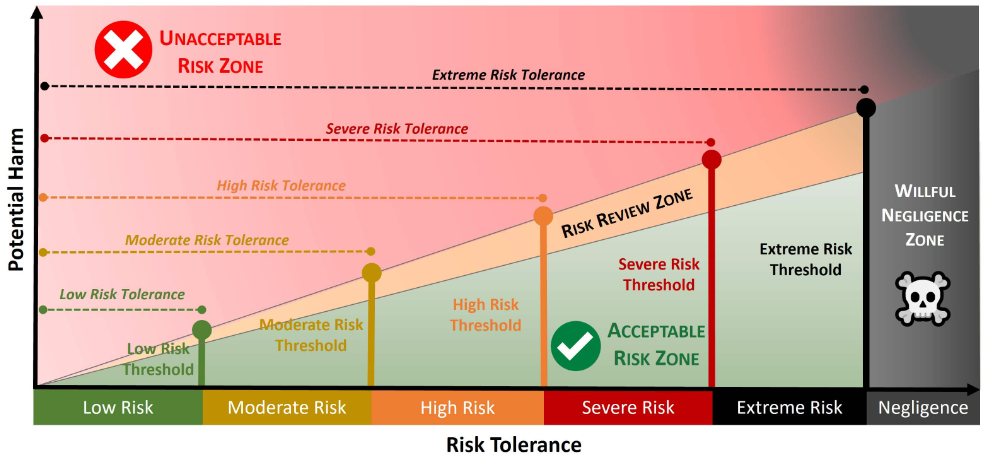
10.5 Secure, Compliant & Resilient Risk Management (CDPRM)
CDPRM focuses on the security, compliance and resilience component of risk management. CDPRM is expected to operate within the parameters established by ERM to ensure entity-wide risk management guidance is implemented.
10.6 Third-Party Risk Management (TPRM)
TPRM focuses on external risks associated with third-parties. This includes, but is not limited to:
- External Service Providers (ESP);
- Cloud Service Providers (CSP); and
- Material suppliers.
Sub-component of TPRM involve:
- Supply Chain Risk Management (SCRM);
- Cybersecurity Supply Chain Risk Management (C-SCRM).
Within the scope of the SCRMS, supply chain-related risks and threats are inclusive of third-party governance practices.
Due Diligence Activities
As described in Section 7, Control Set Determination, the Minimum Security Requirements (MSR) is a baseline determined by the entity’s Minimum Compliance Requirements (MCR) and Discretionary Security Requirements (DSR). While compliance-related activities are unique to the statutory, regulatory or contractual obligations of the entity, there are reasonable security, compliance and resilience capabilities that entities should implement, regardless of its size, industry or geography. These foundational practices are part of the SCF’s Cybersecurity Oversight, Resilience and Enablement (SCF CORE) Fundamentals baseline, designed to:
- Contain administrative, technical and physical safeguards for the protection of Technology Assets, Applications, Services and/or Data (TAASD); and
- Protect against any reasonable risks and threats.
From a due diligence perspective for the SCRMS, an entity is expected to demonstrate conformity with the following practices:
Each of the 33 domains below lists its requirement, the relevant SCF control and the evidence an entity needs to demonstrate conformity. The full guidance for every subsection is in the SCRMS PDF.
11.1 Secure, Compliant & Resilient Program (SCRP)
The entity must specify the development of its security, compliance and resilience program, including criteria to measure success, to ensure ongoing leadership engagement and risk management.
Relevant SCF Control(s): GOV-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- An entity-wide security, compliance and resilience governance program is developed.
- The security, compliance and resilience governance program addresses management commitment.
- The security, compliance and resilience governance program addresses statutory, regulatory and/or contractual compliance obligations.
Subsections in the SCRMS
- 11.1.1 Steering Committee & Program Oversight
- 11.1.2 Publishing Secure, Compliant & Resilient Documentation
- 11.1.3 Exception Management
- 11.1.4 Assigned Secure, Compliant & Resilient Responsibilities
- 11.1.5 Stakeholder Accountability Structure
- 11.1.6 Establish Context For Business Operations
- 11.1.7 Operationalizing Secure, Compliant & Resilient Practices
- 11.1.8 Select Controls
- 11.1.9 Implement Controls
- 11.1.10 Assess Controls
- 11.1.11 Authorize Technology Assets, Applications and/or Services (TAAS)
- 11.1.12 Materiality Determinations
- 11.1.13 Material Risks
- 11.1.14 Material Threats
11.2 Artificial Intelligence & Autonomous Technologies
The entity must ensure Artificial Intelligence (AI) and autonomous technologies are designed to be reliable, safe, fair, secure, resilient, transparent, explainable and data privacy-enhanced. In addition, AI-related risks are governed according to minimize emergent properties or unintended consequences.
Relevant SCF Control(s): AAT-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- AAT-specific policies, standards and procedures are:
- Developed and documented; and
- Implemented effectively.
- AAT operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support AAT operations.
- Responsibility and authority for the performance of AAT-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.2.1 Artificial Intelligence (AI) & Autonomous Technologies Governance
- 11.2.2 Trustworthy AI & Autonomous Technologies
- 11.2.3 Situational Awareness of AI & Autonomous Technologies
- 11.2.4 Adequate Protections For AI & Autonomous Technologies
- 11.2.5 Artificial Intelligence Test, Evaluation, Validation & Verification (AI TEVV)
11.3 Asset Management
The entity must ensure technology assets are properly managed throughout the lifecycle of the asset, from procurement through disposal, ensuring only authorized devices are allowed to access the entity's network and to protect the entity's data that is stored, processed or transmitted on its assets.
Relevant SCF Control(s): AST-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- An authoritative source and repository are established to provide a trusted source and accountability for approved and implemented systems and system components.
- The frequency at which to review / update the system and system component inventory is defined.
- An inventory of systems and system components that is at the level of granularity deemed necessary for tracking and reporting is developed and documented.
- IT Asset Management (ITAM) operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support ITAM operations.
- Responsibility and authority for the performance of ITAM-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.3.1 Asset-Service Dependencies
- 11.3.2 Stakeholder Identification & Involvement
- 11.3.3 Asset Inventories
- 11.3.4 Data Action Mapping
- 11.3.5 Network Diagrams & Data Flow Diagrams (DFDs)
- 11.3.6 Secure Disposal, Destruction or Re-Use of Equipment
- 11.3.7 Bring Your Own Device (BYOD) Usage
11.4 Business Continuity & Disaster Recovery
The entity must establish processes that will help the entity recover from adverse situations with minimal impact to operations, as well as provide the capability for e-discovery.
Relevant SCF Control(s): BCD-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Cybersecurity issues are addressed in the development of a critical infrastructure and key resources protection plan.
- Data privacy issues are addressed in the development of a critical infrastructure and key resources protection plan.
- Business Continuity & Disaster Recovery (BC/DR) operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support Business Continuity & Disaster Recovery (BC/DR) operations.
- Responsibility and authority for the performance of Business Continuity & Disaster Recovery (BC/DR)-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.4.1 Recovery Time / Point Objectives (RTO / RPO)
- 11.4.2 Recovery Operations Criteria
- 11.4.3 Identify Critical Assets
- 11.4.4 Resume All Missions & Business Functions
- 11.4.5 Continue Essential Mission & Business Functions
- 11.4.6 Resume Essential Missions & Business Functions
- 11.4.7 Data Backups
- 11.4.8 Technology Assets, Applications and/or Services (TAAS) Recovery & Reconstitution
11.5 Capacity & Performance Planning
The entity must prevent avoidable business interruptions caused by capacity and performance limitations by proactively planning for growth and forecasting, as well as requiring both technology and business leadership to maintain situational awareness of current and future performance.
Relevant SCF Control(s): CAP-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Resources to be allocated to protect the availability of resources are defined.
- Capacity & performance planning operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support capacity & performance planning operations.
- Responsibility and authority for the performance of capacity & performance planning-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.5.1 Capacity & Performance Management
- 11.5.2 Capacity Planning
- 11.5.3 Elastic Expansion
11.6 Change Management
The entity must ensure both technology and business leadership proactively manage change, including the assessment, authorization and monitoring of technical changes across the enterprise so as to not impact production systems uptime and allow easier troubleshooting of issues.
Relevant SCF Control(s): CHG-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Configuration change control activities are coordinated and overseen by entity-defined configuration change control element.
- Configuration change decisions associated with the system are documented.
- Approved configuration-controlled changes to the system are implemented.
- Change management operations are conducted according to documented policies, standards, procedures and/or other directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support change management operations.
- Responsibility and authority for the performance of change management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.6.1 Configuration Change Control
- 11.6.2 Prohibition Of Changes
- 11.6.3 Security Impact Analysis for Changes
11.7 Cloud Security
The entity must govern the use of private and public cloud environments (e.g., IaaS, PaaS and SaaS) to holistically manage risks associated with third-party involvement and architectural decisions, as well as to ensure the portability of data to change cloud providers, if needed.
Relevant SCF Control(s): CLD-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The entity facilitates the implementation of cloud management controls to ensure cloud instances are securely configured and maintained.
- Cloud management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support cloud management operations.
- Responsibility and authority for the performance of cloud management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.7.1 Cloud Services
- 11.7.2 Cloud Security Architecture
- 11.7.3 Geolocation Requirements for Processing, Storage and Service Locations
- 11.7.4 Sensitive Data In Public Cloud Providers
11.8 Compliance
The entity must ensure controls are in place to ensure adherence to applicable statutory, regulatory and contractual compliance obligations, as well as internal company standards.
Relevant SCF Control(s): CPL-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The entity analyzes its business practices to determine applicable statutory, regulatory and/or contractual obligations.
- Compliance management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support compliance management operations.
- Responsibility and authority for the performance of compliance management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.8.1 Statutory, Regulatory & Contractual Compliance
- 11.8.2 Compliance Scope
11.9 Configuration Management
The entity must establish and maintain the integrity of systems. Without properly documented and implemented configuration management controls, security features can be inadvertently or deliberately omitted or rendered inoperable, allowing processing irregularities to occur or the execution of malicious code.
Relevant SCF Control(s): CFG-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The scope for the configuration management plan is entity-wide.
- The types of changes to the system that are configuration-controlled are defined.
- A configuration management plan for systems, applications and services is:
- Developed;
- Documented; and
- Implemented.
- Configuration management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support configuration management operations.
- Responsibility and authority for the performance of configuration management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.9.1 Secure Baseline Configurations
- 11.9.2 Approved Configuration Deviations
- 11.9.3 Least Functionality
11.10 Continuous Monitoring
The entity must establish and maintain ongoing situational awareness across the enterprise through the centralized collection and review of security-related event logs. Without comprehensive visibility into infrastructure, operating system, database, application and other logs, the entity will have “blind spots” in its situational awareness that could lead to system compromise, data exfiltration, or unavailability of needed computing resources.
Relevant SCF Control(s): MON-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The continuous monitoring program is entity-wide.
- Monitoring objectives to detect attacks and indicators of potential attacks on the system are defined.
- Techniques and methods used to identify unauthorized use of the system are defined.
- Event monitoring operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support event monitoring operations.
- Responsibility and authority for the performance of event monitoring-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.10.1 Automated Tools for Real-Time Analysis
- 11.10.2 System Generated Alerts
- 11.10.3 Security Event Monitoring
- 11.10.4 Content of Event Logs
- 11.10.5 Monitoring for Indicators of Compromise (IOC)
- 11.10.6 Anomalous Behavior
11.11 Cryptographic Protections
The entity must ensure the confidentiality and integrity of its data through implementing appropriate cryptographic technologies to protect systems, applications, services and data.
Relevant SCF Control(s): CRY-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Cryptographic uses are:
- Identified; and
- Defined.
- Cryptographic mechanisms intended to prevent unauthorized disclosure of sensitive and/or regulated data are identified.
- Entity-defined types of cryptography are implemented to protect the confidentiality of sensitive and/or regulated data.
- Cryptographic protections management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support cryptographic protections management operations.
- Responsibility and authority for the performance of cryptographic protections management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.11.1 Transmission Confidentiality
- 11.11.2 Encrypting Data At Rest
- 11.11.3 Public Key Infrastructure (PKI)
- 11.11.4 Cryptographic Key Management
11.12 Data Classification & Handling
The entity must ensure that technology assets, both electronic and physical, are properly classified and measures implemented to protect the entity's data from unauthorized disclosure, or modification, regardless if it is being transmitted or stored. Applicable statutory, regulatory and contractual compliance requirements dictate the minimum safeguards that must be in place to protect the confidentiality, integrity and availability of data.
Relevant SCF Control(s): DCH-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Paper media containing sensitive and/or regulated data is physically controlled.
- Digital media containing sensitive and/or regulated data is physically controlled.
- Data classification & handling management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support data classification & handling management operations.
- Responsibility and authority for the performance of data classification & handling management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.12.1 Sensitive and/or regulated data Protection
- 11.12.2 Defining Access Authorizations for Sensitive and/or regulated data
- 11.12.3 Data & Asset Classification
- 11.12.4 Sensitive Data Inventories
- 11.12.5 Use of External Technology Assets, Applications and/or Services (TAAS)
- 11.12.6 Protecting Sensitive / Regulated Data on External Technology Assets, Applications and/or Services (TAAS)
- 11.12.7 Media & Data Retention
- 11.12.8 Geographic Location of Data
- 11.12.9 Information Disposal
- 11.12.10 Information Location
- 11.12.11 Transfer of Sensitive and/or Regulated Data
- 11.12.12 Ad-Hoc Transfers
11.13 Embedded Technology
The entity must specify the development, proactive management and ongoing review of security embedded technologies, including hardening of the “stack” from the hardware, firmware and software to transmission and service protocols used for Internet of Things (IoT) and Operational Technology (OT) devices.
Relevant SCF Control(s): EMB-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Embedded technology controls are implemented to protect the:
- Confidentiality of IoT and/or OT technologies;
- Integrity of IoT and/or OT technologies;
- Availability of IoT and/or OT technologies; and
- Safety of IoT and/or OT technologies.
- Embedded technology management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support embedded technology management operations.
- Responsibility and authority for the performance of embedded technology management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.13.1 Prevent Alterations
- 11.13.2 Embedded Technology Maintenance
- 11.13.3 Embedded Technology Reviews
11.14 Endpoint Security
The entity must ensure that endpoint devices are appropriately protected from security threats to the device and its data. Applicable statutory, regulatory and contractual compliance requirements dictate the minimum safeguards that must be in place to protect the confidentiality, integrity, availability and safety considerations.
Relevant SCF Control(s): END-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Security configuration settings for information technology products employed in the system are established and included in the baseline configuration.
- Endpoint security management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support endpoint security management operations.
- Responsibility and authority for the performance of endpoint security management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.14.1 Endpoint Protection Measures
- 11.14.2 Malicious Code Protection (Anti-Malware)
- 11.14.3 Always On Protection
- 11.14.4 Phishing & Spam Protection
11.15 Human Resources Security
The entity must create a security, compliance and resilience-minded workforce and an environment that is conducive to innovation, considering issues such as culture, reward and collaboration.
Relevant SCF Control(s): HRS-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Personnel security procedures to facilitate the implementation of the personnel security policy and associated personnel security controls are developed and documented.
- An official to manage the personnel security policy and procedures is defined.
- Personnel management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support personnel management operations.
- Responsibility and authority for the performance of personnel management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.15.1 Onboarding, Transferring & Offboarding Personnel
- 11.15.2 Defined Roles & Responsibilities
- 11.15.3 Competency Requirements for Security-Related Positions
- 11.15.4 Personnel Screening
- 11.15.5 Roles With Special Protection Measures
- 11.15.6 Terms of Employment
- 11.15.7 Rules of Behavior
- 11.15.8 Policy Familiarization & Acknowledgement
- 11.15.9 Personnel Sanctions
- 11.15.10 Workplace Investigations
- 11.15.11 Personnel Transfer
- 11.15.12 Personnel Termination
- 11.15.13 Third-Party Personnel
- 11.15.14 Identifying Authorized Work Locations
11.16 Identification & Authentication
The entity must implement the concept of “least privilege” through limiting access to the entity's systems and data to authorized users only.
Relevant SCF Control(s): IAC-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- A capability to govern logical identification and access management controls is implemented.
- The Identity & Access Management (IAM) program is entity-wide.
- IAM operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support IAM operations.
- Responsibility and authority for the performance of IAM-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.16.1 Authenticate, Authorize and Audit (AAA)
- 11.16.2 User & Service Account Inventories
- 11.16.3 Multi-Factor Authentication (MFA)
- 11.16.4 User Provisioning & De-Provisioning
- 11.16.5 Role-Based Access Control (RBAC)
- 11.16.6 Authenticator Management
- 11.16.7 Default Authenticators
- 11.16.8 Password Managers
- 11.16.9 Account Management
- 11.16.10 System Account Reviews
- 11.16.11 Privileged Account Management (PAM)
- 11.16.12 Privileged Account Inventories
- 11.16.13 Periodic Review of Account Privileges
- 11.16.14 Access Enforcement
- 11.16.15 Least Privilege
11.17 Incident Response
The entity must establish and maintain a viable and tested capability to respond to cybersecurity or data privacy-related incidents in a timely manner, where the entity’s personnel understand how to detect and report potential incidents.
Relevant SCF Control(s): IRO-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The rigor of incident handling activities is comparable and predictable across the entity.
- The intensity of incident handling activities is comparable and predictable across the entity.
- The scope of incident handling activities is comparable and predictable across the entity.
- The results of incident handling activities are comparable and predictable across the entity.
- Incident handling activities are coordinated with contingency planning activities.
- Incident response management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support incident response management operations.
- Responsibility and authority for the performance of incident response management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.17.1 Incident Handling
- 11.17.2 Indicators of Compromise (IOC)
- 11.17.3 Incident Response Plan (IRP)
- 11.17.4 Integrated Security Incident Response Team (ISIRT)
- 11.17.5 Incident Stakeholder Reporting
- 11.17.6 Root Cause Analysis (RCA) & Lessons Learned
11.18 Information Assurance
The entity must ensure the adequacy of security, compliance and resilience controls in development, testing and production environments.
Relevant SCF Control(s): IAO-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- An Information Assurance (IA) process is implemented for conducting security, compliance and resilience testing, training and monitoring activities associated with systems, applications and services.
- The Information Assurance Program (IAP) is entity-wide.
- The authorization processes are integrated into an entity-wide Risk Management Program (RMP).
- The security, compliance and resilience security state of the entity's systems and the environments in which those systems operate are managed through authorization processes.
- Information assurance management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support information assurance management operations.
- Responsibility and authority for the performance of information assurance management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.18.1 Information Assurance Operations
- 11.18.2 Controls Assessments
- 11.18.3 Security Assessment Report (SAR)
- 11.18.4 System Security & Privacy Plan (SSPP)
- 11.18.5 Threat Analysis & Flaw Remediation During Development
- 11.18.6 Plan of Action & Milestones (POA&M)
- 11.18.7 Authorization To Operate (ATO)
11.19 Maintenance
The entity must ensure that Technology Assets, Applications and/or Services (TAAS) are properly maintained to ensure continued performance and effectiveness. Maintenance processes apply additional scrutiny to the security of end-of-life or unsupported assets.
Relevant SCF Control(s): MNT-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- A maintenance policy is developed and documented.
- The maintenance policy is disseminated to entity-defined personnel or roles.
- Maintenance procedures to facilitate the implementation of the maintenance policy and associated maintenance controls are developed and documented.
- The maintenance procedures are disseminated to entity-defined personnel or roles.
- Maintenance management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support maintenance management operations.
- Responsibility and authority for the performance of maintenance management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.19.1 Maintenance Operations
- 11.19.2 Controlled Maintenance
- 11.19.3 Remote Maintenance
11.20 Mobile Device Management
The entity must govern risks associated with mobile devices, regardless of ownership (entity-owned, employee-owned or third-party owned). Wherever possible, technologies are employed to centrally manage mobile device access and data storage practices.
Relevant SCF Control(s): MDM-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Policies and standards facilitate the implementation of mobile device management controls.
- Usage restrictions are established for mobile devices.
- Mobile Device Management (MDM) operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support MDM operations.
- Responsibility and authority for the performance of MDM-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.20.1 Full Device & Container-Based Encryption
- 11.20.2 Remote Purging
- 11.20.3 Personally-Owned Mobile Devices
- 11.20.4 Organization-Owned Mobile Devices
- 11.20.5 Restricting Access To Authorized Technology Assets, Applications and/or Services (TAAS)
11.21 Network Security
The entity must ensure sufficient security, compliance and resilience controls are architected to protect the confidentiality, integrity, availability and safety of the entity's network infrastructure, as well as to provide situational awareness of activity on the entity's networks.
Relevant SCF Control(s): NET-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- System and communications protection procedures to facilitate the implementation of the system and communications protection policy and associated system and communications protection controls are developed and documented.
- Network security management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support network security management operations.
- Responsibility and authority for the performance of network security management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.21.1 Layered Network Defenses
- 11.21.2 Guest Networks
- 11.21.3 Boundary Protection
- 11.21.4 Data Flow Enforcement: Access Control Lists (ACLs)
- 11.21.5 Deny Traffic by Default & Allow Traffic by Exception
- 11.21.6 Domain Name Service (DNS) Resolution
- 11.21.7 Safeguarding Data Over Open Networks
- 11.21.8 End-User Messaging Technologies
- 11.21.9 Remote Access
- 11.21.10 Work From Anywhere (WFA): Telecommuting Security
- 11.21.11 Endpoint Security Validation
- 11.21.12 Wireless Networking
- 11.21.13 DNS & Content Filtering
11.22 Physical & Environmental Security
The entity must minimize physical access to the entity's systems and data by addressing applicable physical security controls and ensuring that appropriate environmental controls are in place and continuously monitored to ensure equipment does not fail due to environmental threats.
Relevant SCF Control(s): PES-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The physical facility where the entity's systems reside is protected.
- The location or site of the facility where the system resides is planned considering physical and environmental hazards.
- For existing facilities, physical and environmental hazards are considered in the entity's risk management strategy.
- Physical security operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support physical security operations.
- Responsibility and authority for the performance of physical security-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.22.1 Physical Security Plan (PSP)
- 11.22.2 Zone-Based Physical Security
- 11.22.3 Physical Access Authorizations
- 11.22.4 Role-Based Physical Access
- 11.22.5 Physical Access Control
- 11.22.6 Physical Security of Offices, Rooms & Facilities
- 11.22.7 Monitoring Physical Access
- 11.22.8 Visitor Control
- 11.22.9 Equipment Siting & Protection
11.23 Data Privacy
The entity must align data privacy engineering decisions with the entity's overall data privacy strategy and industry-recognized leading practices to secure Personal Data (PD) that implements the concept of data privacy by design and by default.
Relevant SCF Control(s): PRI-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- An entity-wide privacy program plan that provides an overview of the agency’s privacy program is developed.
- Data privacy operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support data privacy operations.
- Responsibility and authority for the performance of data privacy-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.23.1 Reasonable Data Privacy Practices
- 11.23.2 Data Privacy Notice
- 11.23.3 Choice & Consent
- 11.23.4 Restrict Collection To Identified Purpose
- 11.23.5 Inventory of Personal Data (PD)
- 11.23.6 Data Subject Empowerment
- 11.23.7 Documenting Data Processing Activities
- 11.23.8 Data Subject Communications
11.24 Project & Resource Management
The entity must ensure that security-related projects have both resource and project/program management support to ensure successful project execution.
Relevant SCF Control(s): PRM-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- An entity-defined official is designated to manage the development, documentation and dissemination of the planning policy and procedures.
- Planning procedures facilitate the implementation of the planning policy and associated planning controls are developed and documented.
- Project & Resource Management (PRM) operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support PRM operations.
- Responsibility and authority for the performance of PRM-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.24.1 Strategic Plan & Objectives
- 11.24.2 Targeted Capability Maturity Levels
- 11.24.3 Allocation of Resources
- 11.24.4 Secure, Compliant & Resilient In Project Management
- 11.24.5 Secure, Compliant & Resilient Requirements Definition
- 11.24.6 Secure Development Life Cycle (SDLC) Management
11.25 Risk Management
The entity must ensure that the business unit(s) that own the assets and / or processes involved are made aware of and understand all applicable security, compliance and resilience-related risks. The security, compliance and resilience teams advise and educate on risk management matters, while it is the business units and other key stakeholders that ultimately own the risk.
Relevant SCF Control(s): RSK-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- A comprehensive strategy is developed to manage security, compliance and resilience risk to the entity's operations and assets, individuals and other entities associated with the operation and use of the entity's systems.
- The risk management strategy is implemented consistently across the entity.
- A senior entity position for Risk Management aligns security, compliance and resilience management processes with strategic, operational and budgetary planning processes.
- For existing facilities, physical and environmental hazards are considered in the entity's risk management strategy.
- Risk management operations are conducted according to documented policies, standards, procedures and/or other directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support risk management operations.
- Responsibility and authority for the performance of risk management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.25.1 Risk Framing
- 11.25.2 Risk Tolerance
- 11.25.3 Risk Threshold
- 11.25.4 Risk Appetite
- 11.25.5 Risk Identification
- 11.25.6 Risk Catalog
- 11.25.7 Risk Assessment
- 11.25.8 Risk Register
- 11.25.9 Risk Assessment Methodology
- 11.25.10 Risk Ranking
- 11.25.11 Risk Remediation
- 11.25.12 Risk Response
- 11.25.13 Compensating Countermeasures
- 11.25.14 Risk Treatment Plan
- 11.25.15 Supply Chain Risk Management (SCRM) Plan
- 11.25.16 Supply Chain Risk Assessment
- 11.25.17 Data Protection Impact Assessment (DPIA)
11.26 Secure Engineering & Architecture
The entity must align cybersecurity engineering and architecture decisions with the entity's overall technology architectural strategy and industry-recognized leading practices to secure networked environments.
Relevant SCF Control(s): SEA-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Secure engineering principles are defined.
- Data privacy engineering principles are defined.
- Architectural designs that promote effective security, compliance and resilience are identified.
- Systems engineering principles that promote effective security, compliance and resilience are identified.
- Identified architectural designs that promote effective security, compliance and resilience are employed.
- Identified systems engineering principles that promote effective security, compliance and resilience are employed.
- Secure Engineering & Architecture (SEA) operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support SEA operations.
- Responsibility and authority for the performance of SEA-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.26.1 Secure Engineering Principles
- 11.26.2 Achieving Resilience Requirements
- 11.26.3 Resilience Capabilities
- 11.26.4 Alignment With Enterprise Architecture
- 11.26.5 Technical Debt Reviews
- 11.26.6 Defense-In-Depth (DiD) Architecture
- 11.26.7 Clock Synchronization
11.27 Security Operations
The entity must ensure appropriate resources and a management structure exists to enable the delivery of cybersecurity, physical security and data privacy operations.
Relevant SCF Control(s): OPS-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Operations security controls to be employed to protect key entity information throughout the system development life cycle are defined.
- Operations security controls are employed to protect key entity information throughout the system development life cycle.
- Security operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support security operations.
- Responsibility and authority for the performance of security operations-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.27.1 Standardized Operating Procedures (SOP)
- 11.27.2 Security Concept Of Operations (CONOPS)
- 11.27.3 Service Delivery (Business Process Support)
11.28 Security Awareness & Training
The entity must develop a security, compliance and resilience-minded workforce through continuous education activities and practical exercises.
Relevant SCF Control(s): SAT-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- A security, compliance and resilience workforce development and improvement program is established.
- The security, compliance and resilience education and awareness program is entity-wide.
- Security literacy training is provided to system users per an entity-defined frequency after initial training.
- Security Awareness & Training (SAT) operations are conducted according to documented policies, standards and procedures.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support SAT operations.
- Responsibility and authority for the performance of SAT-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.28.1 Secure, Compliant & Resilient-Minded Workforce
- 11.28.2 Secure, Compliant & Resilient Awareness Training
- 11.28.3 Role-Based Secure, Compliant & Resilient Training
11.29 Technology Development & Acquisition
The entity must ensure that security, compliance and resilience principles are implemented into any products/solutions, either developed internally or acquired, to make sure that the concepts of “least privilege” and “least functionality” are incorporated.
Relevant SCF Control(s): TDA-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- A system and services acquisition policy is developed and documented.
- System and services acquisition procedures to facilitate the implementation of the system and services acquisition policy and associated system and services acquisition controls are developed and documented.
- Acquisition strategies, contract tools and procurement methods are implemented to:
- Identify supply chain risks;
- Protect against supply chain risks; and
- Mitigate supply chain risks.
- Technology Development & Acquisition (TDA) operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support TDA operations.
- Responsibility and authority for the performance of TDA-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.29.1 Technology Development & Acquisition
- 11.29.2 Product Management
- 11.29.3 DevSecOps
- 11.29.4 Minimum Viable Product (MVP) Security Requirements
- 11.29.5 Development Methods, Techniques & Processes
- 11.29.6 Product Testing & Reviews
- 11.29.7 Software Bill of Materials (SBOM)
- 11.29.8 Developer Architecture & Design
- 11.29.9 Secure Software Development Practices (SSDP)
- 11.29.10 Criticality Analysis
- 11.29.11 Threat Modeling
- 11.29.12 Software Design Review
- 11.29.13 Secure Development Environments
- 11.29.14 Access to Program Source Code
11.30 Third-Party Management
The entity must ensure that security, compliance and resilience risks associated with third-parties are minimized and enable measures to sustain operations should a third-party become compromised, untrustworthy or defunct.
Relevant SCF Control(s): TPM-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Security requirements to protect against supply chain risks to the system, system components, or system services and to limit the harm or consequences from supply chain-related events are defined.
- Cybersecurity and data protection functional requirements, descriptions and criteria are included explicitly or by reference using in the acquisition contract for the system, system component or system service.
- Requirements for protecting security, compliance and resilience documentation, descriptions and criteria are included explicitly or by reference using in the acquisition contract for the system, system component or system service.
- Strength of mechanism requirements, descriptions and criteria are included explicitly or by reference using in the acquisition contract for the system, system component or system service.
- Cybersecurity and data protection assurance requirements, descriptions and criteria are included explicitly or by reference using in the acquisition contract for the system, system component or system service.
- Controls needed to satisfy the security, compliance and resilience requirements, descriptions and criteria are included explicitly or by reference using in the acquisition contract for the system, system component or system service.
- Third-party management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support third-party management operations.
- Responsibility and authority for the performance of third-party management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.30.1 Third-Party Inventories
- 11.30.2 Third-Party Criticality Assessments
- 11.30.3 Supply Chain Risk Management (SCRM)
- 11.30.4 Third-Party Services
- 11.30.5 Third-Party Risk Assessments & Approvals
- 11.30.6 Third-Party Processing, Storage and Service Locations
- 11.30.7 Third-Party Contract Requirements
- 11.30.8 Contract Flow-Down Requirements
- 11.30.9 Responsible, Accountable, Supportive, Consulted & Informed (RASCI) Matrix
- 11.30.10 Break Clauses
11.31 Threat Management
The entity must establish a capability to proactively identify and manage technology-related threats to the security, compliance and resilience of the entity's systems, data and business processes.
Relevant SCF Control(s): THR-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- A threat awareness program that includes a cross-entity information-sharing capability for threat intelligence is implemented.
- Sources of threat intelligence are defined.
- A risk assessment methodology is identified.
- Sources of threat intelligence are employed as part of a risk assessment to guide and inform:
- The development of the entity's systems and security architectures;
- The selection of security solutions;
- System monitoring activities;
- Threat hunting activities; and
- Response and recovery activities.
- Threat management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support threat management operations.
- Responsibility and authority for the performance of threat management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.31.1 Threat Intelligence Program
- 11.31.2 Threat Intelligence Feeds
- 11.31.3 Threat Intelligence Reporting
- 11.31.4 Threat Catalog
- 11.31.5 Threat Analysis
11.32 Vulnerability & Patch Management
The entity must proactively manage the risks associated with technical vulnerability management that includes ensuring good patch and change management practices are utilized.
Relevant SCF Control(s): VPM-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- An entity-wide vulnerability and patch management program is developed and implemented to proactively identify and remediation vulnerabilities.
- For system flaws, the time is specified in which to:
- Identify;
- Report; and
- Correct.
- Within the entity-specified time frame, system flaws are:
- Identified;
- Reported; and
- Corrected.
- Vulnerability & patch management operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support vulnerability & patch management operations.
- Responsibility and authority for the performance of vulnerability & patch management-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.32.1 Vulnerability & Patch Management Program (VPMP)
- 11.32.2 Vulnerability Remediation Process
- 11.32.3 Vulnerability Ranking
- 11.32.4 Software & Firmware Patching
- 11.32.5 Vulnerability Scanning
- 11.32.6 Breadth / Depth of Coverage
11.33 Web Security
The entity must address the risks associated with Internet-accessible technologies by hardening devices, monitoring system file integrity, enabling auditing and monitoring for malicious activities.
Relevant SCF Control(s): WEB-01
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- An enterprise-wide web management policy, as well as associated standards, controls and procedures exists.
- Web security operations are conducted according to documented policies, standards, procedures and/or other entity directives.
- Adequate resources (e.g., people, processes, technologies, data and/or facilities) are provided to support web security operations.
- Responsibility and authority for the performance of web security-related activities are assigned to designated personnel.
Subsections in the SCRMS
- 11.33.1 Strong Customer Authentication (SCA)
- 11.33.2 Secure Web Traffic
Due Care Activities
As described in Section 7, Control Set Determination, the Minimum Security Requirements (MSR) is a baseline determined by the entity’s Minimum Compliance Requirements (MCR) and Discretionary Security Requirements (DSR). While compliance-related activities are unique to the statutory, regulatory or contractual obligations of the entity, there are reasonable security, compliance and resilience capabilities that entities should implement, regardless of its size, industry or geography. These foundational practices are part of the SCF’s Cybersecurity Oversight, Resilience and Enablement (SCF CORE) Fundamentals baseline, designed to:
- Contain administrative, technical and physical safeguards for the protection of Technology Assets, Applications, Services and/or Data (TAASD); and
- Protect against any reasonable risks and threats.
From a due care perspective, an entity is expected to demonstrate conformity with the following practices:
12.1 Ability To Demonstrate Conformity
The entity must ensure it is able to demonstrate conformity with applicable security, compliance and resilience laws, regulations and/or contractual obligations.
Relevant SCF Control(s): CPL-01.3
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- A capability exists to demonstrate conformity with applicable security, compliance and resilience laws, regulations and/or contractual obligations.
- Personnel or roles to whom the assignment of being able to demonstrate conformity is assigned.
Conformity Assessment
The entity must conduct assessments to demonstrate conformity with applicable security, compliance and resilience laws, regulations and/or contractual obligations.
Relevant SCF Control(s): CPL-01.4
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Assessments are conducted to demonstrate conformity with applicable security, compliance and resilience laws, regulations and/or contractual obligations.
Secure, Compliant & Resilient Status Reporting
The entity must submit status reporting of its cybersecurity and/or data privacy program to applicable statutory and/or regulatory authorities, as required.
Relevant SCF Control(s): GOV-19
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The basis for confidence that implemented practices conform to applicable security, compliance and resilience controls, where the control implementation performs as intended is defined.
12.2 Non-Compliance Oversight
The entity must document and review instances of non-compliance with statutory, regulatory and/or contractual obligations to develop appropriate risk mitigation actions.
Relevant SCF Control(s): CPL-01.1
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Instances of non-compliance with statutory, regulatory and/or contractual obligations are:
- Documented, including the reason(s) for non-compliance;
- Formally-reviewed;
- Centrally-governed to maintain appropriate situational awareness; and
- Assigned to individuals or teams for remediation.
- Remediation plans for instances of non-compliance with statutory, regulatory and/or contractual obligations are documented.
Monitor Controls
The entity must compel data and/or process owners to monitor Technology Assets, Applications and/or Services (TAAS) under their control on an ongoing basis for applicable threats and risks, as well as to ensure security, compliance and resilience controls are operating as intended.
Relevant SCF Control(s): GOV-15.5
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Roles and responsibilities exist to compel data and/or process owners to monitor systems, applications and/or services under their control on an ongoing basis for applicable threats and risks, as well as to ensure cybersecurity / data privacy controls are operating as intended.
- Individual Contributor (IC) performance reviews cover how data and/or process owners monitor systems, applications and/or services under their control on an ongoing basis for applicable threats and risks, as well as to ensure cybersecurity / data privacy controls are operating as intended.
Periodic Audits
The entity must conduct periodic audits of security, compliance and resilience controls to evaluate conformity with its documented policies, standards and procedures.
Relevant SCF Control(s): CPL-02.2
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The entity conducts periodic, formal audits of security, compliance and resilience controls for conformity with the entity's policies, standards and procedures.
- Personnel or roles to whom the assignment conformity assessments are assigned.
Functional Review Of Secure, Compliant & Resilient Controls
The entity must regularly review Technology Assets, Applications and/or Services (TAAS) for adherence to its security, compliance and resilience policies and standards.
Relevant SCF Control(s): CPL-03.2
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Controls are assessed in the system and its environment of operation per an entity-defined assessment frequency to determine the extent to which the controls are implemented correctly, operating as intended and producing the desired outcome with respect to meeting established security and/or data privacy requirements.
- A control assessment report is produced that documents the results of the assessment.
- The results of the control assessment are provided to individuals or roles.
Third-Party Scope Review
The entity must perform recurring validation of the Responsible, Accountable, Supportive, Consulted & Informed (RASCI) matrix, or similar documentation, to ensure security, compliance and resilience control assignments accurately reflect current business practices, compliance obligations, technologies and stakeholders.
Relevant SCF Control(s): TPM-05.5
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Recurring validation of the Responsible, Accountable, Supportive, Consulted & Informed (RASCI) matrix, or similar documentation, is performed to ensure cybersecurity / data privacy control assignments accurately reflect current business practices, compliance obligations, technologies and stakeholders.
- Processes, methods and techniques to monitor security requirement compliance by external service providers on an ongoing basis are implemented.
Review of Third-Party Services
The entity must monitor, regularly review and assess External Service Providers (ESPs) for compliance with established contractual requirements for security, compliance and resilience controls.
Relevant SCF Control(s): TPM-08
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The frequency at which to assess and review the supply chain-related risks associated with suppliers or contractors and the systems, system components or system services they provide is defined.
- The supply chain-related risks associated with suppliers or contractors and the systems, system components or system services they provide are assessed and reviewed per an entity-defined frequency.
Managing Changes To Third-Party Services
The entity must control changes to services by suppliers, taking into account the criticality of business Technology Assets, Applications, Services and/or Data (TAASD) that are in scope by the third-party.
Relevant SCF Control(s): TPM-10
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Affected third-parties are identified through change control practices.
- Provided services are assessed for impact from proposed changes.
- Recurring reviews are performed of third-party provided services against existing contract requirements.
- Discrepancies in services provided and/or geolocation of provided services are evaluated for impact to the entity’s operations.
12.3 Measures of Performance
The entity must develop, report and monitor security, compliance and resilience program measures of performance.
Relevant SCF Control(s): GOV-05
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Cybersecurity and data privacy measures of performance are:
- Developed; and
- Monitored.
- The results of security, compliance and resilience measures of performance are reported.
Key Performance Indicators
(KPIs)
The entity must develop, report and monitor Key Performance Indicators (KPIs) to assist executive leadership in performance monitoring and trend analysis of the security, compliance and resilience program.
Relevant SCF Control(s): GOV-05.1
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Key Performance Indicators (KPIs) are developed to assist executive leadership in performance monitoring and trend analysis of specific aspects of the entity's security, compliance and resilience program.
Key Risk Indicators
(KRIs)
The entity must develop, report and monitor Key Risk Indicators (KRIs) to assist executive leadership in performance monitoring and trend analysis of the security, compliance and resilience program.
Relevant SCF Control(s): GOV-05.2
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Key Risk Indicators (KRIs) are developed to assist executive leadership in performance monitoring and trend analysis of specific aspects of the entity's security, compliance and resilience program.
12.4 Incident Response Testing
The entity must formally test incident response capabilities through realistic exercises to determine the operational effectiveness of those capabilities.
Relevant SCF Control(s): IRO-06
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The frequency at which to test the effectiveness of the incident response capability for the system is defined.
- Tests used to test the effectiveness of the incident response capability for the system are defined.
- The effectiveness of the incident response capability is tested per an entity-defined frequency.
- Intrusion-monitoring tools and mechanisms are tested frequently.
Monitoring For Indicators of Compromise
(IOC)
The entity must monitor for and alert on Indicators of Compromise (IoC).
Relevant SCF Control(s): BCD-04
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- Anomalous or suspicious behavior is defined.
- IOC are defined.
- Sources that provide Indicators of Compromise (IOC) are defined.
- IOC provided by sources are discovered.
- IOC provided by sources are collected.
- Unauthorized use of the system is identified through techniques and methods.
Contingency Plan Testing & Exercises
The entity must conduct tests and/or exercises to evaluate the contingency plan's effectiveness and its readiness to execute the plan.
Relevant SCF Control(s): BCD-04
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The frequency of testing the contingency plan for the system is defined.
- Tests for determining the effectiveness of the contingency plan are defined.
- Tests for determining readiness to execute the contingency plan are defined.
- The contingency plan for the system is tested frequently.
12.5 Commitment To Continual Improvements
The entity must commit appropriate resources needed for continual improvement of the entity's security, compliance and resilience program, including:
- Staffing;
- Budget;
- Processes; and
- Technologies.
Relevant SCF Control(s): GOV-01.3
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The entity commits appropriate financial resources needed for continual improvement of the entity's cybersecurity & data privacy program.
Status Reporting To Governing Body
The entity must provide governance oversight reporting and recommendations to those entrusted to make executive decisions about matters considered material to its security, compliance and resilience program.
Relevant SCF Control(s): GOV-01.2
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- The executive steering committee, or advisory board, makes executive decisions about matters considered material to the entity's security, compliance and resilience program.
12.6 Quality Management System (QMS)
The entity must govern a Quality Management System (QMS) to ensure security, compliance and resilience processes conform with applicable statutory, regulatory and/or contractual obligations.
Relevant SCF Control(s): GOV-18
Note
To demonstrate conformity with this requirement, in addition to relevant policies, standards and procedures, the entity needs sufficient evidence to support control effectiveness claims that can prove:
- A Quality Management System (QMS) is implemented to ensure security, compliance and resilience processes conform with applicable statutory, regulatory and/or contractual obligations.
Demonstrating Assurance To Stakeholders
Regardless of the industry, there is a definitive need for a third-party verified certification that assesses tailored security, compliance and resilience controls that could impact an entity and its supply chain stakeholders. The SCRMS was designed to integrate with the SCF’s conformity assessment program that is designed to provide third-party validation of an entity’s security, compliance and resilience controls.
13.1 SCF Conformity Assessment Program (SCF CAP)
The Secure Controls Framework Conformity Assessment Program (SCF CAP) can be used to demonstrate assurance to stakeholders, since it is an entity-level conformity assessment.
The SCF CAP is designed to utilize tailored cybersecurity and privacy controls that specifically address the applicable statutory, regulatory and contractual obligations an Organization Seeking Assessment (OSA) is required to comply with. By using the metaframework nature of the SCF, an OSA is able to perform conformity assessment that spans multiple cybersecurity and privacy-specific laws, regulations and frameworks.
The SCF CAP is focused on using the SCF as the control set to provide a company-level certification. While the SCF CAP shares some similarities with other existing, single-focused certifications (e.g., ISO 27001, CMMC, FedRAMP, etc.), the SCF CAP is unique in its metaframework approach to covering security, compliance and resilience requirements that span multiple laws, regulations and frameworks.
As security, compliance and resilience operations are multi-faceted, the SCF CAP is designed to ensure that assessed controls reflect the real-world requirements faced by the OSA from a statutory, regulatory and contractual perspective. An assessment that only covers a part of an OSA’s security, compliance and resilience program results in an inaccurate and incomplete report on the OSA’s overall security posture, providing a false sense of security to the OSA.
The SCF CAP is designed for cybersecurity & privacy practitioners by cybersecurity & data privacy practitioners. This concept is based on the need within the industry for a tailored conformity assessment solution that is capable of addressing several key considerations:
- View compliance as a natural by-product of secure practices;
- Scale to address multifaceted operational requirements (e.g., laws, regulations and frameworks);
- Acknowledge the stated risk tolerance of the OSA since not all entities have the same risk tolerance;
- Minimize the risk of “gaming” the certification process that provides no useful insights into the security posture of the OSA;
- Utilize technology to make the assessment process more efficient to drive down labor-related assessment costs; and
- Leverage existing industry recognized practices, where possible.
13.2 SCF Certification Options
To learn more about SCF certification options, please contact the SCF.
Earning a SCF Certified™ conformity designation is meant to signify an accomplishment, rather than be viewed as a “participation ribbon” that has little practical value for the OSA or stakeholders in the OSA’s supply chain to understand the OSA’s security posture.
Contributors & Errata
Contributors
The Secure Controls Framework Council wants to thank these individuals for their contributions in the development and refinement of the Secure, Compliant & Resilient Management System (SCRMS):
Errata
2026.3
- Rebranded from “Security, Compliance & Resilience” to “Secure, Compliant & Resilient” to align with the Secure, Compliant & Resilient Initiative (SCR Initiative).
- Corrected a typographical error in section 1.1.
2026.2
- Updated URLs.
- Updated the People, Processes, Technology, Data, Facilities & Artificial Intelligence (PPTDF-AI) section.
2026.1
- Initial documentation published.
Annexes
The SCRMS includes four annexes with supporting reference material. Each one is summarized below, and the full content is in the SCRMS PDF.
- Annex 1: Applicable SCF Controls. The SCF controls mapped into the SCRMS for the due diligence and due care activities in Sections 11 and 12. These controls are a starting point for tailoring, and they appear in the “SCF SCRMS” column on the main tab of the free SCF download.
- Annex 2: Adequate Security. How business planning and analysis lead to stakeholder and system security requirements, what makes a system “secure,” and why a “system of systems” view matters when systems depend on each other.
- Annex 3: Defensible Evidence. The types of evidence an entity should plan for to prove secure, compliant and resilient capabilities, grouped as governance, risk, security capability, compliance, resilience and assurance evidence.
- Annex 4: Planning For Resistance. CISO-focused guidance for building a defensible record when leadership declines to fund needed capabilities, from strategy documents and risk registers to formal risk acceptance and escalation paths.
